| While configuring the SNMP, the interface should be in the management VDOM to get the response from the Firewall to the SNMP Monitoring tool. This article will provide an example and assume that the SNMP is connected to a non-Management VDOM. 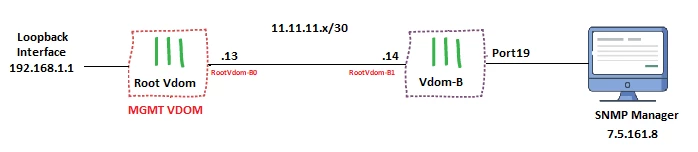
Configuration: Global Mode Configuration.
- Configure Intervdom Links between Root and VDOM-B.
config global config system vdom-link
edit "RootVdom-B"
next
end
config system interface
edit "RootVdom-B0"
set vdom "root"
set ip 11.11.11.13 255.255.255.252
set allowaccess ping https ssh http fgfm
set type vdom-link
set description "VDOM LINK TO Vdom-B"
set snmp-index 60
next
edit "RootVdom-B1"
set vdom "Vdom-B"
set ip 11.11.11.14 255.255.255.252
set allowaccess ping https ssh http fgfm
set type vdom-link
set description "VDOM LINK TO ROOT"
set snmp-index 61
next
end -
Configure the SNMP and set the source IP for the Loopback interface as below: config system snmp community
edit 1
set name "public"
config hosts
edit 1
set source-ip 192.168.1.1
set ip 7.5.161.8 255.255.255.255
next
end
next
end Root VDOM Configuration. - Configure the Loopback Interface and enable SNMP and Ping.
config System Interface
edit "SNMP_LO"
set vdom "root"
set ip 192.168.1.1 255.255.255.0
set allowaccess ping https snmp http fgfm
set type loopback
set description "SNMP LOOPBACK"
set role lan
set snmp-index 62
next -
Configure the Firewall policies from the SNMP Loopback interface to the VDOM Link: config firewall policy
edit 1
set name "SNMP_LB TO SNMP_Serv"
set srcintf "SNMP_LO"
set dstintf "RootVdom-B0"
set action accept
set srcaddr "all"
set dstaddr "all"
set schedule "always"
set service "ALL"
set logtraffic all
set comments "SNMP_LB TO SNMP_Serv"
next
edit 2
set name "Root_To_SNMPLO"
set srcintf "RootVdom-B0"
set dstintf "SNMP_LO"
set action accept
set srcaddr "all"
set dstaddr "all"
set schedule "always"
set service "ALL"
set logtraffic all
set comments "Root_To_SNMPLO"
next
end -
Configure static route toward the SNMP Manager. config router static
edit 3
set dst 7.5.161.0 255.255.255.0
set device "RootVdom-B0"
next
end VDOM-B Configuration. - Configure a static route back to Root VDOM.
config router static
edit 11
set dst 192.168.1.1 255.255.255.255
set gateway 11.11.11.13
set device "RootVdom-B1"
next -
Configure a Firewall policy to allow communication between Port19 and Intervdom Link. config firewall policy
edit 21
set name "PORT19SNMP_TO_ROOT"
set srcintf "port19"
set dstintf "RootVdom-B1"
set action accept
set srcaddr "all"
set dstaddr "all"
set schedule "always"
set service "ALL"
set logtraffic all
set comments " (Copy of Lo_To_Rootvdom)"
next
edit 22
set name "Root_To_SNMP_PORT19"
set srcintf "RootVdom-B1"
set dstintf "port19"
set action accept
set srcaddr "all"
set dstaddr "all"
set schedule "always"
set service "ALL"
set logtraffic all
set comments " to port19"
next
end | 




