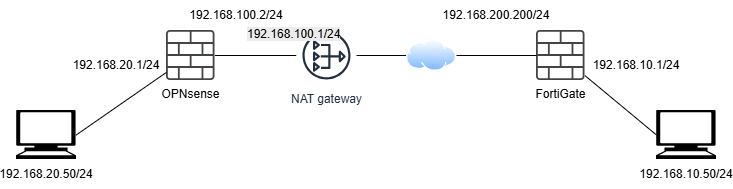
The network diagram and IP addresses that will be used on this test:
In FortiGate, this configuration can be found under VPN - VPN Tunnels
In OPNsense, IPsec configuration utilizes the VPN settings under VPN - IPsec - Connections and Pre-Shared Keys.
Step 1 FortiGate setup:
Interface setup facing internet:
config system interface
    edit "port2"
        set vdom "root"
        set ip 192.168.200.200 255.255.255.0
        set allowaccess ping
        set type physical
        set alias "wan"
        set lldp-reception enable
        set role wan
        set snmp-index 2
    next
end
Interface setup facing internal network:
config system interface
    edit "port3"
        set vdom "root"
        set ip 192.168.10.1 255.255.255.0
        set allowaccess ping
        set type physical
        set device-identification enable
        set lldp-transmission enable
        set role lan
        set snmp-index 3
    next
end
Static route:
config router static
    edit 1
        set gateway 192.168.200.1
        set device "port2"
    next
end
Firewall Address setup:
config firewall address
    edit "ToOpnsense_local_subnet"
        set comment "FortiGate_LAN_Subnet"
        set allow-routing enable
        set subnet 192.168.10.0 255.255.255.0
    next
end
config firewall address
    edit "ToOpnsense_remote_subnet"
        set comment "OPNsense_LAN_Subnet"
        set allow-routing enable
        set subnet 192.168.20.0 255.255.255.0
    next
end
VPN setup:
config vpn ipsec phase1-interface
    edit "ToOpnsense"
        set type dynamic
        set interface "port2"
        set ike-version 2
        set peertype any
        set net-device disable
        set proposal aes128-sha256 aes256-sha256 aes128gcm-prfsha256 aes256gcm-prfsha384 chacha20poly1305-prfsha256
        set comments "VPN: ToOpnsense -- Created by VPN wizard"
        set dhgrp 20 21
        set wizard-type dialup-fortigate
        set transport udp
        set psksecret ENC Mt/w+BHXXx/0gp8cNY6iY4eQvNn
    next
end
Note: Since OPNsense is behind NAT, the FortiGate is configured as a dial-up responder using 'set type dynamic'. The OPNsense peer initiates the IKE negotiation toward the FortiGate.
config vpn ipsec phase2-interface
    edit "ToOpnsense"
        set phase1name "ToOpnsense"
        set proposal aes128-sha1 aes256-sha1 aes128-sha256 aes256-sha256 aes128gcm aes256gcm chacha20poly1305
        set dhgrp 20 21
        set src-addr-type name
        set dst-addr-type name
        set src-name "ToOpnsense_local"
        set dst-name "ToOpnsense_remote"
    next
end
Firewall policy:
config firewall policy
    edit 1
        set name "vpn_ToOpnsense_local"
        set srcintf "port3"
        set dstintf "ToOpnsense"
        set action accept
        set srcaddr "ToOpnsense_local_subnet"
        set dstaddr "ToOpnsense_remote_subnet"
        set schedule "always"
        set service "ALL"
        set comments "Allow Traffic from FortiGate to OPNsense LAN"
    next
    edit 2
        set name "vpn_ToOpnsense_remote"
        set srcintf "ToOpnsense"
        set dstintf "port3"
        set action accept
        set srcaddr "ToOpnsense_remote_subnet"
        set dstaddr "ToOpnsense_local_subnet"
        set schedule "always"
        set service "ALL"
        set comments "Allow Traffic from OPNsense to Fortigate LAN"
    next
end
Step 2 - OPNsense setup:
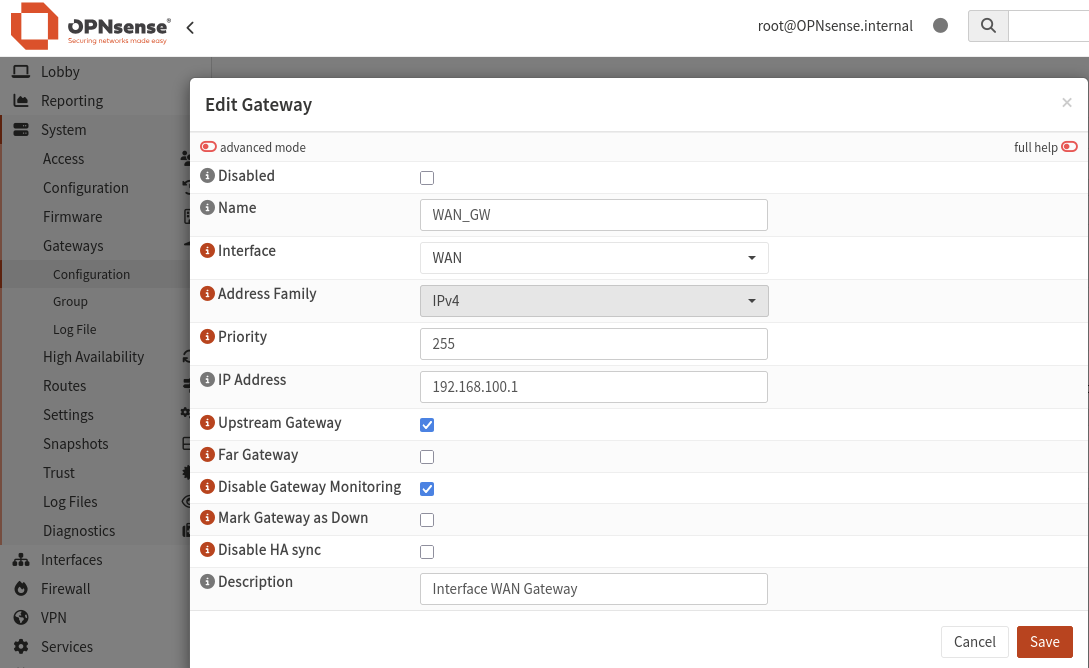
Default Gateway:
Go to System -> Gateways -> Configuration -> Add.
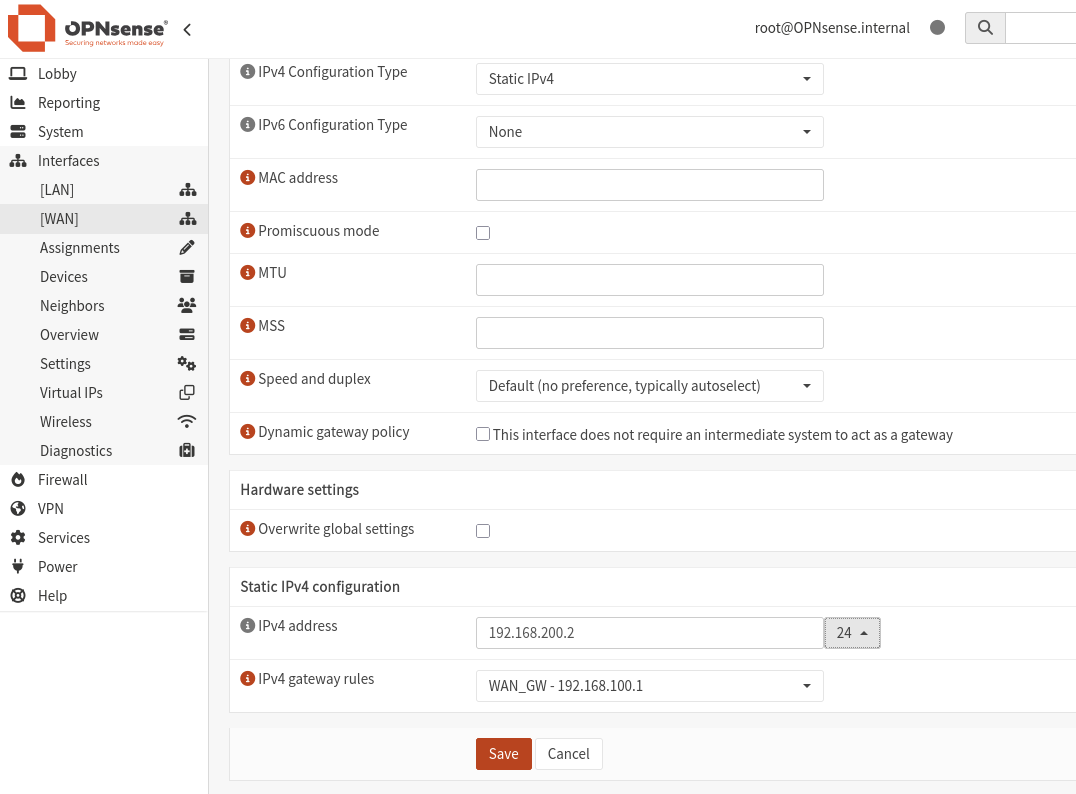
Interface setup facing internet:
Lock the interface to avoid any unintentional deletion.
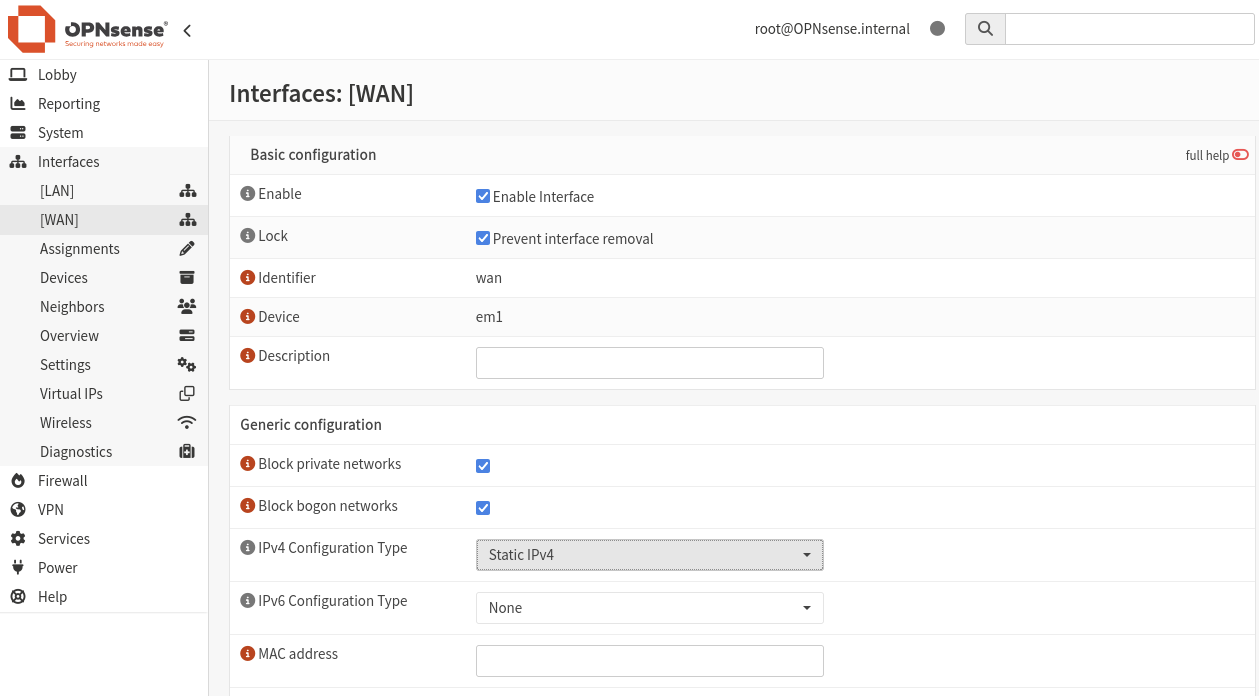
Configure static IPv4 and select IPv4 gateway:
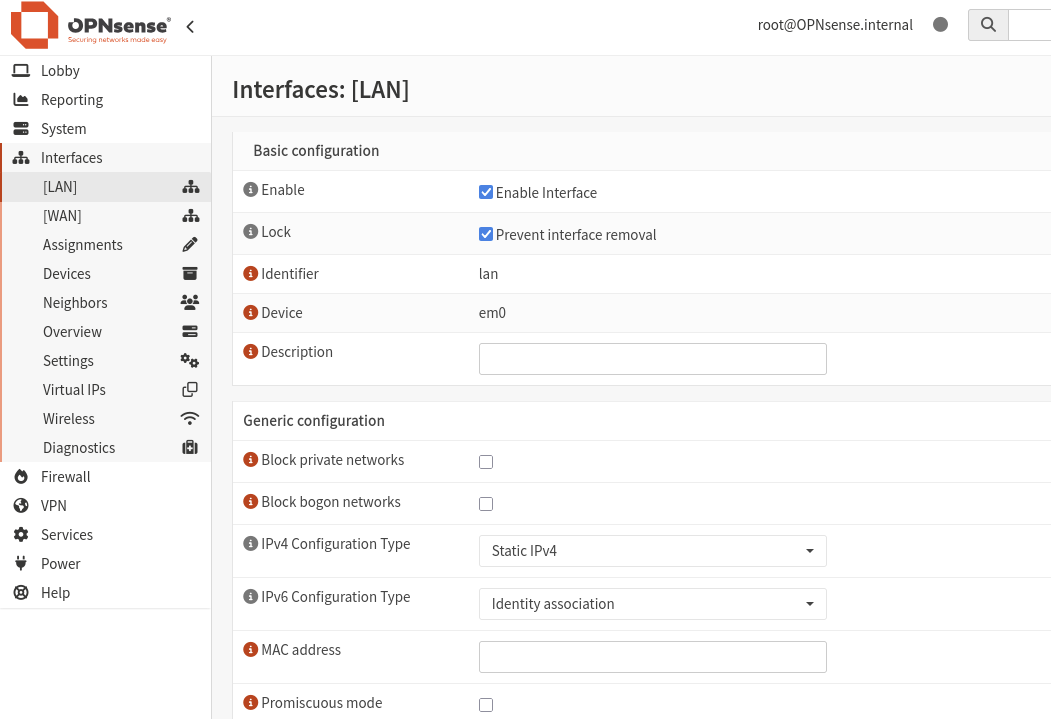
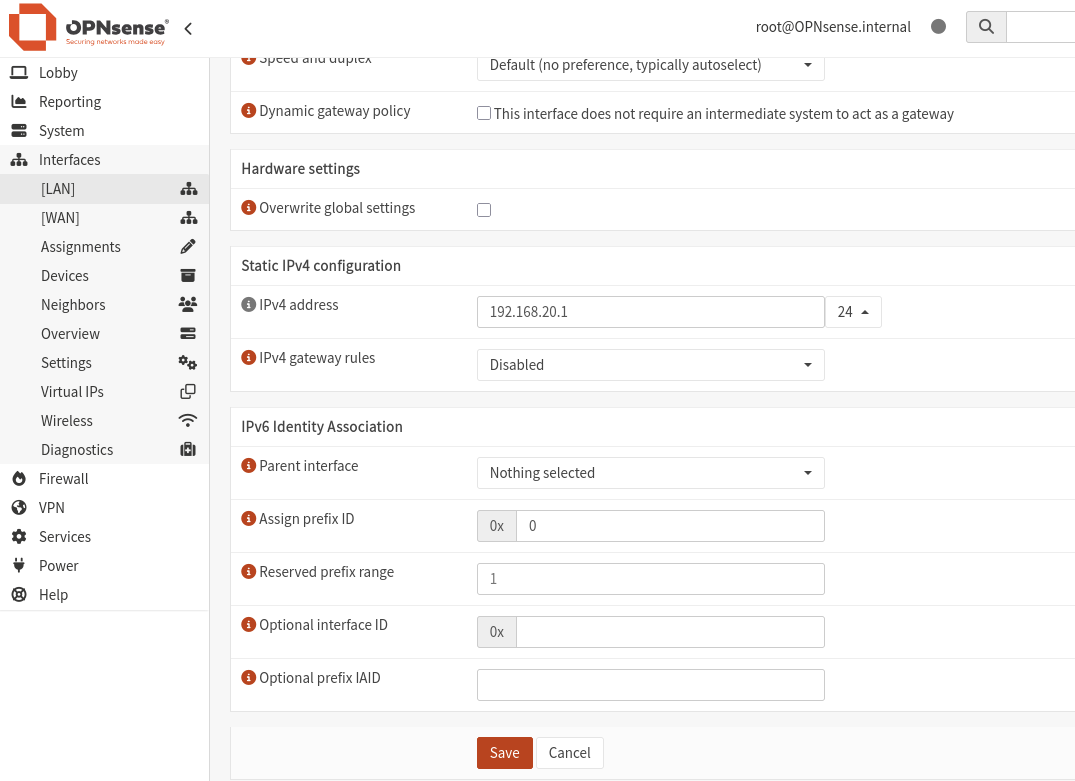
Interface setup facing internal LAN:
Lock the interface to avoid any unintentional deletion.
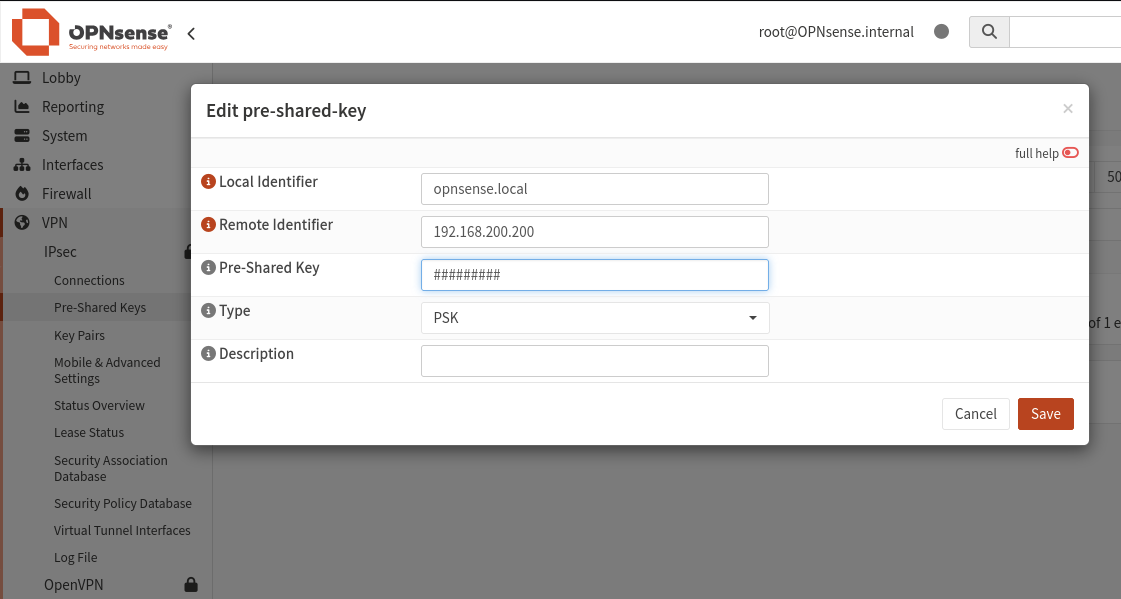
VPN setup pre-shared key:
The first step is to create a pre-shared key and identifiers that will be later linked to the correct IPsec tunnel under VPN -> IPsec -> Pre-Shared Keys -> Add. This key should match with the FortiGate pre-shared key setup under the phase-1 interface.
VPN setup IPsec tunnel:
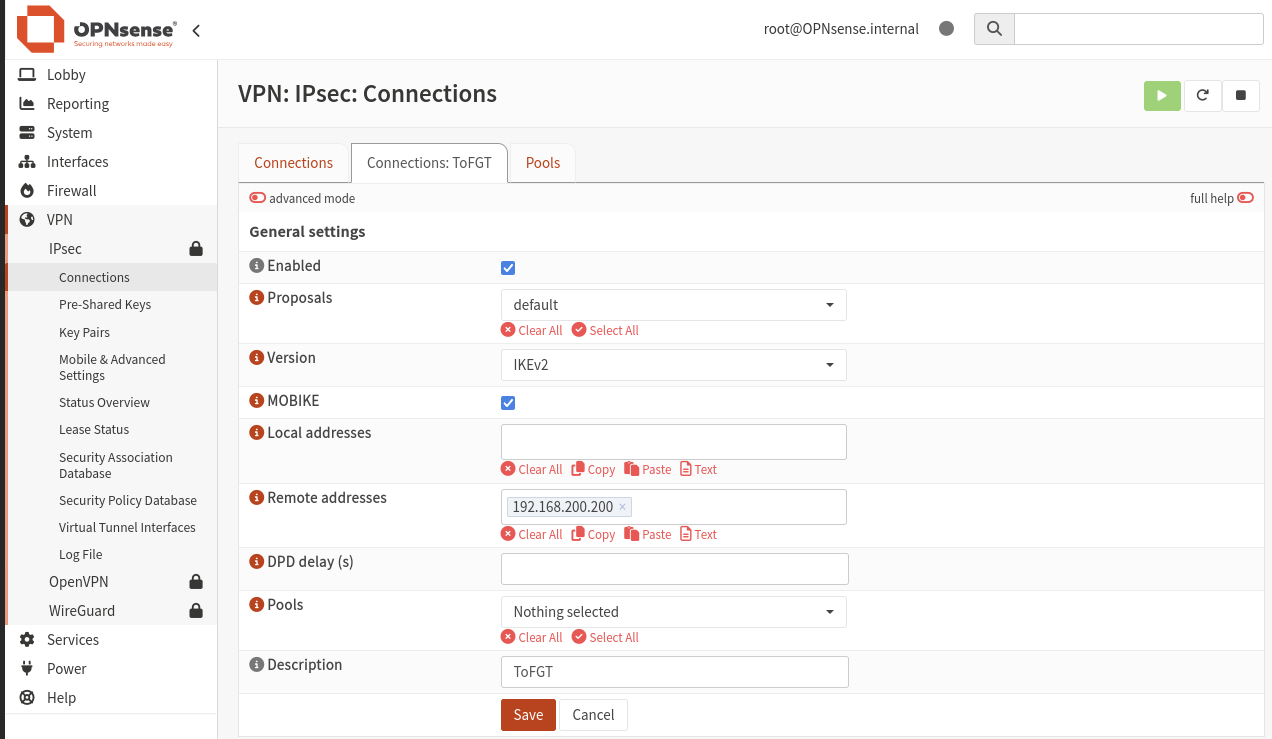
The second step is to create an IPsec tunnel with all settings that should match FortiGate. For testing purposes, default values are set up but can be changed according to the deployment needs.
Navigate to VPN -> IPsec -> Connections and select +.
VPN setup local authentication:
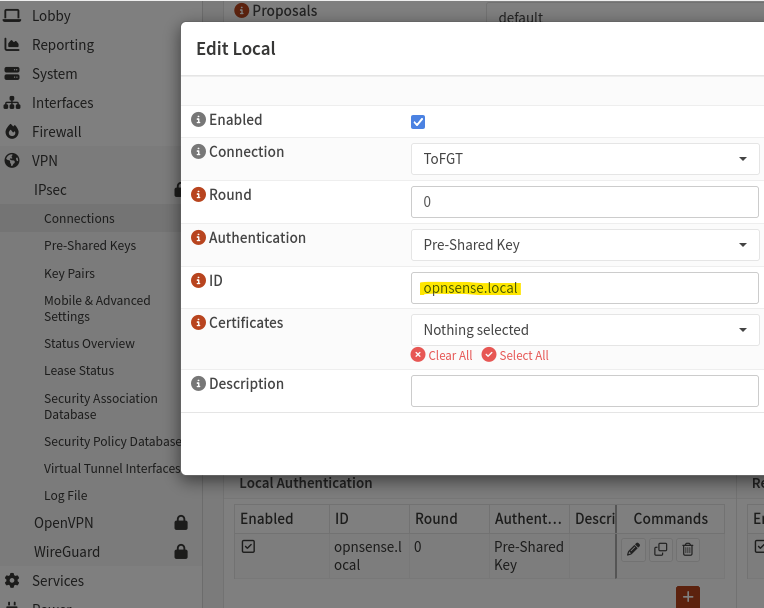
Local authentication:
Connection: ToFGT (the same name configured under General Settings). Auth Method: Pre-Shared Key. Identifier (Id): opnsense.local (Must match Step 1 & FortiGate Peer ID if this is configured in FortiGate. In this example, it is not necessary because FortiGate accepts any peer ID: peertype any.)
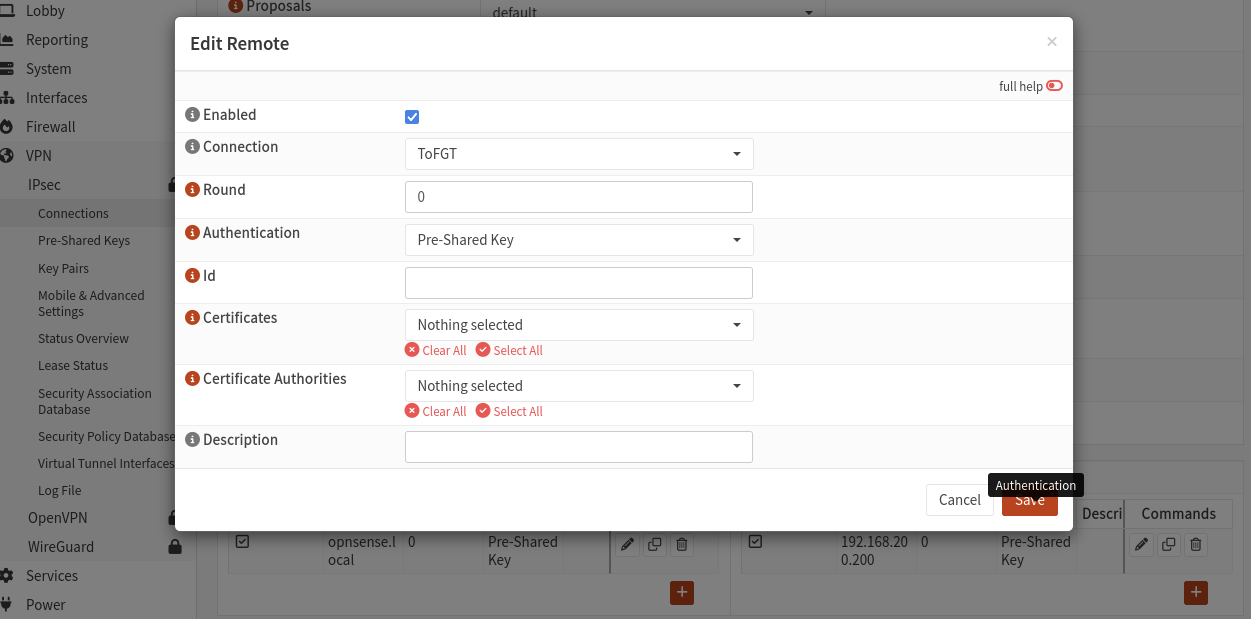
 VPN setup remote authentication:
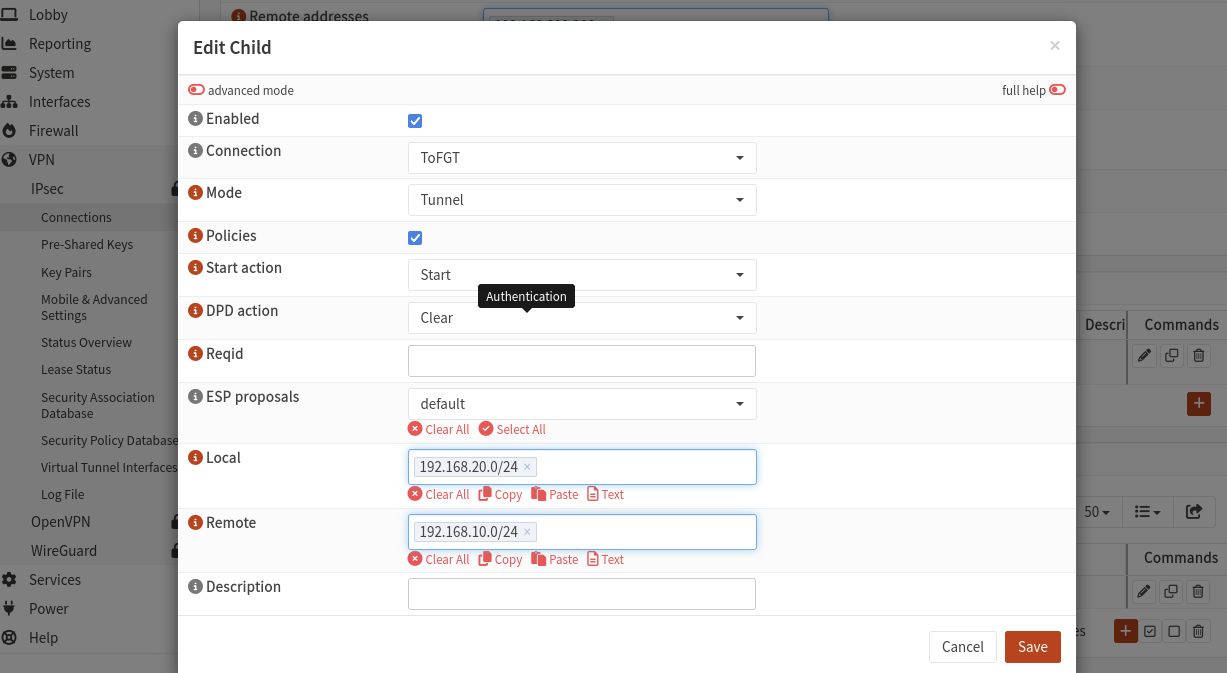
Phase2 selectors (FortiGate terminology) / Children (OPNsense terminology):
Firewall policy:
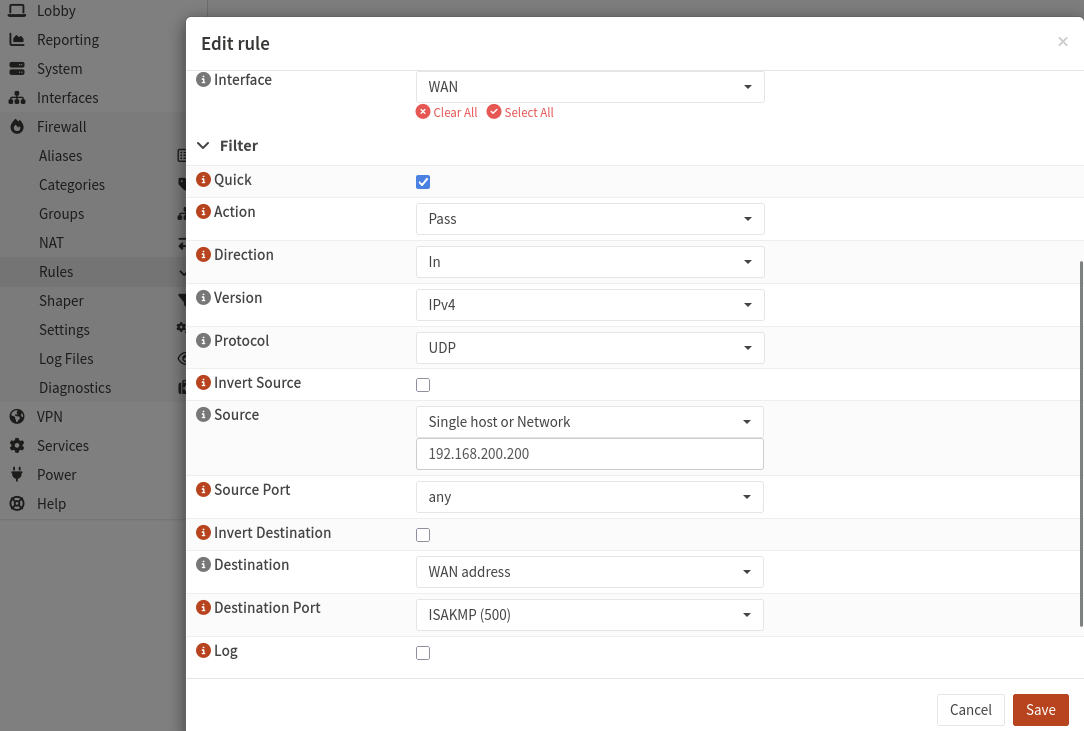
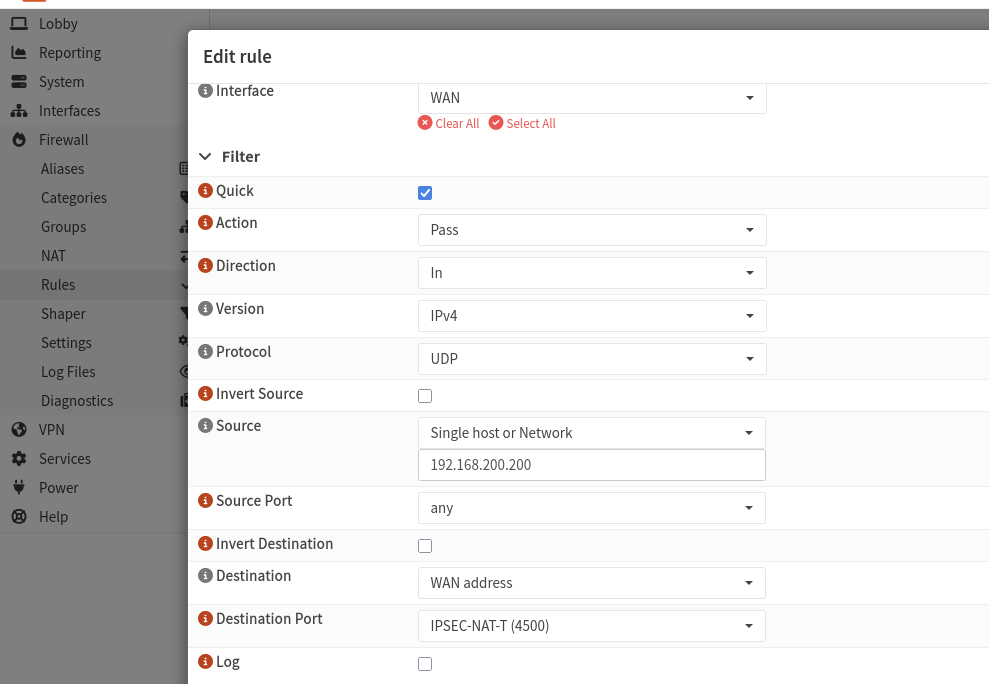
OPNsense needs a specific firewall rule to allow isakmp (UDP port 500) and ipsec-nat-t traffic (UDP port 4500). FortiGate, on the other hand, makes this configuration automatically once IPsec tunnel is configured.
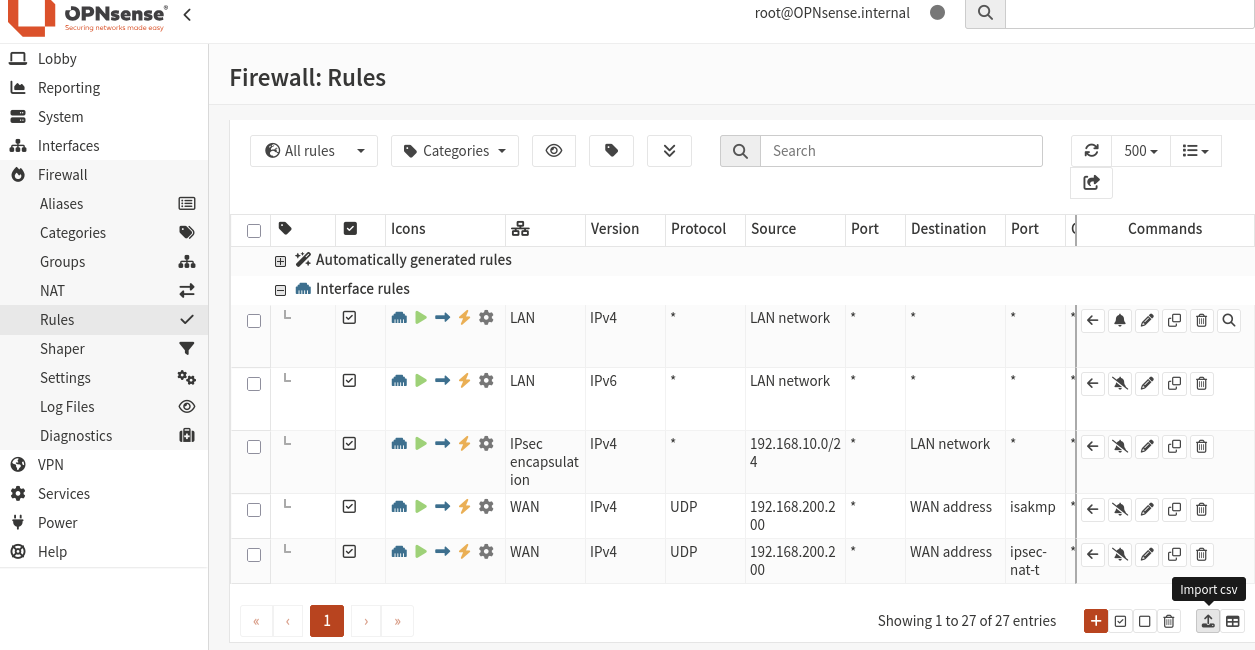
Final ruleset:
For LAN to LAN traffic, only one rule is needed to allow remote traffic to enter OPNsense. The initial firewall rule is not needed because OPNsense comes with a pre-configured firewall policy that allows traffic from LAN to all other interfaces, including IPsec.
Testing connectivity:
Ping from PC behind FortiGate toward OPNsense subnet:
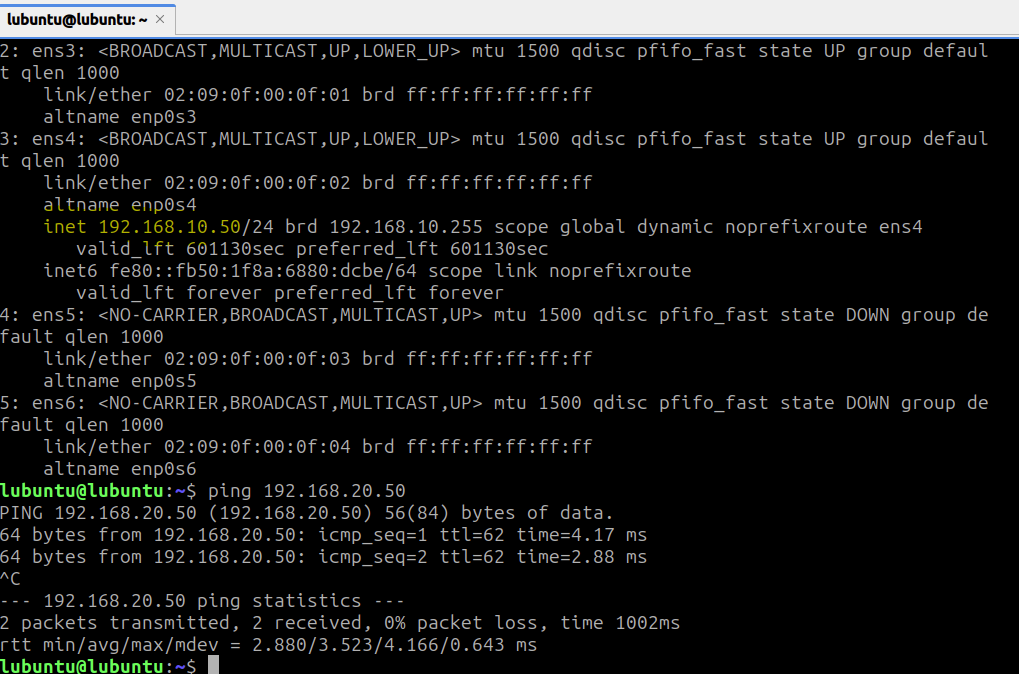
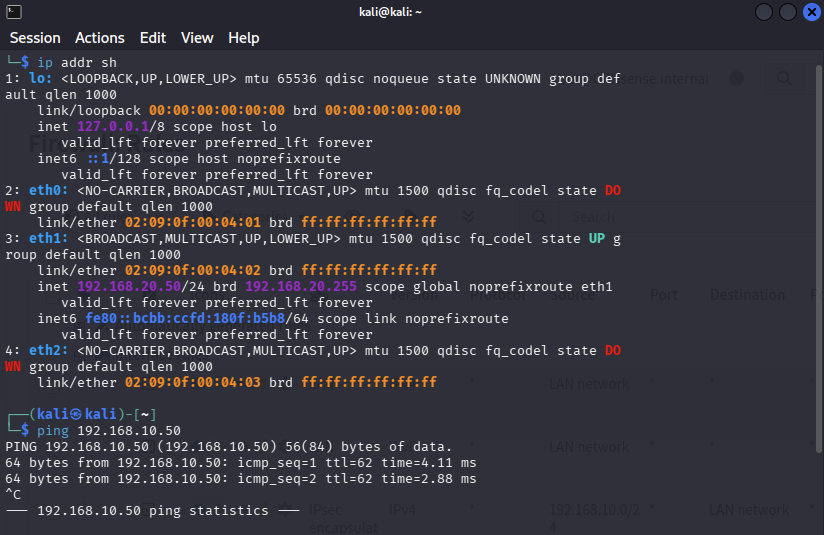
Ping from PC behind OPNsense toward FortiGate subnet:
Check tunnel summary on FortiGate:
VPN-to-OPNSENSE # diagnose vpn ike gateway list

vd: root/0
name: ToOpnsense_0
version: 2
interface: port2 4
addr: 192.168.200.200:4500 -> 192.168.200.1:9617
tun_id: 192.168.200.1/::10.0.0.2
remote_location: 0.0.0.0
network-id: 0
transport: UDP
created: 5593s ago
peer-id: opnsense.local
peer-id-auth: no
nat: peer
pending-queue: 0
PPK: no
IKE SA: created 1/1  established 1/1  time 0/0/0 ms
IPsec SA: created 1/3  established 1/2  time 0/0/0 ms

  id/spi: 1 d43dceb898872d43/331f12abe47f83ee
  direction: responder
  status: established 5593-5593s ago = 0ms
  proposal: aes128-sha256
  child: no
  SK_ei: 9a5128224d0dcf10-1aa16b8604087745
  SK_er: 9de89da7af0f9f3f-86ea1c7162ff1e7d
  SK_ai: cbc6999dcea2db13-28b958ce408afb9f-fdba872438d5cd4f-6843cf03cc1d5643
  SK_ar: 5896096fa90d8a87-7a49bb0d62bcee28-be952d66c0545178-fead0794f3c4b1bd
  PPK: no
  message-id sent/recv: 0/5
  QKD: no
  PQC-KEM (IKE): no
  PQC-KEM (all IPsec): no
  lifetime/rekey: 86400/80536
  DPD sent/recv: 00000000/00000000
  peer-id: opnsense.local
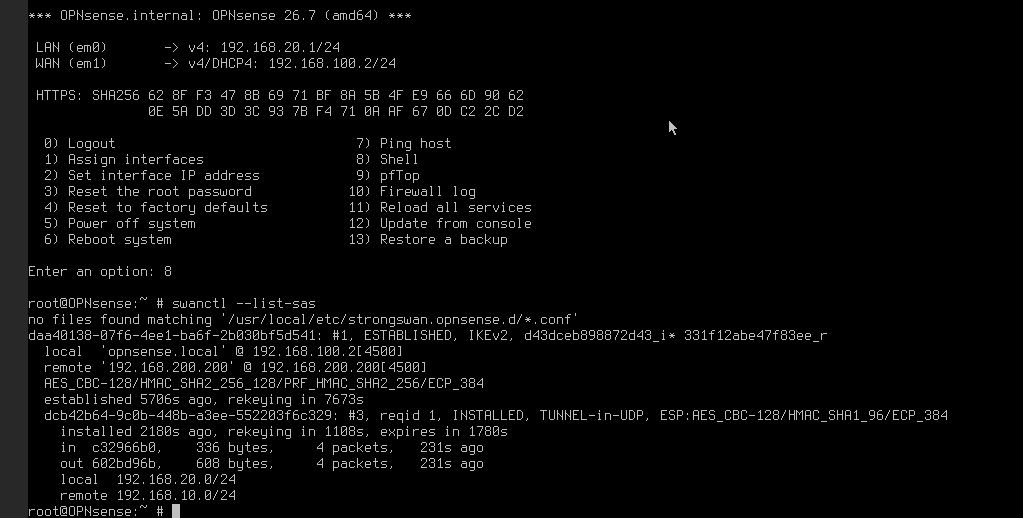
Check tunnel summary on OPNsense:
 |