


Technical Tip: Configuring FortiGate to inspect HTTP and HTTPS traffic over non-standard ports in 7.0 Forti OS
| Description | This article describes how to apply UTM features.
This configuration will ensure that the FortiGate is scanning HTTP/HTTPS traffic over non-standard ports (for example 8090,8888 etc..) along with standard port 80/443. |
| Scope | To access the web site which is hosting on the non standard port e.g:- http or https://example.com:8090 (port 8090 is the custom port) in this case UTM profile will not scan the traffic even though its enabled on the firewall policy. |
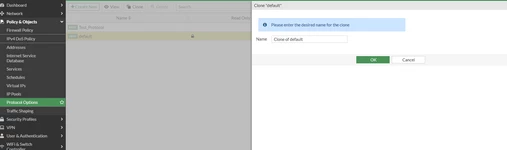
| Solution | 1) Go to Policy & objects and create clone of the default profile.
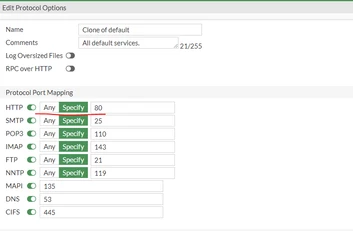
In clone of default profile we have default port 80 for HTTP.
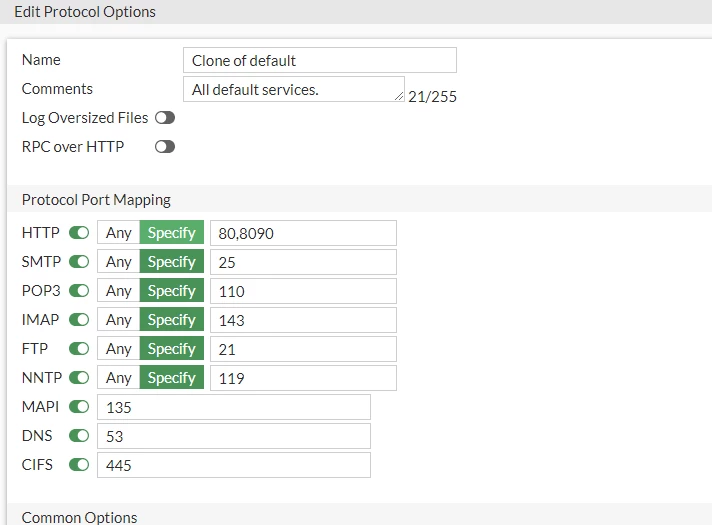
As per requirement, it is possible add additional port number for scanning after adding comma or if it is required to scan HTTP hosted for all the ports than choose any.
2) Under Security profiles -> SSL Inspection and Edit/create SSL Inspection Profile for deep-inspection. Add non-standard ports for HTTPS as mentioned above.
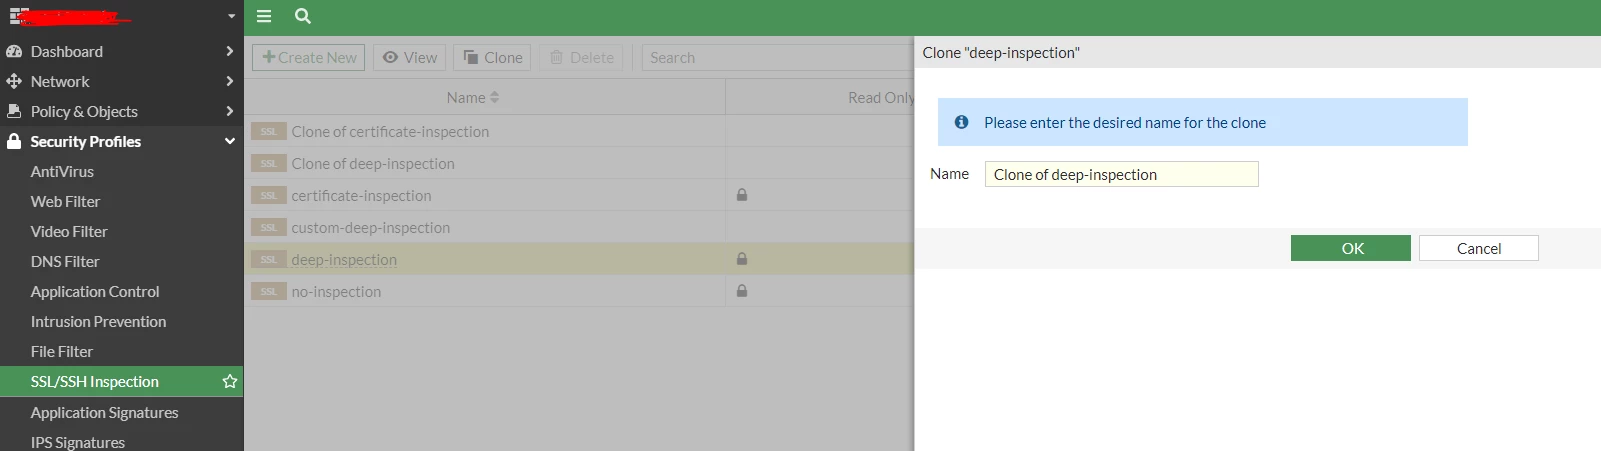
Now add custom port along with HTTPS. In case all the port need to scan than, it is possible to enable inspect all ports.
3) Apply above created/edited Protocol options as well as SSL Inspection Profile on the firewall policy. |

