
Technical Tip: Configuring firewall policy and firewall proxy policies source and/or destination address with firewall address wildcard FQDN type objects
Description
This article provides complementary information on firewall address wildcard FQDN type objects that have been introduced starting with FortiOS v6.2.2.
Scope
FortiGate.
Solution
Alike it was previously the case with FQDN objects, it is now possible, starting with FortiOS v6.2.2, to use pre-defined or user-defined wildcard FQDN objects for configuring the source address and/or destination address of a Firewall Policy or a firewall proxy policy.
For wildcard FQDN addresses to work, the DNS resolution from the PC to the DNS Server should pass through FortiGate.
Creating a Firewall Address of type FQDN from the GUI.
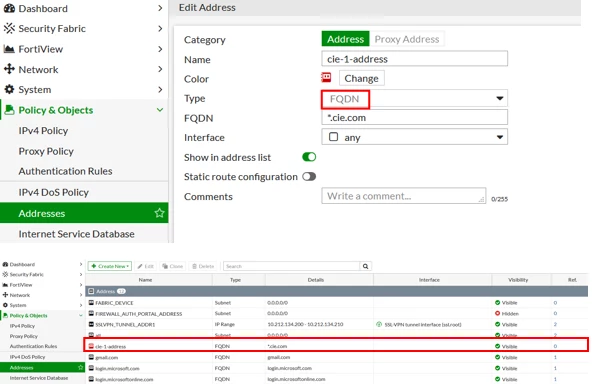
Displaying Firewall Address information from CLI.
config firewall address
…
edit "wildcard.dropbox.com" <----- Pre-defined wildcard FQDN type object.
set uuid 4c296cd0-0254-51eb-165d-464362d57a2e
set type fqdn <-----
set fqdn "*.dropbox.com"
next
…
edit "cie-1-address" <<< user-defined wildcard FQDN type object
set uuid 1da49eb2-0a37-51eb-9c6c-529c7483a5b3
set type fqdn <-----
set color 7
set fqdn "*.cie.com"
next
end
…
edit "wildcard.dropbox.com" <----- Pre-defined wildcard FQDN type object.
set uuid 4c296cd0-0254-51eb-165d-464362d57a2e
set type fqdn <-----
set fqdn "*.dropbox.com"
next
…
edit "cie-1-address" <<< user-defined wildcard FQDN type object
set uuid 1da49eb2-0a37-51eb-9c6c-529c7483a5b3
set type fqdn <-----
set color 7
set fqdn "*.cie.com"
next
end
Once defined, a wildcard FQDN type firewall address object can then be used as a source and/or destination address of a firewall policy or firewall proxy policy.
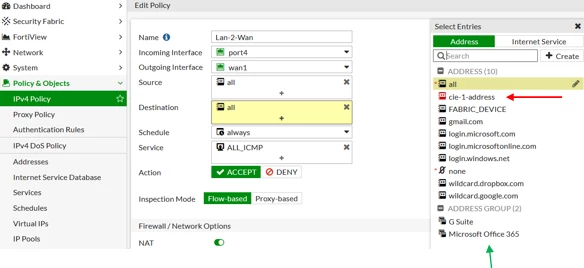
It has to be noted that firewall address wildcard FQDN type objects are different than the already existing wildcard FQDNs, which are defined in the 'config firewall wildcard-fqdn custom' section and are dedicated to SSL inspection exemptions. Therefore, pre-defined wildcard FQDNs (e.g., 'microsoft') or user-defined wildcard FQDNs (e.g., 'cie-1-wild-fqdn') do not appear in the list of addresses that can be selected when configuring the source address and/or destination address variables of a firewall policy or a firewall proxy policy.
config firewall wildcard-fqdn custom
…
edit "microsoft" <----- Pre-defined wildcard FQDN.
set uuid 4c549702-0254-51eb-b42a-a4e5e533c197
set wildcard-fqdn "*.microsoft.com"
next
…
edit "cie-1-wild-fqdn" <----- User-defined wildcard FQDN.
set uuid ba862812-0a38-51eb-0be5-7917d66e2c53
set wildcard-fqdn "*.cie.com"
set color 8
next
end
…
edit "microsoft" <----- Pre-defined wildcard FQDN.
set uuid 4c549702-0254-51eb-b42a-a4e5e533c197
set wildcard-fqdn "*.microsoft.com"
next
…
edit "cie-1-wild-fqdn" <----- User-defined wildcard FQDN.
set uuid ba862812-0a38-51eb-0be5-7917d66e2c53
set wildcard-fqdn "*.cie.com"
set color 8
next
end
Despite this difference, it is not possible to provide the same name to a firewall address wildcard FQDN type object and a wildcard FQDN defined in the 'config firewall wildcard-fqdn custom' section.
Note.
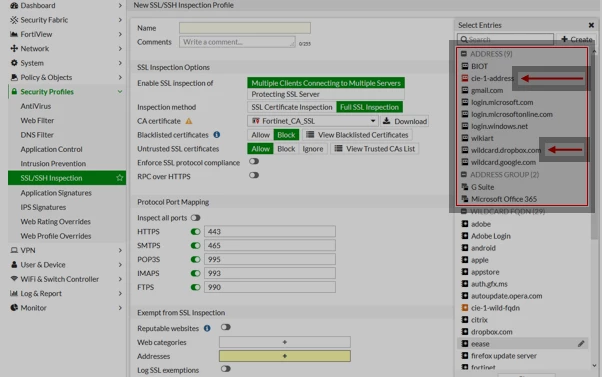
While, as mentioned above, wildcard FQDNs custom objects do not appear in the list of address that can be selected when configuring the source address and/or destination address variables of a firewall policy or a firewall proxy policy, firewall address wildcard FQDN type objects, on the contrary, can be selected and used as SSL Inspection exemption addresses of SSL/SSH profiles (e.g. 'cie-1-address' or 'wildcard.dropbox.com' in the screenshot below).
Wildcard FQDN objects and DNS resolution.
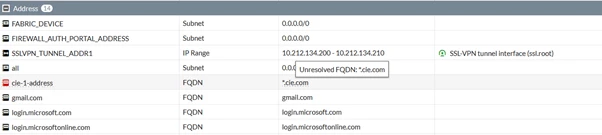
Right after being configured, wildcard FQDN objects displayed in the firewall address list show a status of 'Unresolved FQDN'.
That status is updated with the corresponding set of IP addresses at the time the FortiGate has to process traffic matching the wildcard FQDN, and DNS resolution has to be done.
By default, IP addresses are assigned to wildcard FDQNs for an unlimited time, but this can be changed using the 'cache TTL' variable if needed.
config firewall address
edit "cie-1-address" <----- user-defined wildcard FQDN type object.
set uuid 1da49eb2-0a37-51eb-9c6c-529c7483a5b3
set type fqdn <-----
set color 7
set fqdn "*.cie.com"
set cache-ttl <----- A value in the range 0-86400.
next
end
edit "cie-1-address" <----- user-defined wildcard FQDN type object.
set uuid 1da49eb2-0a37-51eb-9c6c-529c7483a5b3
set type fqdn <-----
set color 7
set fqdn "*.cie.com"
set cache-ttl <----- A value in the range 0-86400.
next
end
Note:
FQDN to IP address mapping can be displayed using the 'diagnose firewall fqdn list' CLI command.
FQDN to IP address mapping can be displayed using the 'diagnose firewall fqdn list' CLI command.
Starting in v7.0.4, the 'diagnose firewall fqdn list' CLI command has been replaced. The equivalent CLI command is 'diagnose firewall fqdn list-all'.
The following options have also been added:
diagnose firewall fqdn
list-ip List IP FQDN.
list-mac List MAC FQDN.
list-all List FQDN.
getinfo-ip Get info of IP FQDN address
getinfo-mac Get info of MAC FQDN address
get-ip Get and display one IP FQDN address.
get-mac Get and display one MAC FQDN address.
list-ip List IP FQDN.
list-mac List MAC FQDN.
list-all List FQDN.
getinfo-ip Get info of IP FQDN address
getinfo-mac Get info of MAC FQDN address
get-ip Get and display one IP FQDN address.
get-mac Get and display one MAC FQDN address.


