johnathan
Staff
Staff
December 31, 2025

Technical Tip: Configuring a shared FQDN and certificate for the Captive Portal without using a loopback interface

  • December 31, 2025
  • 0 replies
  • 438 views
Description This article describes the simplest way to use the same certificate for multiple Captive Portals.
Scope FortiOS.
Solution

To use the same certificate for Captive Portals on different interfaces, they all need to share the same FQDN but resolve to the corresponding IP the FortiGate has for that interface.

This can be achieved in multiple different ways, the simplest would be to use a DNS filter.

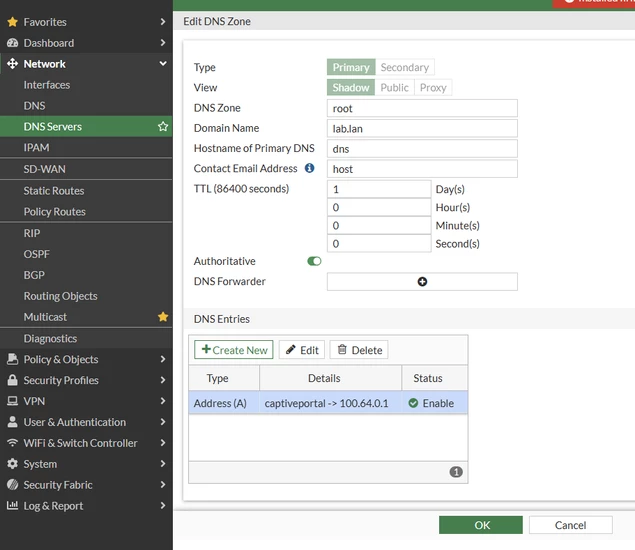
The following is the first Captive Portal configured in the device. The certificate has 'captiveportal.lab.lan' as the domain (this should be a real certificate signed by a public CA). Currently, this resolves to 100.64.0.1 as per the local DNS database:
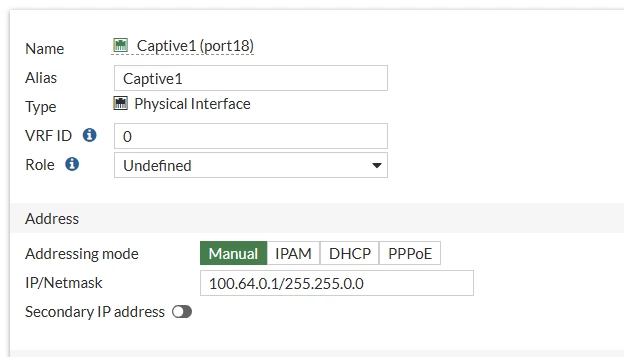
 

c1 1.PNG 

dnsdb.PNG


The following is the second Captive Portal configured in the device. Notice how the interface IP is 100.65.0.1, so the domain would not resolve correctly: 
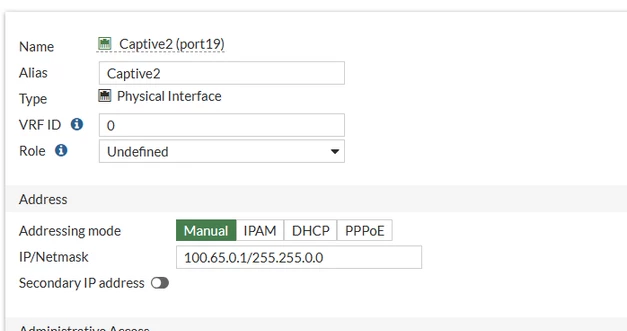
 

c2.PNG


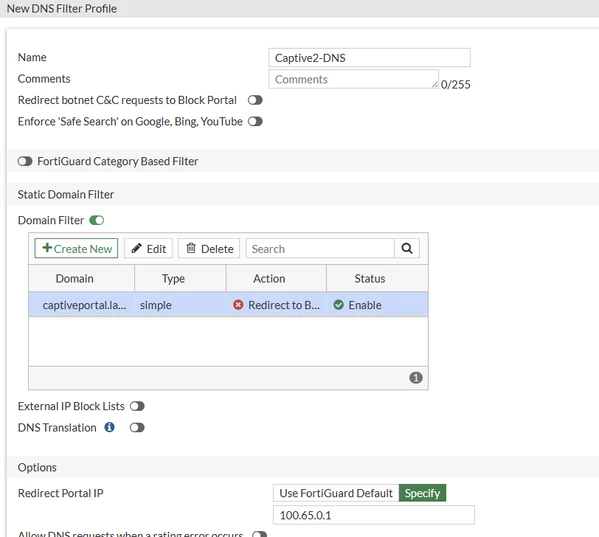
In order to make this work, create a new DNS filter to 'block' captiveportal.lab.lan. When the DNS filter blocks a domain, it allows returning an arbitrary IP as the response. Under 'Redirect Portal IP', set this to the IP of the interface to go to. In this case, it will be 100.65.0.1:


dnsfilter.PNG


For the first captive portal, the DNS setting should be set to use the FortiGate as the DNS server and the local DNS entry.
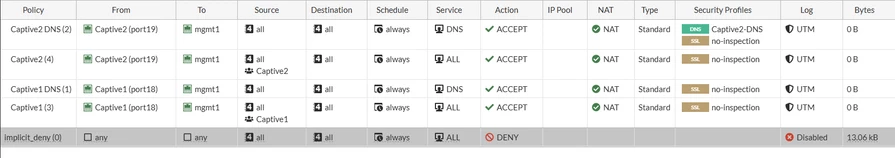
For every additional captive portal, the DNS should be set to Public DNS and the DNS filter applied on the policy.
When trying to use the 'DNS filter' option in the 'DNS Service on Interface' menu, the DNS filter is technically applied after the local entry is matched so it is not possible to use it in this way. It must be on a policy.

policy w.PNG


This configuration can be scaled to as many Captive Portals as needed. A different DNS filter would be used for each additional Captive Portal on its DNS policy.
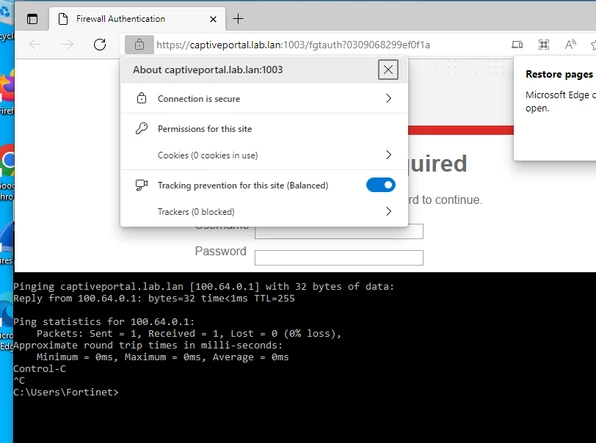
When accessing the Captive Portal on Captive1, no certificate warning is seen:


captive1good.PNG


When accessing the Captive Portal on Captive2, no certificate warning is seen:
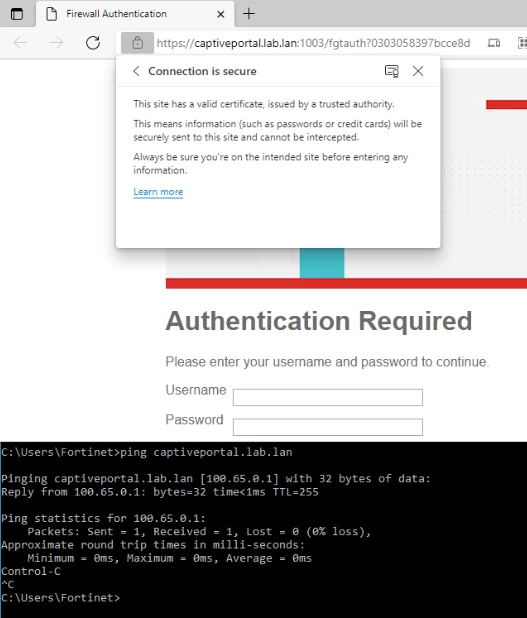
 

captive2good.PNG
    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!