



Technical Tip: Configure password policy for locally defined administrator passwords and IPsec VPN pre-shared keys
Description
The article describes how to configure the password policy for locally defined administrator passwords and IPsec VPN pre-shared keys.
Scope
FortiGate.
Solution
Configuration from GUI:
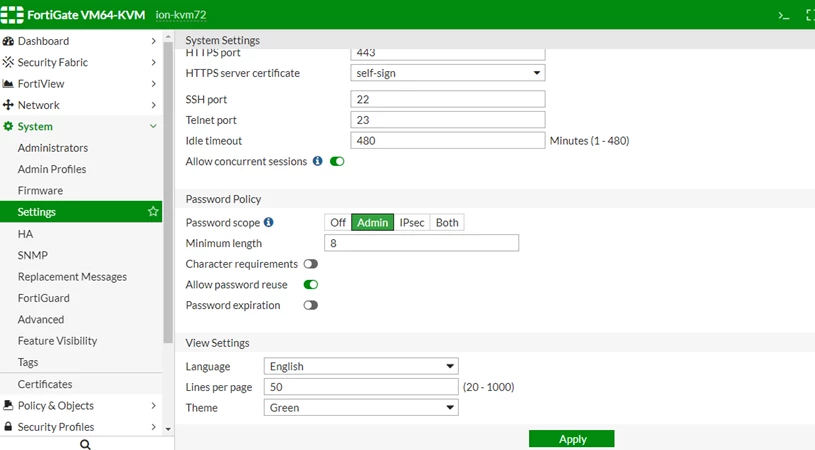
To create a system password policy from the GUI:
- Go to System -> Settings.
- In the Password Policy section, change the Password scope to Admin, IPsec, or Both.
- Configure the password policy options.
- Select 'Apply'.
To create a system password policy the CLI:
set status {enable | disable}
set apply-to {admin-password | ipsec-preshared-key}
set minimum-length <8-128>
set min-lower-case-letter <0-128>
set min-upper-case-letter <0-128>
set min-non-alphanumeric <0-128>
set min-number <0-128>
set change-4-characters {enable | disable}
set expire-status {enable | disable}
set expire-day <1-999>
set reuse-password {enable | disable}
end
config system password-policy
set login-lockout-upon-downgrade { enable | disable }
end
When enabling login-lockout-upon-downgrade, a warning message will appear. To apply the configuration, an administrator must confirm the setting manually.
Verification of Configuration and troubleshooting:
If Password Scope is Admin:
FGT1 # show system password-policy
# config system password-policy
set status enable
end
If Password Scope is IPsec:
FGT1 # show system password-policy
# config system password-policy
set status enable
set apply-to ipsec-preshared-key
end
If Password Scope is Both Admin and IPsec:
FGT1 # show system password-policy
# config system password-policy
set status enable
set apply-to admin-password ipsec-preshared-key
end
Related article:

