



Technical Tip: Configure FSSO in DC Agent mode
Description
This article describes how to configure Fortinet Single Sign On Collector Agent (FSSO-CA) in DC Agent mode.
Scope
FortiGate, FSSO, FSSO CA, DC Agent.
Solution
After downloading, validating, and installing FSSO-CA is possible to configure it in DC Agent mode.
- Port Requirements:
Inbound.
TCP/8003 – DC_Agent keepalive and push logon info to Collector Agent (SSL enabled/secure).
UDP/8002 – DC_Agent keepalive and push logon info to Collector Agent.
TCP/8001 – FortiGate to FSSO Collector Agent connection (SSL).
TCP/8000 – FortiGate to FSSO Collector Agent connection.
TCP/8000 – NTLM.
Outbound.
TCP/135, TCP/139, UDP/137 – Workstation check, polling mode (fallback method).
TCP/445 – Workstation check (remote registry).
TCP/389 – Group lookup using LDAP.
TCP/636 – Group lookup using LDAPS.
UDP/53 – DNS for resolving hostnames of the logon events.
Collector agent with SSL connection to FortiGate. See this KB article Technical Tip: Fortinet Single Sign On (FSSO) Agent SSL connection to FortiGate.
FSSO-CA server configuration:
- Open FSSO-CA:

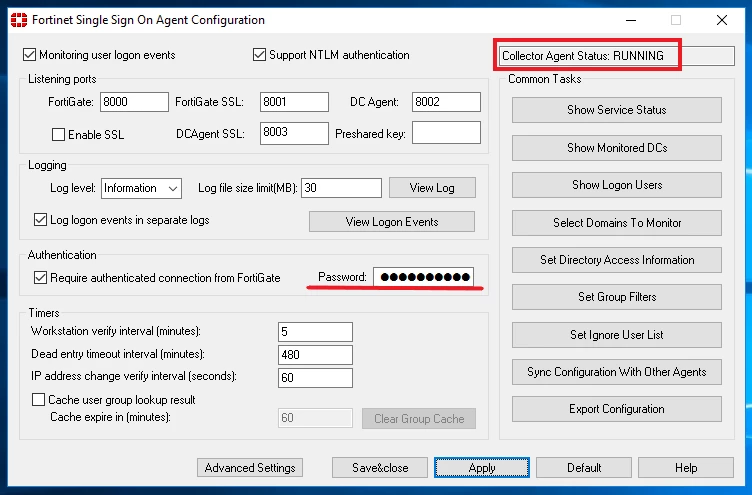
- Validate Collector Agent status is in RUNNING and set up one password (take note, it will be used for FortiGate connection) and select Apply to save the password. Ensure the password does not exceed 15 characters. The character limit for passwords on the FSSO collector agent is 15 characters.
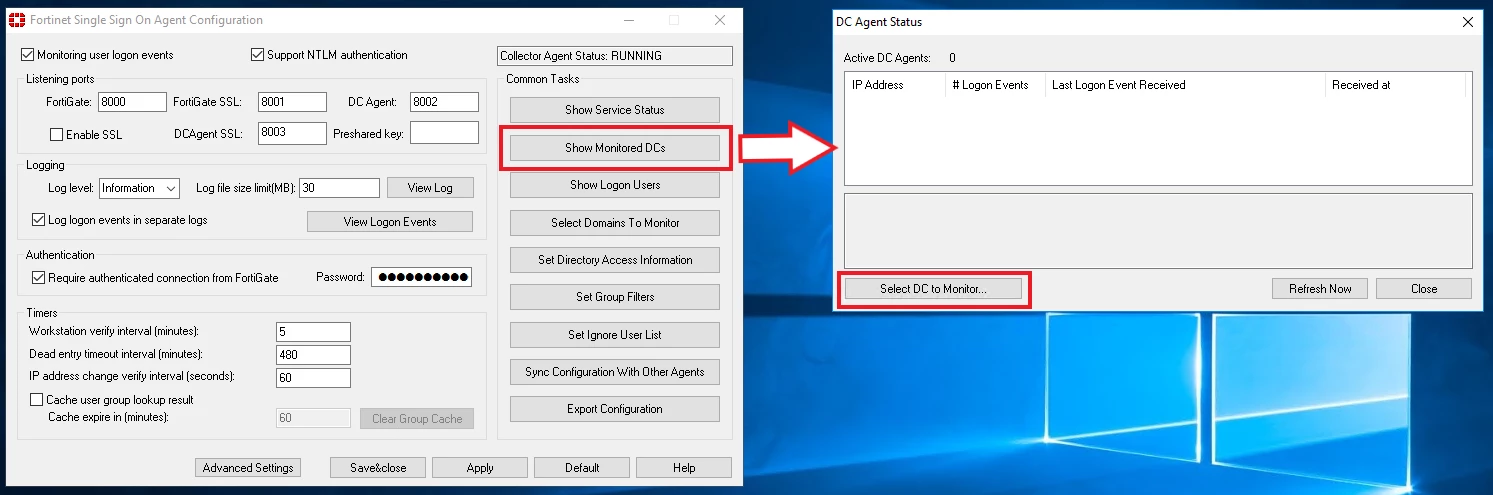
- Select 'show monitored DCs', then 'Select DC to Monitor'.
- Then select 'DC Agent mode' and select all DC servers listed down:

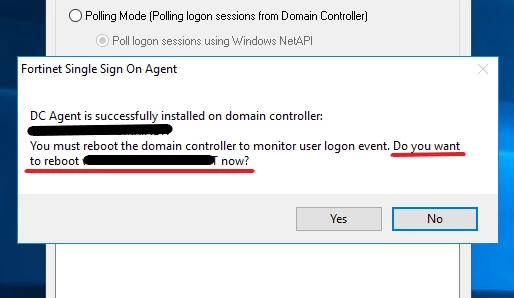
- Then select OK, and the DC Agent installation advice will be displayed for each DC server. Install a DC agent on every domain controller where user logon events captured on AD servers are necessary. DC Agent mode provides reliable user login information; however, installing a DC agent on every domain controller is necessary. A reboot is needed after the agent is installed. Each installation requires some maintenance as well. For these reasons, it may not be possible to use the DC Agent mode.

- To finish the DC Agent installation, a reboot for each server is required; it is possible to wait between each reboot.
- Optional. Install GUI for DC Agent: Technical Tip: DC Agent Graphical Interface (dc_agent GUI)
Note:
The collector agent installation needs to run with an account that is a member of the local administrators or domain administrators. The permissions are required for creating local registries, libraries, local folders, logs, etc.
It is a temporary requirement, however, it is needed for the installation to be completed properly.
To restrict a Fortinet Single Sign On Agent Service account, follow the link at the bottom.
Important points to keep in mind:
- Enable DC Agent log: Technical Tip: How to enable logging on DC Agent (FSSO DC Agent mode)
- Configure user group filter: Technical Tip: FSSO Group Filter configured on Collector Agent
- Configure poller event ID with value '2': Technical Tip: Windows event IDs used by FSSO in WinSec polling mode
FortiGate Configuration.
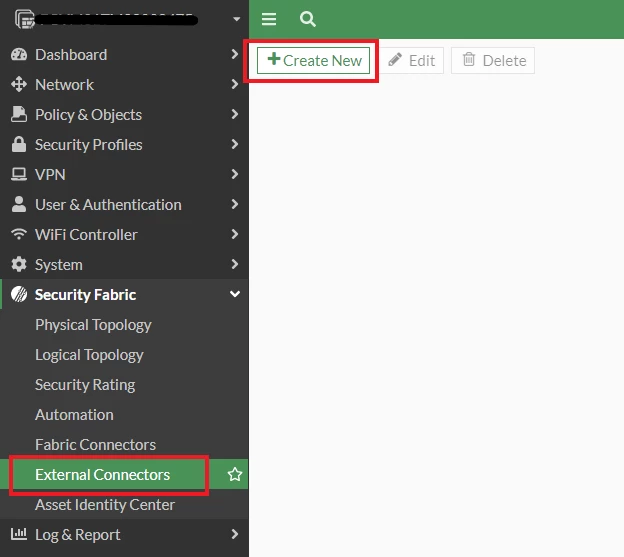
- Configure Security Fabric -> External Connector -> Create New.
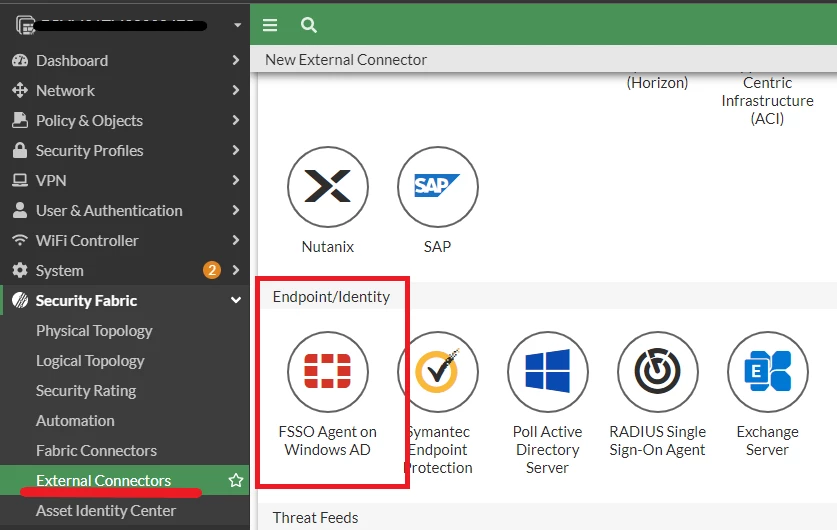
- In Endpoint Identity -> FSSO Agent on Windows AD.
- Configure Name, IP/FQDN, and same password as point 2.
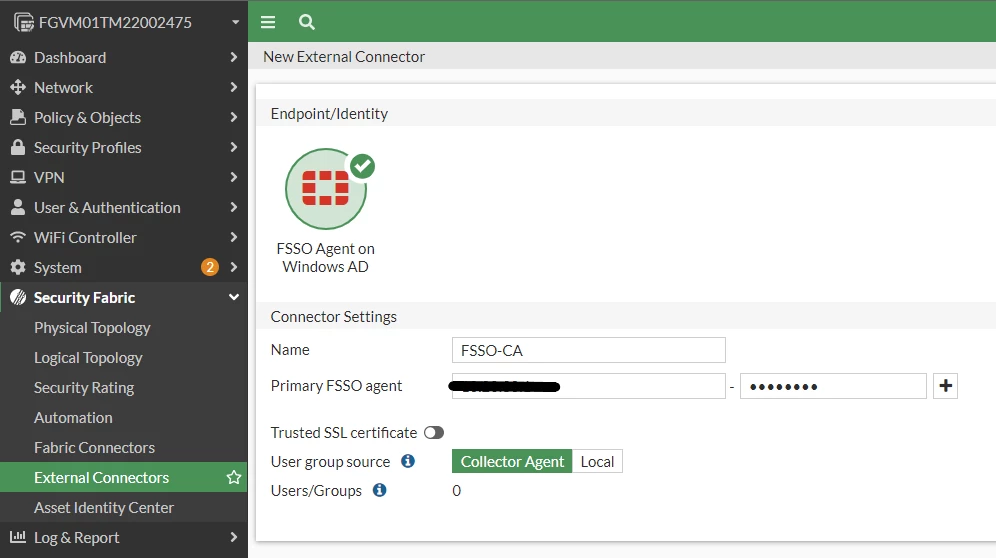
If there are two or more FSSO-CA servers installed, it is possible to add a new entry with '+', only one FSSO Connector is allowed with many FSSO-CA servers, and two or more FSSO Connector for the same domain will cause user group inconsistency.
For user group sources, use 'Collector Agent' for Standard or 'Local' for Advanced: Technical Tip: FSSO Windows Directory Access Methods - Standard versus Advanced Mode
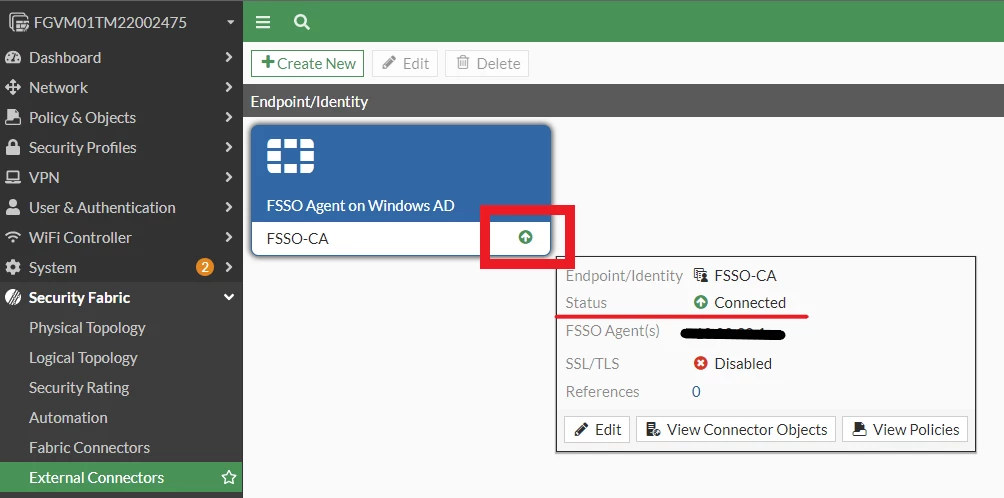
- FSSO connector must show connected in green color and if hovering over the connector for a few seconds a status will be displayed.
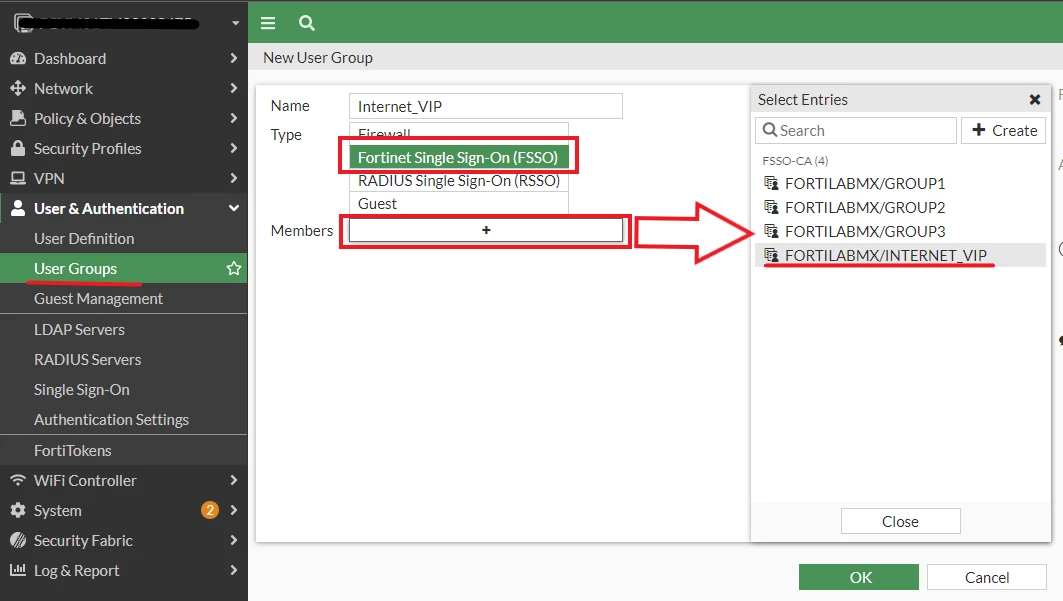
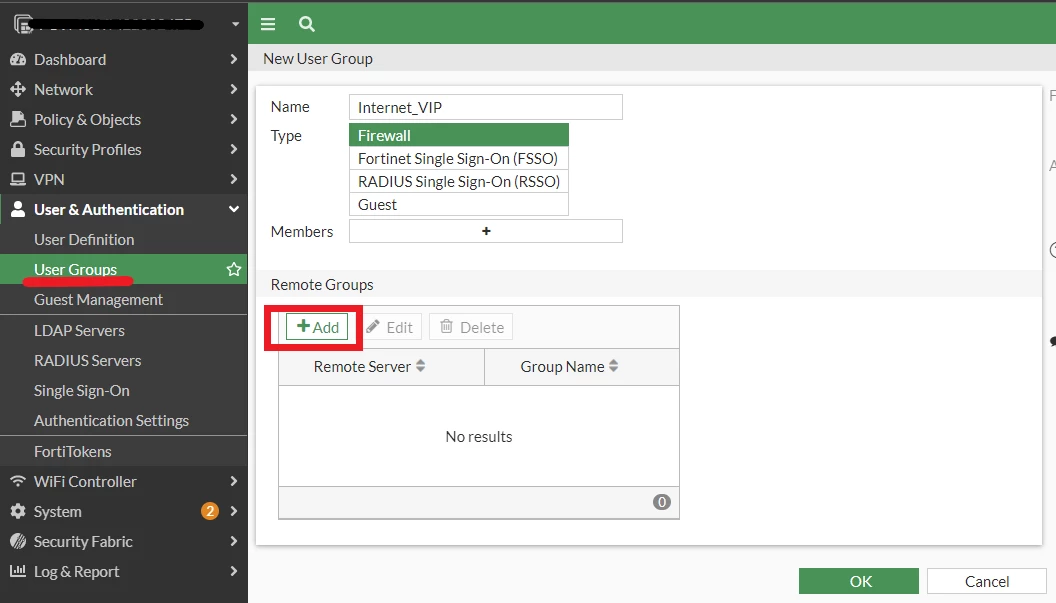
- Based on the previous configuration of point 3. FSSO Connector -> User group source, Create a user group to use it in Firewall Policy. For Collector Agent (imported from FSSO-CA):
For Local (imported from LDAP):
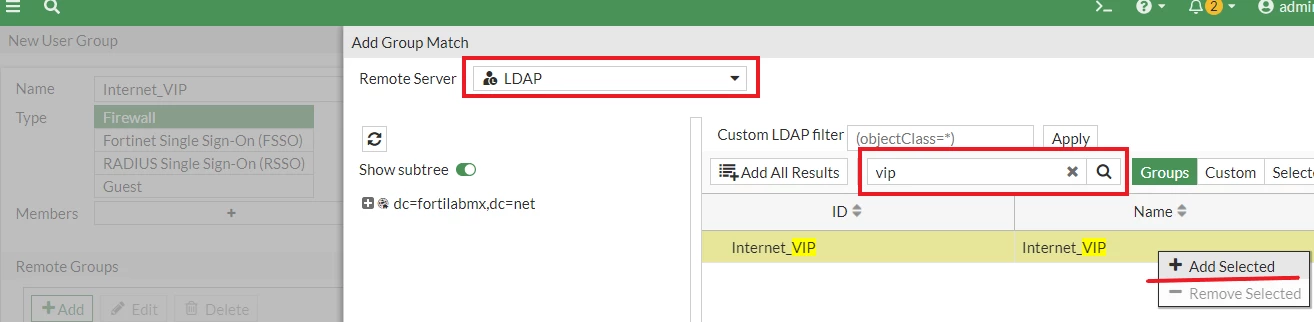
Important Note:
Avoid using crossed configurations.
- Configure firewall policies with a user group in the source.

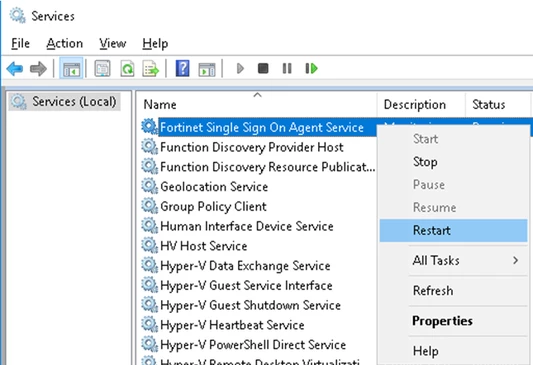
Note: After updating the IP address on the DC Agent, the status may keep displaying the old IP address. A service restart or system reboot may be required to rectify this.
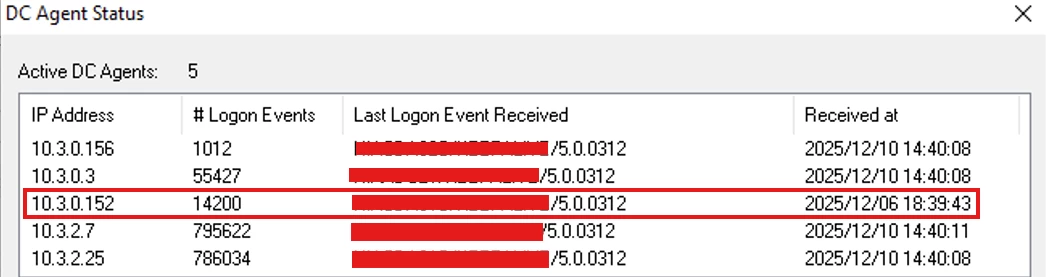
To restart the service, select the Search icon and search for Services. Select Services -> Fortinet Single Sign On Agent Service: right-click and select Stop, then right-click and select 'Start'.
Related articles:
Technical Tip: DC Agent Graphical Interface (dc_agent GUI)
Technical Tip: FSSO choose between DC Agent mode or Polling mode
Technical Tip: Downloading FSSO agent software
Technical Tip: How to validate MD5 checksum hash for FSSO installer
Technical Tip: How to install FSSO Collector Agent
Technical Tip: Comparison between DC-Agent mode and polling mode
Troubleshooting Tip: FSSO Complete troubleshooting for TAC tickets
Technical Tip: Restricting a Fortinet Single Sign On Agent Service (FSSO) service account
Technical Tip: FSSO breaks after installing Microsoft KB5039227 or KB5039217 update
Technical Tip: Common reasons FSSO status shows as 'down' on the Firewall

