mpandya
Staff
Staff
October 30, 2025

Technical Tip: Collect IKE Debug Logs for IPsec VPN Directly from the GUI

  • October 30, 2025
  • 0 replies
  • 2299 views
Description This article describes the process of collecting IKE debug logs using the FortiGate GUI.
Skope FortiGate v7.6.3 and later.
Solution

In environments where multiple IPsec tunnels are configured, managing diagnostics through the CLI can be complex. The FortiGate GUI provides a simplified and more efficient method for collecting IKE debug logs.


Steps to collect IKE debug from the GUI:

  1. Log in to the FortiGate GUI.
  2. Navigate to VPN -> IPsec Tunnels.
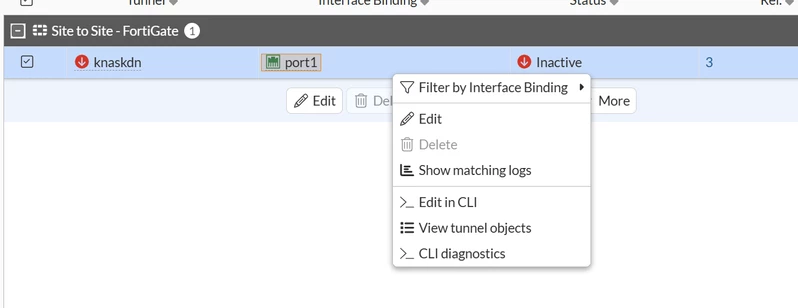
  3. Locate the specific IPsec tunnel that requires debugging.
  4. 'Right-click' the tunnel and select CLI Diagnostics.

 Screenshot 2025-09-27 025811.png


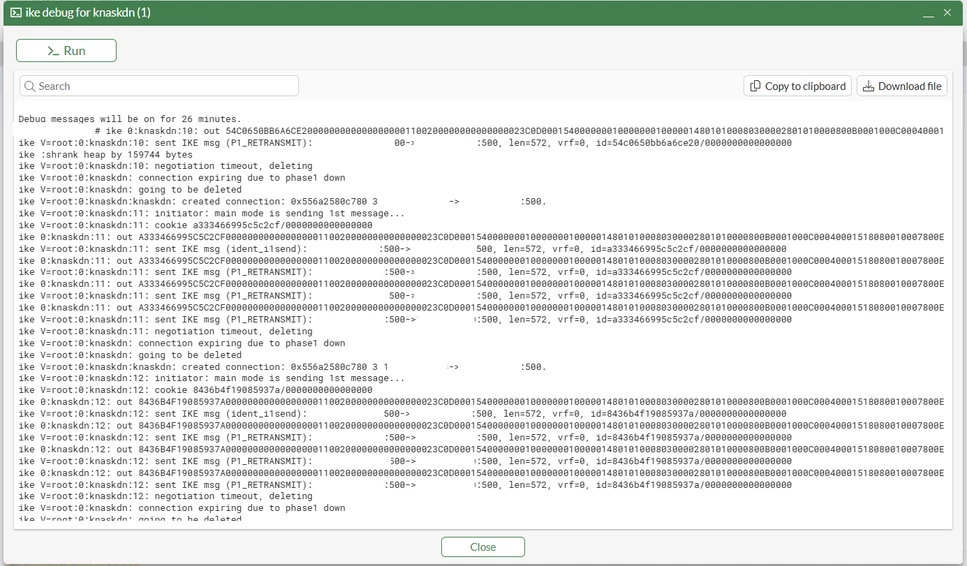
  1. In the opened diagnostics window, IKE Debug will run for the selected ipsec tunnel.


Screenshot 2025-12-02 151004.png


  1. Start the debug process and reproduce the issue or initiate the tunnel connection.
  2. Once the debug session is complete, stop the debug 'diagnose debug reset' to avoid unnecessary log generation.
  3. The collected debug output can be reviewed directly in the GUI or exported for further analysis.


    Thought Leadership. Security Summit. Thursday, November 12th, PGA National Resort, Palm Beach Gardens, FL.
    Thought Leadership. Security Summit. Thursday, October 8th. Disney's Grand Californian Hotel & SPA, Anaheim, CA.