


Technical Tip: Changing Interface associated to the Generic Routing Encapsulation (GRE) tunnel
| Description | This article describes the changing interface associated to the Generic Routing Encapsulation (GRE) tunnel. |
| Scope | FortiGate all models. |
| Solution | GRE tunnel is always associated to an interface and these are the steps to migrating the GRE tunnel from WAN1 to WAN2 Interface.
Initial Configuration.
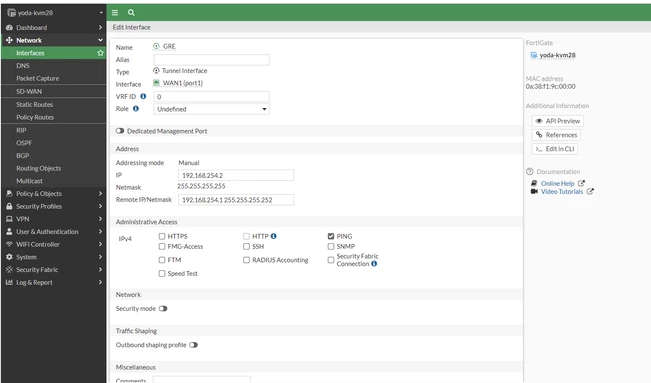
config system interface edit "GRE" show config system interface edit "GRE" set vdom "root" set ip 192.168.254.2 255.255.255.255 set allowaccess ping set type tunnel set remote-ip 192.168.254.1 255.255.255.252 set snmp-index 15 set interface "port1" next end
Change the interface to port3.
set interface "port3"
This error will occur when changing the interface.
Entry not found in datasource. Value parse error before 'port3'. Command fail. Return code -3.
config system gre-tunnel edit GRE show
config system gre-tunnel edit "GRE" set interface "port1" set remote-gw 10.56.241.131 set local-gw 10.56.241.156 next end
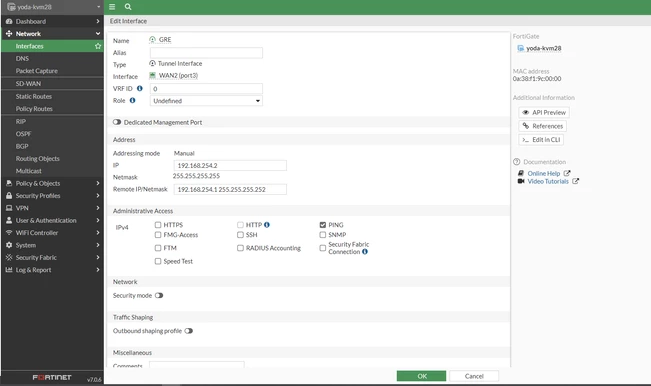
Change the interface and save it using end command.
(GRE) # set interface port3 (GRE) # end
 Related articles: Technical Tip: Configuring and verifying a GRE tunnel between two FortiGates (static routing) Configuring IPsec or GRE tunnels on FortiOS |


