



Technical Tip: Captive portal and LDAP authentication
Description
This article explains how to configure a captive portal for LDAP users.
Scope
FortiGate.
Solution
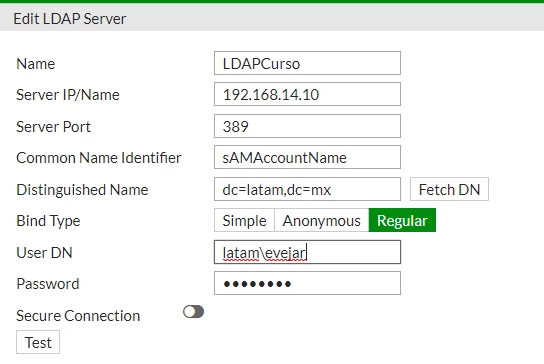
- Configure the LDAP Server: Go to User & Authentication -> LDAP Server. Select 'create new' and configure as follows:
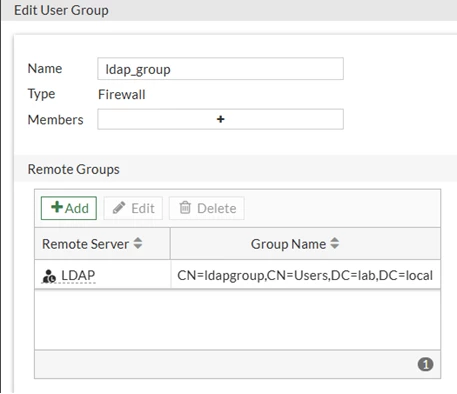
- Go to User & Authentication -> User Groups and configure the LDAP user group. Select 'create new' and configure as follows:
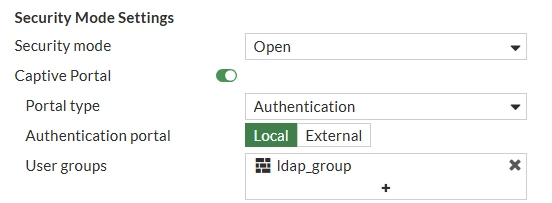
- Enable the captive portal in the interface or SSID: Enable Security Mode and captive portal. In the user groups section, select the User group created in step 2.
- Create a firewall policy to allow traffic for the user group:
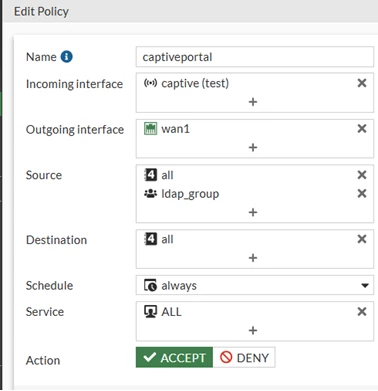
Note: Only certain traffic can trigger a captive portal redirection. If specific services are selected instead of ALL, it is required to allow at least one of the following services to trigger the captive portal:
- HTTP.
- HTTPS.
- FTP.
- Telnet.
Unauthenticated DNS requests are allowed:
If a firewall policy has a user or group configured in the source field, and the firewall policy allows the 'ALL' or 'DNS' service, TCP and UDP port 53 DNS traffic is allowed regardless of authentication status. This is because some DNS access is likely required to initially trigger the captive portal.
Related articles:
Troubleshooting Tip: General captive portal explanation, flow and troubleshooting
Technical Tip: Creating Captive Portal with LDAP users via policy-based

