Technical Tip: Blocking YouTube shorts on FortiGate
| Description | This article describes how to block YouTube Shorts while allowing access to normal YouTube videos on FortiGate. It provides a step-by-step guide to configuring the necessary settings to achieve this. |
| Scope | FortiGate. |
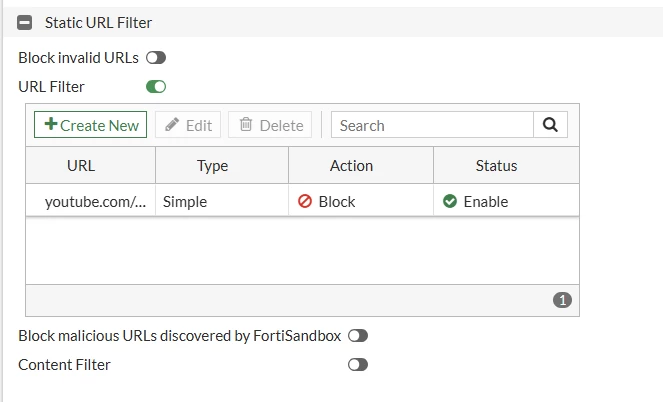
| Solution | To block YouTube Shorts on FortiGate, follow these steps: Go to Security Profile -> Webfilter -> Static URL filter -> URL Filter and create a new URL filter. In the URL filter, add the following URL: youtube.com/shorts/ and set the action to block.
Go to Policy & Objects -> Policy -> IPv4 and create a new policy or edit an existing one. In the policy, add the Web Filter profile created in step 1 and set the action to block. CLI method:
config webfilter profile edit "block-shorts" <----- Create or edit a web filter profile (choose a name or use an existing one). config ftgd-wf unset options config web set urlfilter-table 1 <----- Using table ID 1 for the URL filter. end config urlfilter edit 1 config entries edit 1 set url "youtube.com/shorts" set type wildcard set action block set status enable next end next end
Apply it to a policy:
config firewall policy edit <policy id> set webfilter-profile "block-shorts" <----- Add the webfilter profile created previously. next end
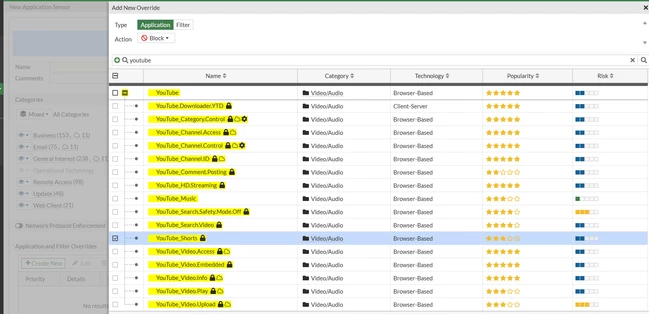
Alternatively, it is possible to use Application Control to block YouTube Shorts. Go to Security Profile -> Application Control -> Application and Filter overrides and create a new application control policy. In the application control policy, add the YouTube Shorts application and set the action to block.
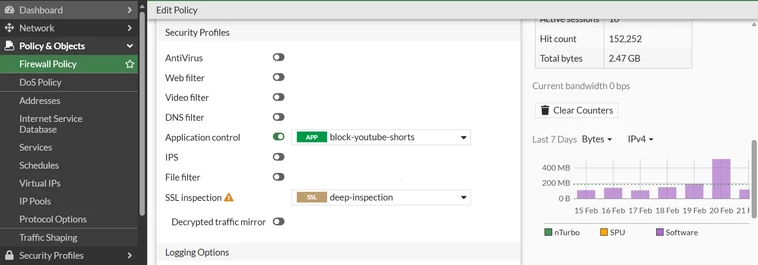
Go to Policy & Objects -> Policy -> IPv4 and create a new policy or edit an existing one. In the policy, add the application control policy created in step 5 and set the action to block.
CLI method:
config application list
edit <policy id>
The Application Control Profile is then used in the Firewall Policy with Deep Packet Inspection.
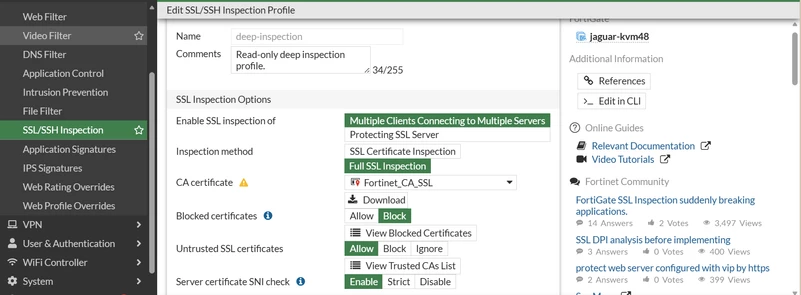
For Deep Inspection, make sure the user's browser has a cert installed for the SSL handshake. Refer to the document Importing the certificate into web browsers.
Windows Group Policy Editor can be used to push the certificate to users' browsers in the appropriate environment, such as the Windows Group Policy Management Console. In this instance, importing the certificate into users' browsers is not necessary.
Note: Without Deep Packet Inspection, this Application Control will not work in this case.
The results of downloading the Certificate from the SSL Inspection Profile are shown in the screenshot below:
Make sure to apply the changes and test the configuration to ensure that YouTube Shorts are blocked while normal YouTube videos are allowed. |