Technical Tip: Blocking a MAC address in FortiGate using a Firewall Policy
| Description | This article describes how to block a MAC address in FortiGate using a Firewall Policy. |
| Scope | FortiGate 6.x.x and 7.x.x. |
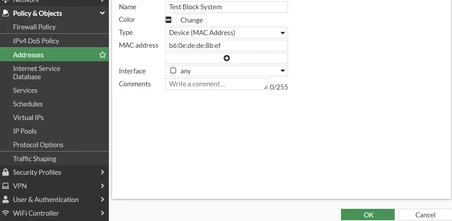
| Solution | The Firewall Policy to block a MAC address can be either configured from a specific source and destination interface, or for all interfaces.
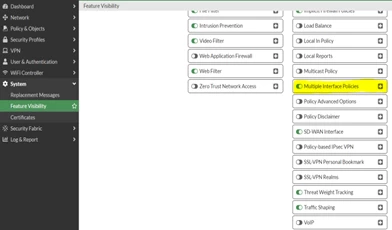
If that MAC should be blocked from accessing all interfaces: Enable the Multiple Interface Policies feature in feature visibility (configuring a policy in this way will stop Interface Pair view from working):
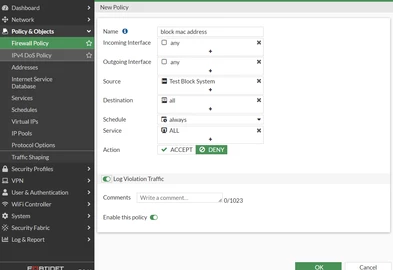
Make a Deny Firewall Policy with the source address as the address object which we created in step 1, and move the policy to the top of the list:
If that MAC should be blocked from accessing specific interfaces (or if Interface Pair View mode should be preserved):
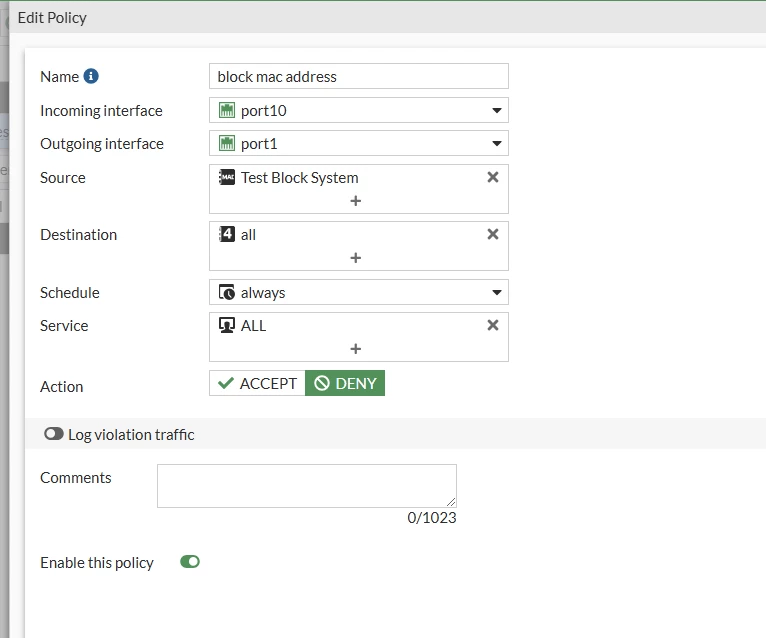
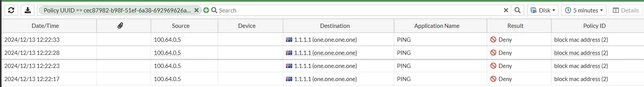
Traffic is now blocked:
Note: This works only if the MAC address is not getting changed in the path toward FortiGate or if the device is trying to access a service hosted by FortiGate (Web GUI, SSLVPN, etc.)
Related articles: |