



Technical Tip: Behavior of ZTNA Tags shared across multiple vdoms and multiple FortiGates
Description
This article describes the current behavior of ZTNA tags when shared across multiple VDOMs or multiple FortiGate firewalls in the Security Fabric connected to the same FortiClient EMS Server.
Scope
FortiGate v7.0.0+, v7.2.0+, v7.4.0+ running multi-VDOM mode.
FortiClient EMS Server v7.0.8+, v7.2.0+.
FortiClient v7.0.8+, v7.2.0+.
Solution
ZTNA tags can be used in several features in FortiGate and FortiClient, but the focus of this article will be ZTNA Access Proxy and ZTNA IP/MAC Control (NAC - Network Access Control), specifically when FortiOS is running in multi-VDOM mode.
ZTNA Access Proxy scenario
When FortiGate is running in multi-VDOM mode, it is possible to create a ZTNA Server in each VDOM and apply tags synchronized from the EMS Server to the ZTNA Rules. However, if the same FortiClient endpoint needs to connect to servers protected by ZTNA Servers in different VDOMs, then only the first one will work when ZTNA tags are applied.
To clarify, the example below has one endpoint attempting RDP connections to Server1 and Server2 via ZTNA Access Proxy.
The request to the first server (Server1) will succeed, and ZTNA Tag information will be cached with vdom1 information.
RDP connection will fail to Server2 because the TAG will fail to be matched, even though it is the same tag applied to vdom2.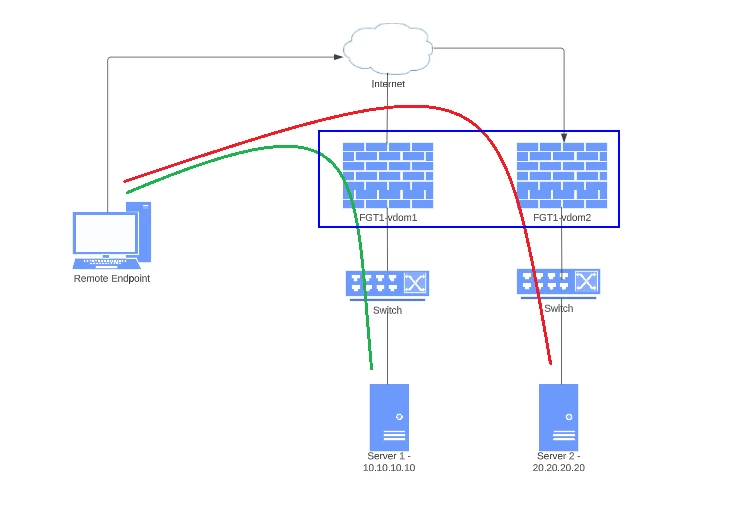
Irrespective of which server is accessed, only the first one will succeed until the FortiGate is rebooted or the ZTNA cache information is cleared by restarting the proxy process with the command diagnose test application wad 99 performed in Global VDOM.
NAC (IP/MAC) scenario.
Starting with FortiClient EMS Server v7.0.8 and v7.2.0, ZTNA Tag can be shared across multiple devices in the Fabric. This option is controlled in EMS as per the document below.
EMS administration guide: fabric devices
As previously mentioned, the ZTNA Tag will be synchronized from EMS to all FortiGate units authorized in the same EMS Server. However, the tag information relevant to NAC Control, which is the IP and MAC Addresses of a connected endpoint, will only be shared within the VDOM it is connected to.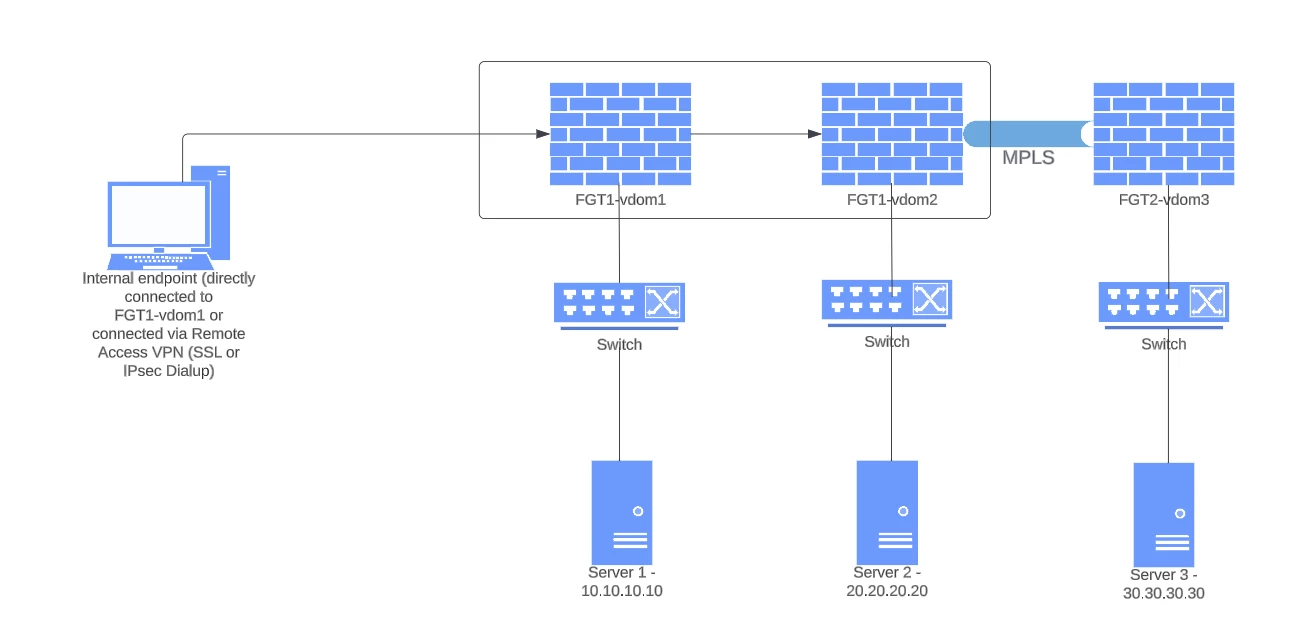
In the example above, if a ZTNA Tag is applied to firewall policies for traffic from Endpoint to Server1, Server2, and Server3, a connection will only succeed to Server1. The reason is the same as before: ZTNA tag information is only shared with the VDOM the endpoint is connected to, in this case, vdom1.
IP and MAC Addresses of the endpoint will not be shared to the same ZTNA tag in the same FortiGate FGT1-vdom2 nor to FortiGate FGT2-vdom3.
However, if FortiGate FGT2 has a VDOM called vdom1, then the tag information will be synced there as well.
Create ZTNA Access Proxy Servers in a single VDOM if the same endpoints require access to them.
ZTNA Tag information will be shared only with the VDOM to which the endpoint is connected. If it is necessary to share across multiple FortiGate units, the VDOM name must match in all firewalls.
Note.
This has been reported to Development under internal ticket 849073, which is currently under investigation.
This issue has been fixed in FortiOS v7.4.x and EMS v7.2.2 to configure multitenancy EMS or different EMSs with multiple VDOMs in FortiGate.
It is necessary to enable override.
CLI commands:
config endpoint-control settings
set override enable
end
For config, refer to the admin guide:
Configuring FortiGate per-VDOM connection
Note:
The override setting option is only available and supported in the FortiOS 7.4.x version.
Note on NAT: If the IP tags are available in both VDOMs but the traffic is still not matching, it could be due to the misuse of NAT in the policy for internal networks. When traffic is NATed in VDOM1 to traverse to VDOM2, the endpoint cannot be identified because the original traffic information is replaced by the NATed details.
Related document:
Configuring FortiClient EMS and FortiClient EMS Cloud on a per-VDOM basis

