Technical Tip: Basic L2 connectivity troubleshooting before opening a TAC ticket
| Description | This article describes a simple scenario where a workstation establishes access to the destination host and how to use the commands within FortiGate to execute the basic troubleshooting steps to solve the issues. |
| Scope | FortiGate. |
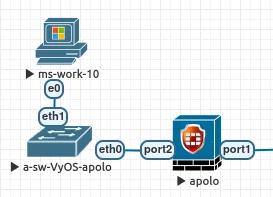
| Solution | Topology:
L2 connectivity between Workstation and FortiGate: Commonly, workstations use the DHCP as a service to receive an IP address to initiate the IP communication to internal and external hosts.
The FortiGate can be used as a DHCP server, but is it necessary to check the L2 connectivity between the Workstation and FortiGate.
Follow the basic information, and ensure that L2 communication between FortiGate and Workstation is working.
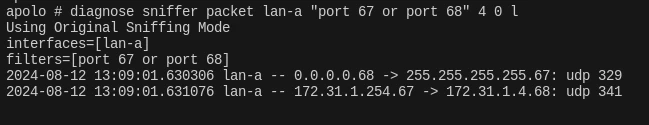
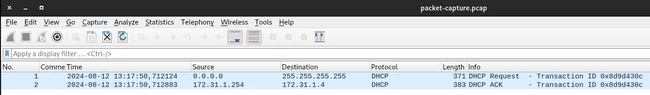
It is also possible to check if the DHCP request is arriving at the FortiGate interface. Check this by executing the command below, restarting the workstation NIC, or rebooting the Workstation. After this, the Workstation will send a DHCP Request using the broadcast destination, and the FortiGate will reply to this packet with a DHCP Offer.
diagnose sniffer packet <interface_name/any> "port 67 or port 68" 4 0 l
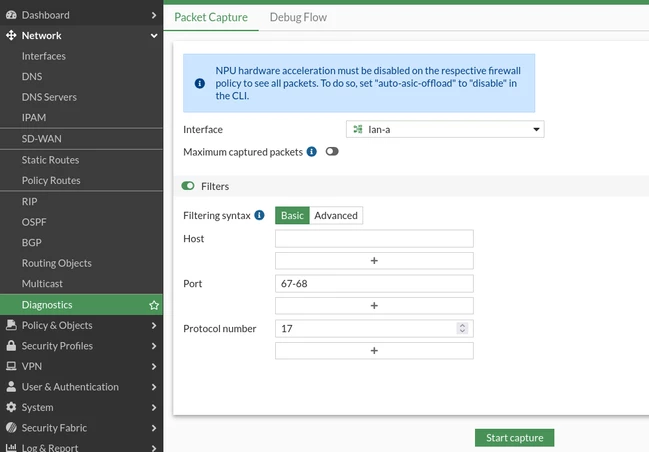
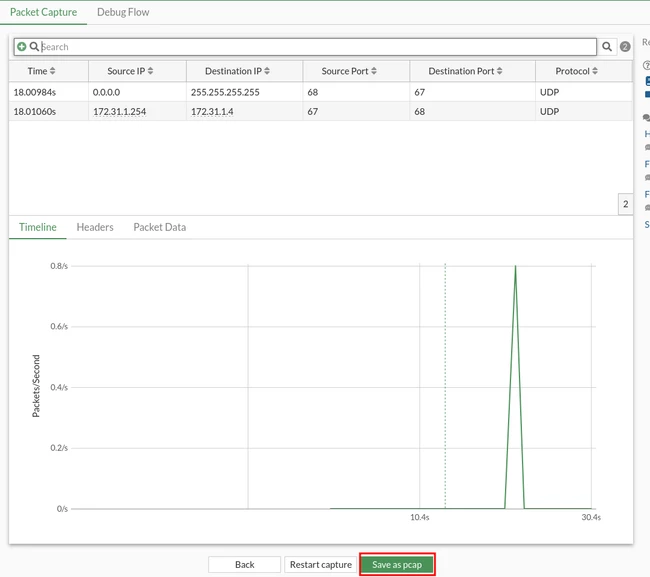
It is also possible to collect this information by opening the captured packets using Wireshark and viewing the detailed information regarding these packets, using the Packet Capture feature. Go under Network -> Diagnostics, select the desired interface and the filter used in the command 'diagnose sniffer packet'.
Select 'Start capture' and restart the Workstation NIC or reboot the Workstation.
Select 'Save as pcap'. FortiGate will save this information and generate a .pcap file. After this, it will be possible to see more detailed information about the communication via Wireshark.
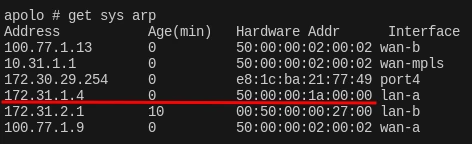
If this communication is happening, it is most likely that the L2 connection is OK, and it is possible to check this within the ARP table from FortiGate, using the command 'get sys arp'.
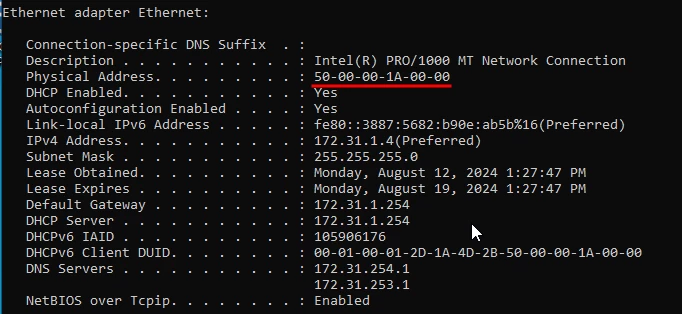
Confirm if the MAC address is correct by using the command 'ipconfig /all' on Windows devices and 'ifconfig' if using a Linux workstation.
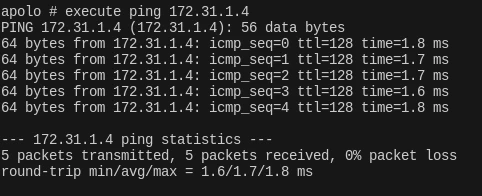
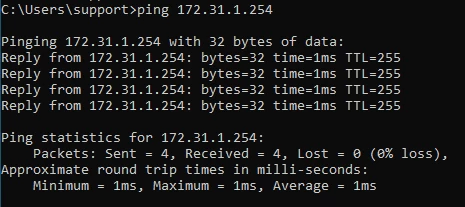
Execute a ping to check the integrity of this connection, from FortiGate or a workstation.
execute ping < Destination IP >
After following the above steps, the Workstation should be able to send packets to the FortiGate. The FortiGate will decide to forward these packets to the destination if they contain the correct IPv4 policy and routes to the destination.
Related articles: Troubleshooting Tip: Basic FortiGate connectivity diagnostics Technical Tip: 'Layer-1 and Layer-2 Troubleshooting' with 2 simple commands |