



Technical Tip : Alternative LDAP settings for FSSO Collector Agent
Description
In certain scenarios it is necessary to have a different account used for LDAP access information.
This is the default LDAP server that Fortinet Single Sign On Collector Agent uses to query user information; among other things, for finding and matching the groups a user is a member of, when the logon information for that user is received.
If this is left blank, which is the default setting, the FSSO CA will use the credentials from the FSSO CA service account (specified in the Windows Services).
This article describes how to set a different LDAP account for directory access information when using Advanced AD access mode.
Solution
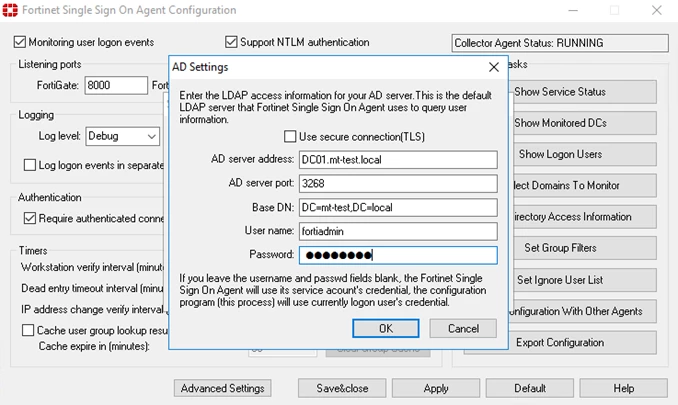
The AD settings can be set in the FSSO Collector Agent under Directory Access Information -> Advanced Setting.
In certain scenarios it is necessary to have a different account used for LDAP access information.
This is the default LDAP server that Fortinet Single Sign On Collector Agent uses to query user information; among other things, for finding and matching the groups a user is a member of, when the logon information for that user is received.
If this is left blank, which is the default setting, the FSSO CA will use the credentials from the FSSO CA service account (specified in the Windows Services).
This article describes how to set a different LDAP account for directory access information when using Advanced AD access mode.
Solution
The AD settings can be set in the FSSO Collector Agent under Directory Access Information -> Advanced Setting.
One important thing to note is that the username has to be entered without any domain prefix or suffix.
The domain information will be extracted from the information entered as the base DN and concatenated with the username.

