



Technical Tip: Allowing FSSO Ports when using Windows Server 2008 and higher
Description
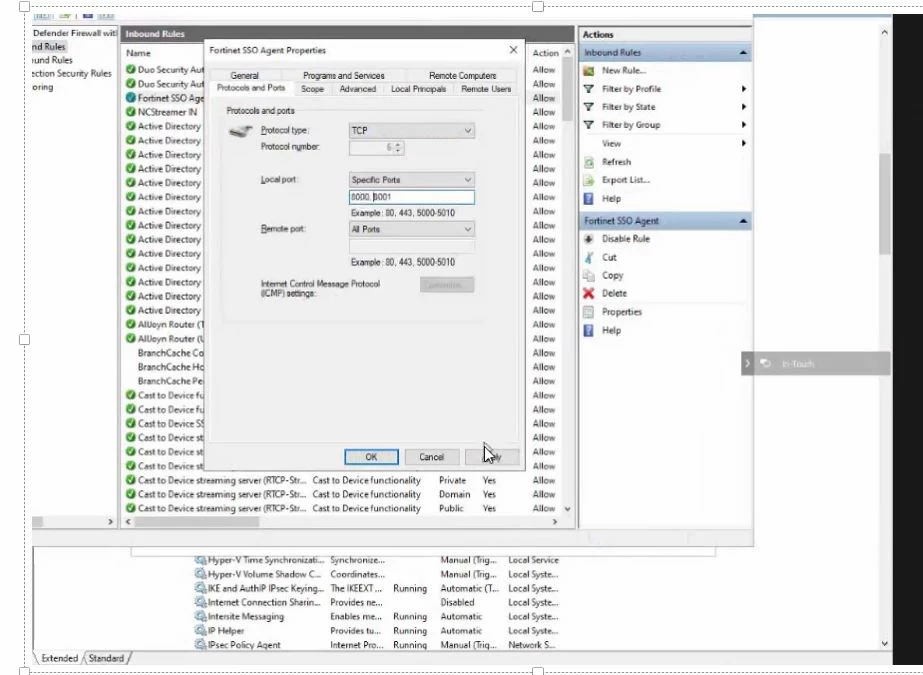
This article describes how to allow FSSO ports when using Windows Server 2008 and later versions. A new feature was implemented in Windows Server 2008 called 'Windows Firewall with Advanced Security'. This feature can sometimes block the FSSO ports from passing the traffic to the FortiGate.
Scope
FortiGate.
Solution
- Using the GUI:
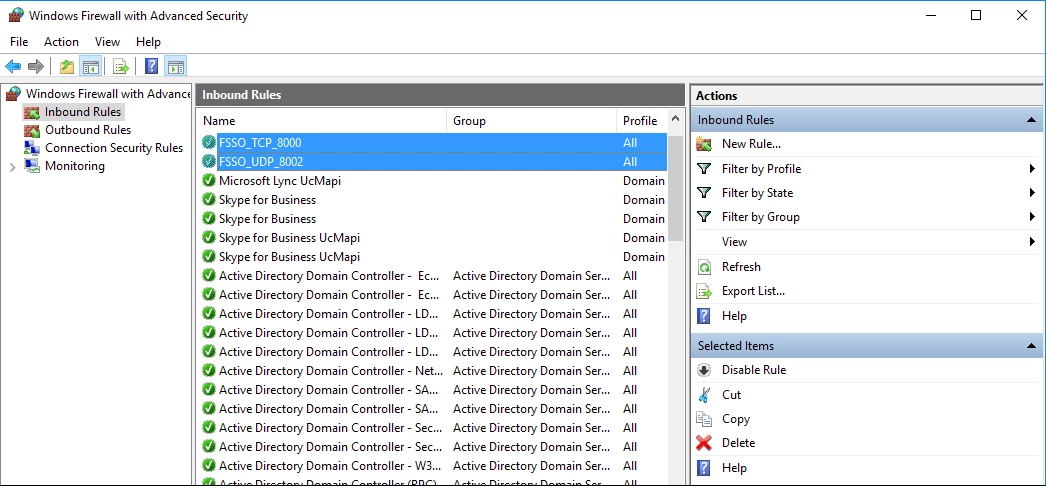
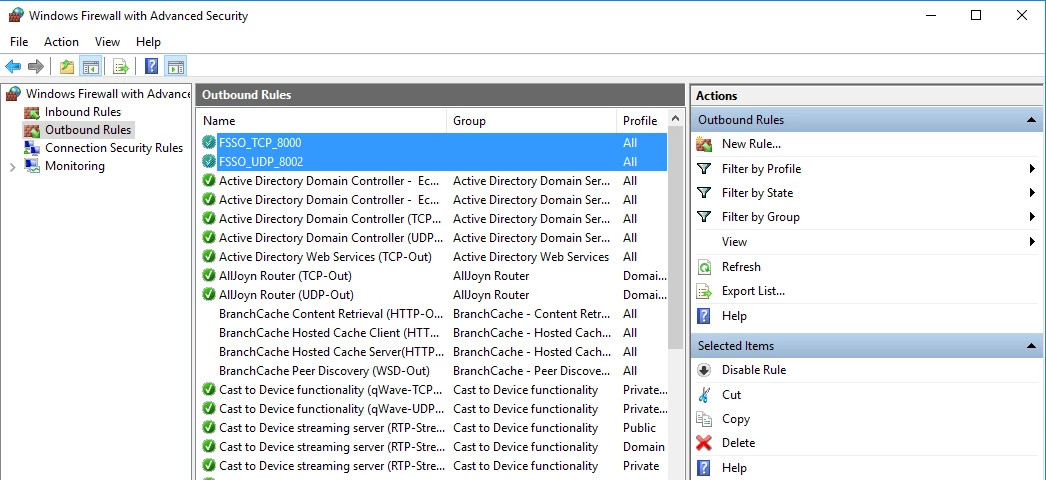
Go to Start Menu -> Control Panel -> Administrative Tools -> Windows Firewall with Advanced Security. - Using the command line:
For Inbound Traffic:
C:\>netsh advfirewall firewall add rule name="FSSO_TCP_8000" dir=in action=allow protocol=TCP localport=8000
C:\>netsh advfirewall firewall add rule name="FSSO_UDP_8002" dir=in action=allow protocol=UDP localport=8002
For Outbound Traffic:
C:\>netsh advfirewall firewall add rule name="FSSO_TCP_8000" dir=out action=allow protocol=TCP localport=8000
C:\>netsh advfirewall firewall add rule name="FSSO_UDP_8002" dir=out action=allow protocol=UDP localport=8002
CLI commands to change the default TCP 8000 in FortiOS are as follows:
set port <-- Enter an integer value from <1> to <65535> (default = <8000>).
end
diagnose debug enable
diagnose debug authd fsso server-status

