



Technical Tip: Administrative access: Disable Telnet permanently
Description
This article describes the option to permanently disable Telnet access to FortiGate.
Scope
FortiGate.
Solution
Starting v6.2.0, the option has been added that completely disables Telnet, removing the GUI options per interface and disabling the Telnet daemon.
When Telnet is disabled, the Telnet port cannot be configured, and access cannot be enabled on interfaces.
To disable Telnet:
config system global
set admin-telnet disable
end
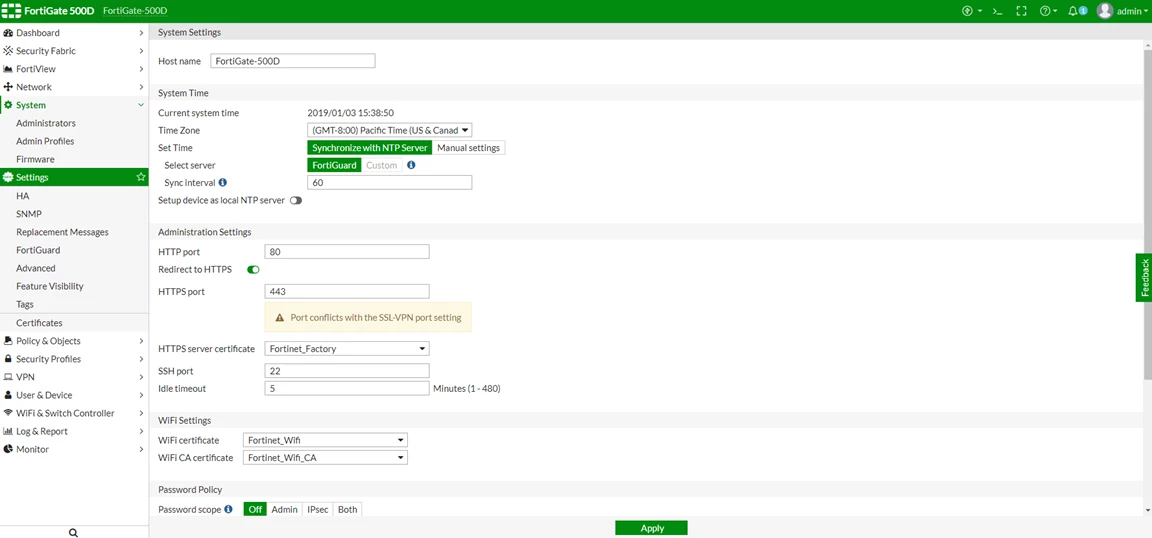
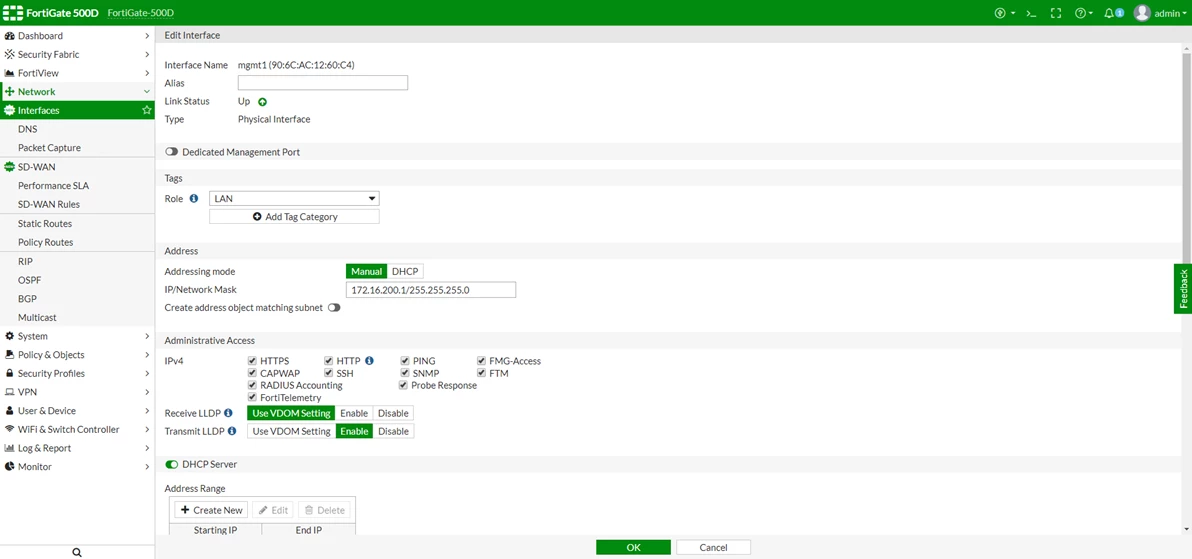
When disabled, the Telnet port is removed from the System -> Settings, and Telnet is no longer an administrative access option on the Network -> Interfaces.
config sys int
edit port1
set allowaccess ?
ping PING access.
https HTTPS access.
ssh SSH access.
snmp SNMP access.
http HTTP access.
fgfm FortiManager access.
radius-acct RADIUS accounting access.
probe-response Probe access.
fabric Security Fabric access.
ftm FTM access.
speed-test Speed test access.
To enable telnet, execute the following command:
config system global
set admin-telnet enable
set admin-telnet-port <port>
end
Note:
When the admin-telnet command is disabled in a FortiGate 6000F, 7000E, or 7000F platform, the command 'execute load-balance slot manage <slot-id>' returns a 'Connection timeout' message. Re-enabling the admin-telnet feature will not re-grant telnet access, and a 'Connection timeout' message will still be displayed. A unit reboot can fix the problem.
Related article:
Technical Tip: How to enable the free Telnet client to connect to FortiGate from Windows OS

