



Technical Tip: Adding BGP community string to route updates and control BGP routes advertisements by community
Description
This article describes how to configure BGP community strings to be added to path attributes for some NLRI (route updates), and control BGP routes advertisements by community
Scope
FortiGate or VDOM in NAT mode. Example given for v4.0 and above
Solution
Diagram:
The following diagram illustrates this example:
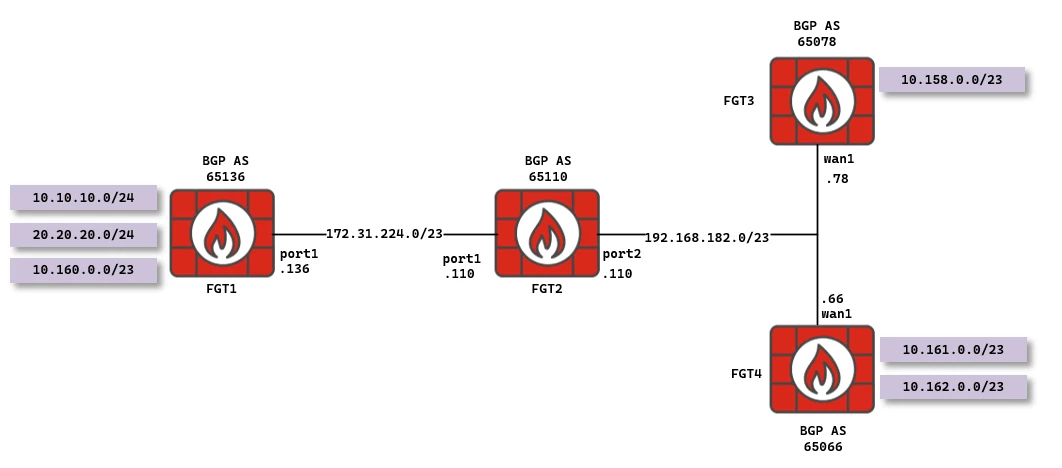
Expectations, requirements:
- FGT2 must redistribute the BGP routes to FGT3 and FGT4 as described below:
- Only routes announced with community string 65110:1 are advertised to FGT3.
- Only routes announced with community string 65110:2 are advertised to FGT4.
- FGT1 must announce the following routes in BGP:
- 10.10.10.0/24 with community string 65110:1.
- 20.20.20.0/24 with community string 65110:2.
- 10.160.0.0/23 without community string.
- 172.31.224.0/23 without community string.
- FGT3 is announcing in BGP the following routes:
- 10.158.0.0/23
- 192.168.182.0/23
- FGT4 is announcing in BGP the following routes:
- 10.161.0.0/23
- 10.162.0.0/23
- FGT3 and FGT4 are not BGP peers.
Configuration:
This will be achieved by configuring an access-list and a route-map-out on FortiGate1 (FGT1) and FortiGate 2 (FGT2) .
Only relevant parts of the configuration are provided in CLI format.
FGT1:
config router access-list
edit "net10"
config rule
edit 1
set prefix 10.10.10.0 255.255.255.0
set exact-match disable
next
end
next
edit "net20"
config rule
edit 1
set prefix 20.20.20.0 255.255.255.0
set exact-match disable
next
end
next
end
config router route-map
edit "community_set"
config rule
edit 1
set match-ip-address "net10"
set set-community "65110:1"
next
edit 2
set match-ip-address "net20"
set set-community "65110:2"
next
end
next
end
config router bgp
set as 65136
config neighbor
edit "172.31.224.110"
set remote-as 65110
set route-map-out "community_set"
next
end
config network
edit 1
set prefix 10.0.0.0 255.0.0.0
next
edit 2
set prefix 172.31.224.0 255.255.254.0
next
end
config redistribute "connected"
set status enable
end
set router-id 172.31.224.136
end
execute router restart
Warning:
This last command is needed to make all previous settings effective. It will however bring down and up all routing instances (BGP,OSPF...) for a short period of time, which will depend on each routing protocol convergence time.
FGT2:
config router community-list
edit "community1"
config rule
edit 1
set action permit
set match "65110:1"
next
end
next
edit "community2"
config rule
edit 1
set action permit
set match "65110:2"
next
end
next
end
config router route-map
edit "route_map_out_fgt3"
config rule
edit 1
set match-community "community1"
next
end
next
edit "route_map_out_fgt4"
config rule
edit 1
set match-community "community2"
next
end
next
end
config router bgp
set as 65110
config neighbor
edit "172.31.224.136"
set remote-as 65136
next
edit "192.168.182.78"
set remote-as 65078
set route-map-out "route_map_out_fgt3"
next
edit "192.168.182.66"
set remote-as 65066
set route-map-out "route_map_out_fgt4"
next
end
set router-id 172.31.224.110
end
execute router restart
Warning:
This last command is needed to make all previous settings effective. It will however bring down and up all routing instances (BGP,OSPF...) for a short period of time, which will depend on each routing protocol convergence time.
Verification:
Verification steps on FGT1 to FGT4:
On FGT3 and FGT4, only 1 BGP route is received.
FGT1 # get router info bgp route-map community_set
BGP table version is 3, local router ID is 172.31.224.136
Status codes: s suppressed, d damped, h history, * valid, > best, i - internal,
S Stale
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path
*> 10.10.10.0/24 0.0.0.0 32768 ?
*> 20.20.20.0/24 0.0.0.0 32768 ?
Total number of prefixes 2
FGT1 # get router info routing-table all
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area
* - candidate default
S* 0.0.0.0/0 [10/0] via 172.31.225.254, port1
C 10.10.10.0/24 is directly connected, port4
B 10.158.0.0/23 [20/0] via 172.31.224.110, port1, 00:39:41
C 10.160.0.0/23 is directly connected, port2
B 10.161.0.0/23 [20/0] via 172.31.224.110, port1, 00:39:41
B 10.162.0.0/23 [20/0] via 172.31.224.110, port1, 00:39:41
C 20.20.20.0/24 is directly connected, port4
C 172.31.224.0/23 is directly connected, port1
B 192.168.182.0/23 [20/0] via 172.31.224.110, port1, 00:39:41
FGT2 # get router info bgp summary
BGP router identifier 172.31.224.110, local AS number 65110
BGP table version is 3
3 BGP AS-PATH entries
2 BGP community entries
Neighbor V AS MsgRcvd MsgSent TblVer InQ OutQ Up/Down State/PfxRcd
172.31.224.136 4 65136 50 49 2 0 0 00:40:30 2
192.168.182.66 4 65066 49 49 2 0 0 00:40:25 3
192.168.182.78 4 65078 49 49 1 0 0 00:40:30 2
Total number of neighbors 3
FGT2 # get router info bgp community-info
Address Refcnt Community
[0x404237b8] (2) 65110:1
[0x40423788] (2) 65110:2
FGT2 # get router info bgp community 65110:1
BGP table version is 3, local router ID is 172.31.224.110
Status codes: s suppressed, d damped, h history, * valid, > best, i - internal,
S Stale
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path
*> 10.10.10.0/24 172.31.224.136 0 0 65136 ?
Total number of prefixes 1
FGT2 # get router info bgp community 65110:2
BGP table version is 3, local router ID is 172.31.224.110
Status codes: s suppressed, d damped, h history, * valid, > best, i - internal,
S Stale
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path
*> 20.20.20.0/24 172.31.224.136 0 0 65136 ?
Total number of prefixes 1
FGT2 # get router info bgp community-list community1
BGP table version is 3, local router ID is 172.31.224.110
Status codes: s suppressed, d damped, h history, * valid, > best, i - internal,
S Stale
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path
*> 10.10.10.0/24 172.31.224.136 0 0 65136 ?
Total number of prefixes 1
FGT2 # get router info bgp community-list community2
BGP table version is 3, local router ID is 172.31.224.110
Status codes: s suppressed, d damped, h history, * valid, > best, i - internal,
S Stale
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path
*> 20.20.20.0/24 172.31.224.136 0 0 65136 ?
Total number of prefixes 1
FGT2 # get router info bgp route-map route_map_out_fgt3
BGP table version is 3, local router ID is 172.31.224.110
Status codes: s suppressed, d damped, h history, * valid, > best, i - internal,
S Stale
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path
*> 10.10.10.0/24 172.31.224.136 0 0 65136 ?
Total number of prefixes 1
FGT2 # get router info bgp route-map route_map_out_fgt4
BGP table version is 3, local router ID is 172.31.224.110
Status codes: s suppressed, d damped, h history, * valid, > best, i - internal,
S Stale
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path
*> 20.20.20.0/24 172.31.224.136 0 0 65136 ?
Total number of prefixes 1
FGT2 # get router info routing-table all
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area
* - candidate default
S* 0.0.0.0/0 [10/0] via 172.31.225.254, port1
B 10.10.10.0/24 [20/0] via 172.31.224.136, port1, 00:43:26
B 10.158.0.0/23 [20/0] via 192.168.182.78, port2, 00:43:26
B 10.161.0.0/23 [20/0] via 192.168.182.66, port2, 00:43:21
B 10.162.0.0/23 [20/0] via 192.168.182.66, port2, 00:43:21
B 20.20.20.0/24 [20/0] via 172.31.224.136, port1, 00:43:26
C 172.31.224.0/23 is directly connected, port1
C 192.168.182.0/23 is directly connected, port2
FGT3 # get router info routing-table all
codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area
* - candidate default
S* 0.0.0.0/0 [10/0] via 192.168.183.254, wan1
B 10.10.10.0/24 [20/0] via 192.168.182.110, wan1, 00:43:37
C 10.158.0.0/23 is directly connected, internal
C 192.168.182.0/23 is directly connected, wan1
FGT3 # get router info bgp community-info
Address Refcnt Community
[0x404247ac] (1) 65110:1
FGT3 # get router info bgp community 65110:1
BGP table version is 28, local router ID is 192.168.182.78
Status codes: s suppressed, d damped, h history, * valid, > best, i - internal,
S Stale
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path
*> 10.10.10.0/24 192.168.182.110 0 0 65110 65136 ?
Total number of prefixes
FGT4 # get router info routing-table all
Codes: K - kernel, C - connected, S - static, R - RIP, B - BGP
O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, L1 - IS-IS level-1, L2 - IS-IS level-2, ia - IS-IS inter area
* - candidate default
S* 0.0.0.0/0 [10/0] via 192.168.183.254, wan1
C 10.161.0.0/23 is directly connected, wan1
C 10.162.0.0/23 is directly connected, wan1
B 20.20.20.0/24 [20/0] via 192.168.182.110, wan1, 16:07:46
C 192.168.182.0/23 is directly connected, wan1
FGT4 # get router info bgp community-info
Address Refcnt Community
[0x8c601a0] (1) 65110:2
FGT4 (root) # get router info bgp community 65110:2
BGP table version is 7, local router ID is 192.168.182.66
Status codes: s suppressed, d damped, h history, * valid, > best, i - internal,
S Stale
Origin codes: i - IGP, e - EGP, ? - incomplete
Network Next Hop Metric LocPrf Weight Path
*> 20.20.20.0/24 192.168.182.110 0 0 65110 65136 ?
Total number of prefixes 1
A packet capture can be used to see if the community is sent.
Run PCAP on the FortiGate network -> Diagnostics.
- Set the interface to the interface connected to the neighbor.
- Set the host to the neighbor.
- Set the port to 179.
- Select 'start capture'.
- Restart BGP with 'all' or 'soft' for the interface.
- Run the following:
execute router clear all bgp
- Check the PCAP.
- Expand BGP.
- Expand path attributes.
BGP debug commands:
FGT# diagnose ip router bgp all enable
FGT# diagnose ip router bgp level info
FGT# diagnose debug enable
To stop the debugging:
FGT# diagnose debug disable


