



Technical Tip: Activate 'Unreachable' Web Filtering and Email Filtering after FortiGate was updated
Description
This article describes how to resolve issues associated with email and web filtering are “Unreachable” after FortiGate was updated.
Solution
- Ensure the customer has the Email and Web Filtering services support activated. Go to support.fortinet.com and Log in with the credentials.
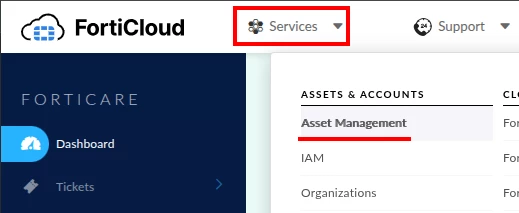
- Select Services -> Asset Management.
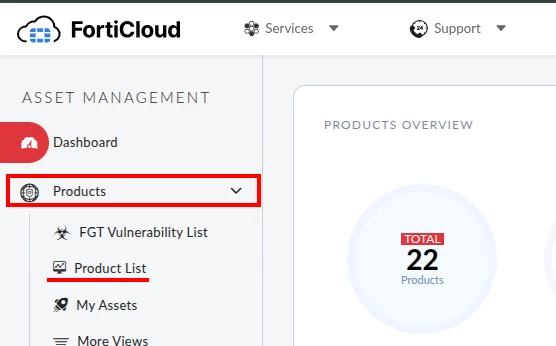
- On the next page, select Product -> Product List.
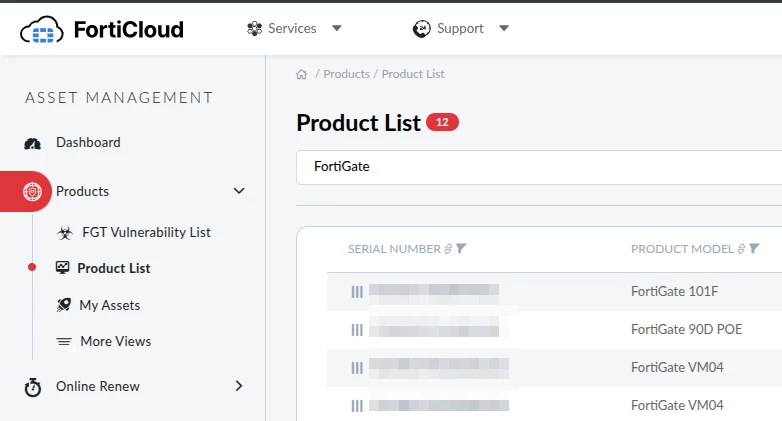
- Use the search box to find the device
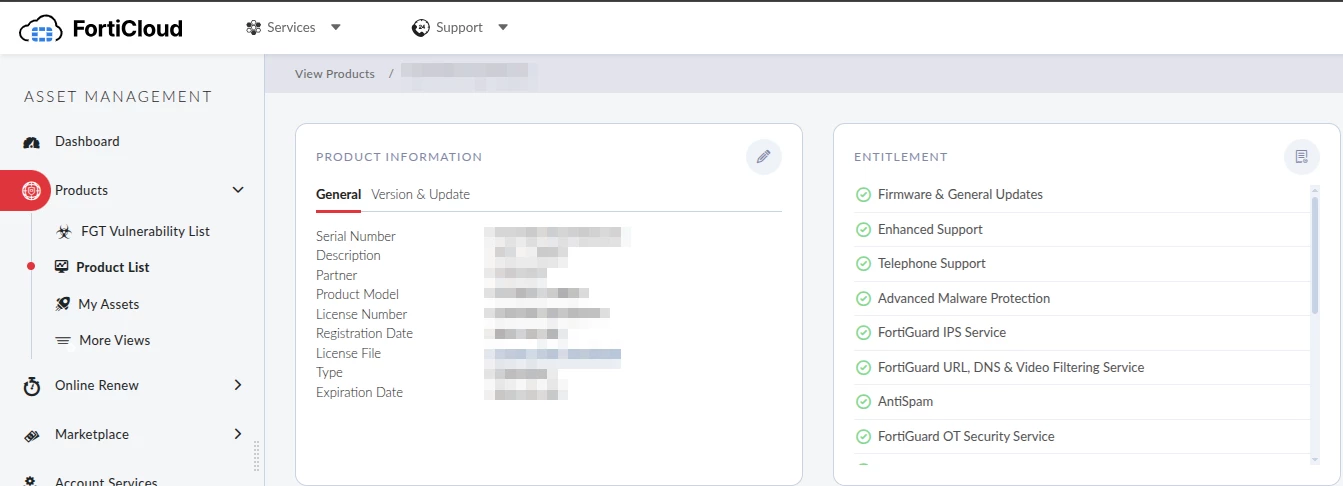
- Select the device and check the Entitlement widget.
- Try to force update the service in the CLI as follows:
execute update-now <-- It may take several minutes
- Webfilter/Antistpam services uses "service.fortiguard.net" and port 53 or port 8888, right communication must be ensured (either Layer 3 and Layer 4 including DNS-domain resolution)
- If the services are not activated with the previous command, try to change the ports, in System > FortiGuard. The default port is 53, but it can be changed to 8888. Try to probe both ports, select each and click “Test Availability” (refer to Figure 3).
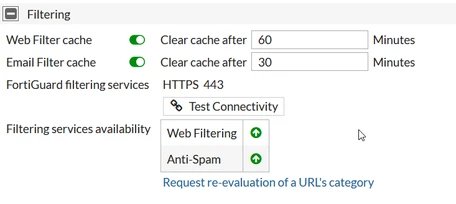
config system fortiguardset port 8888set protocol udp <--------- Can be set to https from v6.2.2.endIn v6.2, the FortiGuard server now supports HTTPS on port 443, which allows for FortiManager support.
FortiGuard filtering now supports the following protocol and port configurations:
- HTTPS: ports 443, 53, and 8888 (default port)
- UDP: ports 53 and 8888
- HTTP: port 80
Sometimes, this test may take several minutes (approximately 10 minutes or inclusive more). If it doesn't work, try rebooting the device.
- In case if it's still not working, it is possible to have problem resolving the URL service.fortiguard.net. Execute the following command in CLI:
execute ping service.fortiguard.net
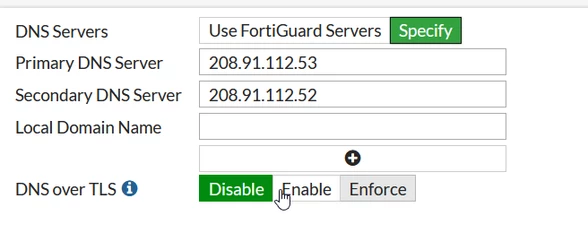
The result must to back the IP Address and must be successful. If not, review the DNS. Go to System > Network > DNS and check and change the DNS server. Try with FortiGuard DNS or use other DNS, for example Google DNS: 8.8.8.8 and 8.8.4.4 (refer to Figure 4).Figure 4
- The next debug is to identify other possible causes if the previous steps don’t work. (Information required for TAC diagnosis)
diagnose debug reset
diagnose debug enable
diagnose debug application update -1
execute update-nowThe following message will be displayed:
__upd_act_update[279]-Trying FDS 173.243.138.67-443 with AcceptDelta=1 <-- Chosen FortiGuard server to download information
extract_fds_info[245]-SEQ TZ IP:PORT TYPE <-- Shows the complete list of FortiGuard servers (service.fortiguard.com is OK)
extract_fds_info[314]- 0 009 173.243.138.79-443 3
extract_fds_info[314]- 1 009 173.243.138.80-443 3
extract_fds_info[314]- 2 -005 209.222.136.22-443 3
extract_fds_info[314]- 3 000 96.45.33.80-443 3update_status_obj[547]-AVDB contract expiry=Mon Jan 21 17:00:00 2019 <-- current expiration contract service: it shows for all databases (if it is different, please check with customer service)
level(10) alert(0)
update_status_obj[547]-ETDB contract expiry=Mon Jan 21 17:00:00 2019
level(10) alert(0)
update_status_obj[547]-EXDB contract expiry=Mon Jan 21 17:00:00 2019
level(10) alert(0)__upd_act_update[336]-Package installed successfully <-- update and package installation successfully
do_update[404]-UPDATE successful
After the result please enter the following commands to stop the debug:
diagnose debug disable
diagnose debug resetPlease, identify any issue in the communication.
Execute a sniffer with the next:
diagnose sniffer packet <wan_interface> 'tcp port 443' 1
This command is to know the problem with the Update.
- Other commands to know the updates status are as follows:
diagnose autoupdate status <-- to know IPS and Virus definition update)
FDN availability: available at Sun Oct 14 13:52:14 20xx
Virus definitions update: enablediagnose test update info <-- logs about last update
execute ping service.fortiguard.net (WEBFILTERING AND ANTISPAM)config system fortiguard
getwebfilter-force-off : disable <-- ensure it is disabled
endNote: If webfilter-force-off is enabled, run the following commands to disable the webfilter-force-off:config system fortiguardset webfilter-force-off disableend
Related Articles
Troubleshooting Tip: FortiGuard Web Filtering problems
Troubleshooting performance issues when FortiGuard Web Filtering is enabled - Low source port

