Technical Tip: Accessing specific Internet destinations via dial-up IPSec with split tunneling
| Description | This article describes accessing specific Internet destinations when remote FortiClient users connect to dial-up IPSec with split tunneling enabled. |
| Scope | FortiOS, FortiClient. |
| Solution | Split tunneling allows splitting Internet traffic from local traffic. When enabled, remote VPN users can access the Internet using the local ISP. When disabled, remote VPN users can access the Internet using FortiGate to apply the necessary security settings and for log monitoring.
In some cases, it is required to access specific Internet destinations with split tunneling enabled. To allow such access, configure the following:
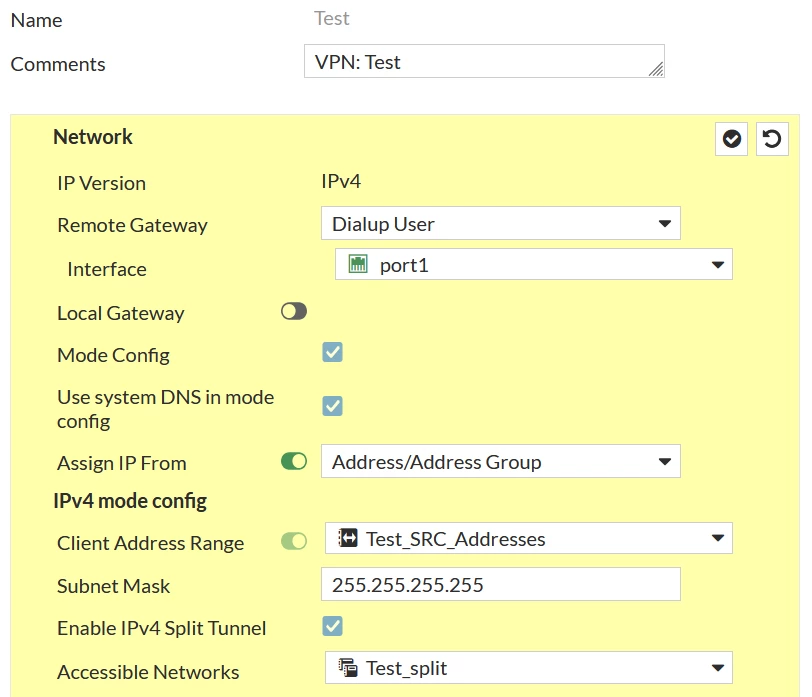
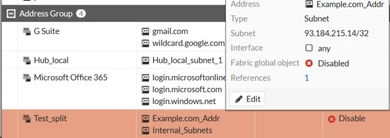
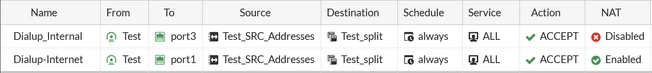
Example: Assume the configured dialup vpn tunnel name is 'Test', split-tunneling is enabled, addresses group name is Test_split, port1 is the public interface, and port3 is the internal interface. The requirement is to only allow the traffic of the Internet destination www.example.com (DNS resolves to: 93.184.215.14) to go via the Test tunnel. All other Internet destinations should go via the local ISP of the remote FortiClient user.
Relevant CLI:
config vpn ipsec phase1-interface edit "Test" set type dynamic next
config firewall addrgrp edit "Test_split" set member "Example.com_Addr" "Internal_Subnets" next
config firewall address edit "Test_SRC_Addresses" set type iprange next set subnet 93.184.215.14 255.255.255.255 next set subnet 192.168.1.0 255.255.255.0 next
config firewall policy edit 3 set name "Dialup_Internal" next set name "Dialup-Internet" next
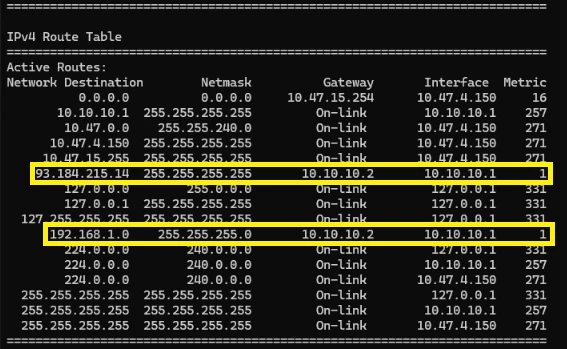
Verify the routes received on the Windows machine, and run the following command on the command prompt on Windows:
route print
Use 'netstat -nr' for MacOS devices.
Notes:
Related article: |