


Technical Note: Video/Telephony traffic issue giving 'No socket found. Drop' message
Description
Solution
This article addresses a Video/Telephony traffic issue when using IPPool NAT with a VIP different IP than FortiGate public (external) IP address.
If one hit one-way traffic issue (internet to private). Running "diag debug flow" command, one observes: "No socket found. Drop".
If one hit one-way traffic issue (internet to private). Running "diag debug flow" command, one observes: "No socket found. Drop".
Solution
Set 'config firewall ippool' with 'type one-to-one' instead of default 'overload'.
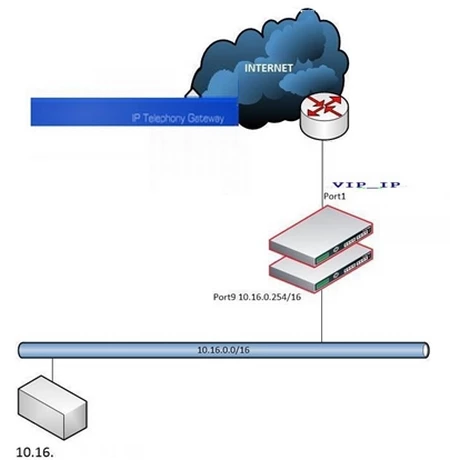
Problem
Extract of a typical default configuration with all TCP/UDP ports opened for NAT
Problem
diag debug flow filter add <VIP_ip>
diag debug flow trace start
trace_id=127 func=print_pkt_detail line=4471 msg="vd-root received a packet(proto=17,VIP_ip:port) from port11. " trace_id=127 func=resolve_ip_tuple_fast line=4532 msg="Find an existing session, id-19e1f6d5, original direction" trace_id=127 func=udp_rcv line=980 msg="No socket found. Drop."
Extract of a typical default configuration with all TCP/UDP ports opened for NAT
config firewall ippool edit "pool_VIP" set startip VIP_ip set endip VIP_ip ------------------------------------------------ config firewall vip edit "VIP_10.16_tcp" set comment "videoconf_TCP" set extip <VIP_ip > set extintf "port11" set portforward enable set mappedip "10.16.2.101" set extport 1-65535 set mappedport 1-65535 next edit "VIP_10.16_UDP" set comment "videoconf_UDP" set extip <VIP_ip > set extintf "port11" set portforward enable set mappedip "10.16.2.101" set protocol udp set extport 1-65535 set mappedport 1-65535
Related Articles


