



Technical Note: Using Certificates to authenticate users in SSL VPN
Description
Solution
In order to strength authentication between FortiGate and users, certificates can be used and two factor authentication enabled.
In this example, openSSL is used as an external CA.
In this example, openSSL is used as an external CA.
Solution
1. Create a CA with openSSL (Linux).
2. Generate a Certificate Request on the FortiGate and download.
3. Sign the FortiGate certificate.
4. Import the signed certificate (VPNSSL.cer) into the FortiGate as “local certificate”.
5. Create user certificate.
6. Import the usercert.pfx certificate into the Personal Section on the Certificates management console.
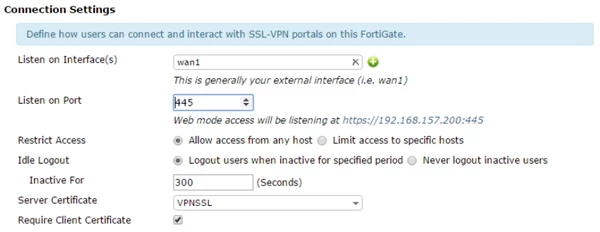
7. Create the SSL VPN (Tunnel Mode and Web Mode). Then, Select the “Server Certificate” imported in the step 4 and check “Require Client Certificate” in the SSL > Settings.
8. Create the PKI users (CLI only)
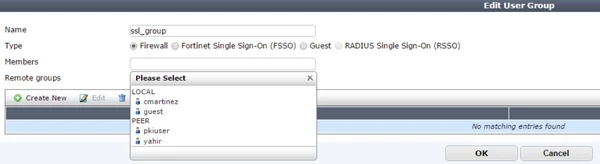
9. Now, associate the “PKIuser” with the SSL VPN “User Group” in User & Device > User > User Groups.
10. If imported correctly the User Certificate, the certificate should now be seen in FortiClient.
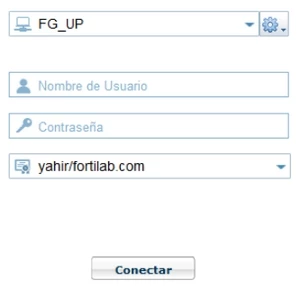
It is important also to enable the “client certificate” in FortiClient.
openssl req -new -x509 -days 3650 -keyout caprivatekey.pem -out cacertificate.pemcacertificate.pem is the public key and should be imported into the FortiGate and the user browser.
2. Generate a Certificate Request on the FortiGate and download.
3. Sign the FortiGate certificate.
openssl ca -out VPNSSL.cer -infiles /root/Downloads/VPNSSL.csr
4. Import the signed certificate (VPNSSL.cer) into the FortiGate as “local certificate”.
5. Create user certificate.
openssl req -new -nodes -out usercert.csr -keyout usercert.key
openssl ca -out usercert.cer -infiles usercert.csr
openssl pkcs12 -export -out usercert.pfx -inkey usercert.key -in usercert.cer
6. Import the usercert.pfx certificate into the Personal Section on the Certificates management console.
7. Create the SSL VPN (Tunnel Mode and Web Mode). Then, Select the “Server Certificate” imported in the step 4 and check “Require Client Certificate” in the SSL > Settings.
8. Create the PKI users (CLI only)
config user peer
edit "pkiuser"
set ca "CA_Cert_1"
set two-factor enable
set passwd
9. Now, associate the “PKIuser” with the SSL VPN “User Group” in User & Device > User > User Groups.
10. If imported correctly the User Certificate, the certificate should now be seen in FortiClient.
It is important also to enable the “client certificate” in FortiClient.

