



Technical Note: SSL warning with invalid CN error for internal CP authentication on FortiGate
Description
Scope
Solution
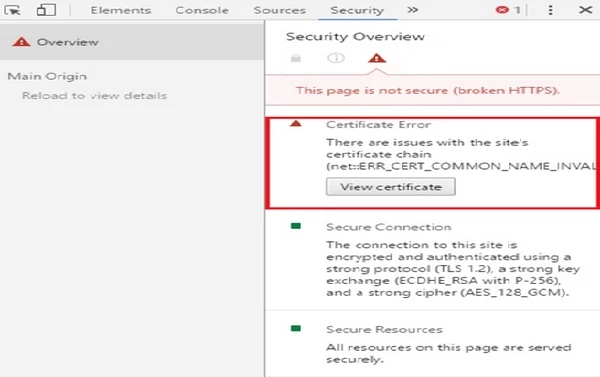
When a user connects to a wireless network with internal captive portal authentication, the device is redirected to url: https://x.x.x.x:1003. Since FortiGate is installed with standard certificate, the user is presented with an SSL warning error of using invalid common name because it does not match the IP address of the captive portal server (or FortiGate).
Scope
All versions.
Solution
This error can be avoided only by redirecting the wireless users to a Url that includes the FQDN of the FortiGate; instead of the FortiGate IP address. https://<FQDN>:1003
This can be implemented with the following commands:
Ensure also that there is a DNS resolution entry in the DNS server for the FQDN name with the FortiGate IP address.
This can be implemented with the following commands:
#config firewall auth-portal
#set portal-addr <FGT FQDN>
#end
Ensure also that there is a DNS resolution entry in the DNS server for the FQDN name with the FortiGate IP address.

