



Technical Note: How to create a certificate to use in SSL Inspection
Description
Solution
In order to strengthen inspection between a FortiGate and users, certificates can be used to inspect SSL connections.
Solution
1. Create a CA with openSSL (Linux)
Edit the file /etc/ssl/openssl.cnf
2. Generate a Certificate Request on the FortiGate and download.
3. Sign the FortiGate certificate.
5. Now use the imported certificate to inspect SSL connections.
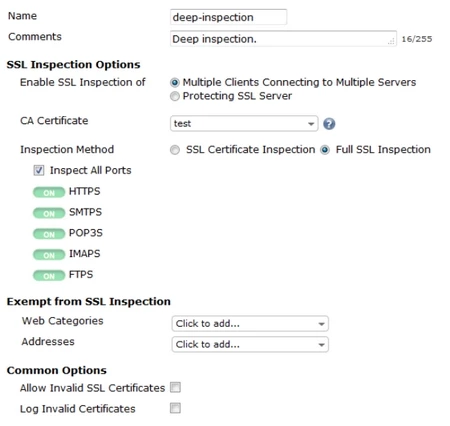
6. Security certificate warnings can be avoided by installing the cacert.pem file in your browsers.
Edit the file /etc/ssl/openssl.cnf
dir = /root/CALook for basicConstraints and change to TRUE:
[ policy_match ]
countryName = optional
stateOrProvinceName = optional
organizationName = optional
organizationalUnitName = optional
commonName = supplied
emailAddress = optional
basicConstraints=CA:TRUECreate the following folders:
cd /rootThe certificates can now be created:
mkdir CA
chmod 700 CA
cd CA
mkdir certs private newcerts
echo 1000 > serial
touch index.txt
openssl req -new -x509 -days 3650 -keyout private/cakey.pem \ -out cacert.pem -config /etc/ssl/openssl.cnfcacert.pem is the public key and should be imported into the FortiGate and the user browser.
2. Generate a Certificate Request on the FortiGate and download.
3. Sign the FortiGate certificate.
openssl ca -out test.cer -infiles /root/Downloads/ test.csr4. Import the signed certificate (test.cer) into the FortiGate as “local certificate”.
5. Now use the imported certificate to inspect SSL connections.
6. Security certificate warnings can be avoided by installing the cacert.pem file in your browsers.

