


Technical Note: How to allow communication between PPTP clients and remote networks through IPsec
Description
Scope
Solution
This article provides an example of how to allow communication between PPTP clients and remote networks through IPsec.
Scope
All FortiGates.
Solution
The following diagram shows there is already an IPsec tunnel between Site A and Site B, both of which are FortiGates. Site A is configured as PPTP server for its PPTP clients. These clients should be able to ping and be pinged from 192.168.10.0/24 which is the local network behind Site B.
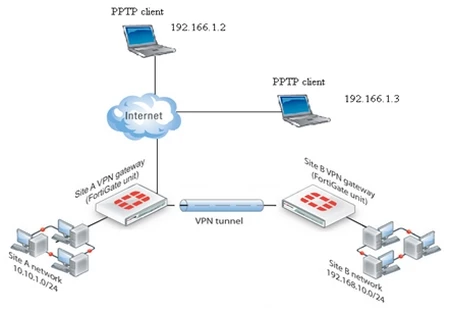
The PPTP configuration on Site A is:
To access internal resources:
To access internet once connected to PPTP:
Regular internal to internet policy:
Integrating PPTP in IPsec policies:
Regular IPsec policies:
Site B will include static routes for 10.10.1.0/24 and 192.166.1.0/28 . These subnets will also be defined in the IPsec policies as remote networks.
Testing the connection from Site A to PPTP client via ping:
On Site A there is a host 10.10.1.5 which is pinging 192.166.1.2 (PPTP client)
15.512989 internal in 10.10.1.5 -> 192.166.1.2: icmp: echo request
15.513014 wan1 out 192.166.1.1 -> 192.166.1.2: icmp: echo request
15.514236 wan1 in 192.166.1.2 -> 192.166.1.1: icmp: echo reply
15.514245 internal out 192.166.1.2 -> 10.10.1.5: icmp: echo reply
On Site B there is a host 192.168.10.8 which is pinging 192.166.1.2 (PPTP client)
3.568954 to_SiteB in 192.168.10.8 -> 192.166.1.2: icmp: echo request
3.569235 wan1 out 192.168.10.8 -> 192.166.1.2: icmp: echo request
3.570450 wan1 in 192.166.1.2 -> 192.168.10.8: icmp: echo reply
3.570457 to_SiteB out 192.166.1.2 -> 192.168.10.8: icmp: echo reply
The PPTP configuration on Site A is:
Site A # conf vpn pptp
Site A (pptp) # sh full-configuration
config vpn pptp
set status enable
set ip-mode range
set eip 192.166.1.14
set sip 192.166.1.1
set usrgrp "Guest-group"
end
Site A # config firewall address
Site A (address) # edit pptp
Site A (pptp) # set subnet 192.166.1.0 255.255.255.240
Site A (pptp) # next
Site A (address) # end
To access internal resources:
Site A # conf firewall policy
edit 1
set srcintf "wan1"
set dstintf "internal"
set srcaddr "pptp"
set dstaddr "10.10.1.0/24"
set action accept
set schedule "always"
set service "ALL"
To access internet once connected to PPTP:
edit 2
set srcintf "wan1"
set dstintf "wan1"
set srcaddr "pptp"
set dstaddr "all"
set action accept
set schedule "always"
set service "ALL"
set nat enable
next
Regular internal to internet policy:
edit 3
set srcintf " internal"
set dstintf "wan1"
set srcaddr "10.10.1.0/24"
set dstaddr "all"
set action accept
set schedule "always"
set service "ALL"
set logtraffic all
set nat enable
Integrating PPTP in IPsec policies:
edit 12
set srcintf "wan1"
set dstintf "to_SiteB"
set srcaddr "pptp"
set dstaddr "192.168.10.0/24"
set action accept
set schedule "always"
set service "ALL"
next
edit 13
set srcintf "to_SiteB"
set dstintf "wan1"
set srcaddr "192.168.10.0/24"
set dstaddr "pptp"
set action accept
set schedule "always"
set service "ALL"
Regular IPsec policies:
edit 9
set srcintf "to_SiteB"
set dstintf "internal"
set srcaddr "192.168.10.0/24"
set dstaddr "10.10.1.0/24"
set action accept
set schedule "always"
set service "ALL"
next
edit 10
set srcintf "internal"
set dstintf "to_SiteB"
set srcaddr "10.10.1.0/24"
set dstaddr "192.168.10.0/24"
set action accept
set schedule "always"
set service "ALL"
next
Site B will include static routes for 10.10.1.0/24 and 192.166.1.0/28 . These subnets will also be defined in the IPsec policies as remote networks.
Testing the connection from Site A to PPTP client via ping:
On Site A there is a host 10.10.1.5 which is pinging 192.166.1.2 (PPTP client)
15.512989 internal in 10.10.1.5 -> 192.166.1.2: icmp: echo request
15.513014 wan1 out 192.166.1.1 -> 192.166.1.2: icmp: echo request
15.514236 wan1 in 192.166.1.2 -> 192.166.1.1: icmp: echo reply
15.514245 internal out 192.166.1.2 -> 10.10.1.5: icmp: echo reply
On Site B there is a host 192.168.10.8 which is pinging 192.166.1.2 (PPTP client)
3.568954 to_SiteB in 192.168.10.8 -> 192.166.1.2: icmp: echo request
3.569235 wan1 out 192.168.10.8 -> 192.166.1.2: icmp: echo request
3.570450 wan1 in 192.166.1.2 -> 192.168.10.8: icmp: echo reply
3.570457 to_SiteB out 192.166.1.2 -> 192.168.10.8: icmp: echo reply


