Technical Note: Enable SIP Application Layer Gateway (ALG) on a FortiGate unit
Description
When configuring SIP features on a FortiGate unit, it is recommended to disable the SIP session-helper and work with the SIP Application Layer Gateway, to ensure compatibility across SIP systems.
Here are the steps to configure that:
1. Check the session-helper number in the CLI:
FGT# show system session-helper
…response should be similar to:
edit 12 #ID set name sip set port 5060 set protocol 17 next |
"#ID" indicates the line with an ID number, to be used for the next step
2. Remove this session-helper
FGT# config system session-helper
FGT#(session-helper) delete 12
FGT#(session-helper) end
3. Clear SIP sessions
Removing the session helper helps to ensure that new SIP sessions will not use the session-helper.
For existing SIP sessions (and their associated expectation sessions for the required pinholes) to be cleared, chose one of the following options:
1) wait for the existing sessions to timeout from the FortiGate session table
2) manually clear the existing sessions
3) reboot the FortiGate
4. Create a Protection Profile with VoIP enabled.
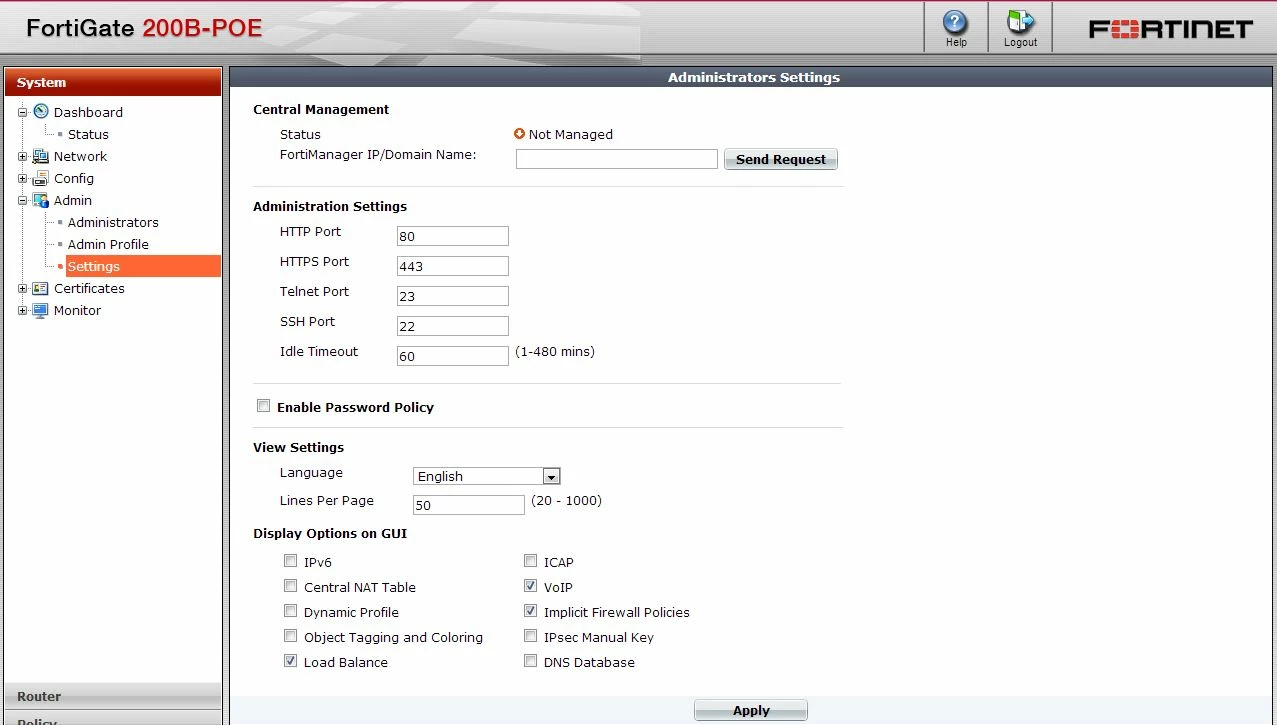
4.1 Enable the VoIP settings in the GUI. Go to: System > Admin > Settings > Display Option on GUI > Tick VoIP
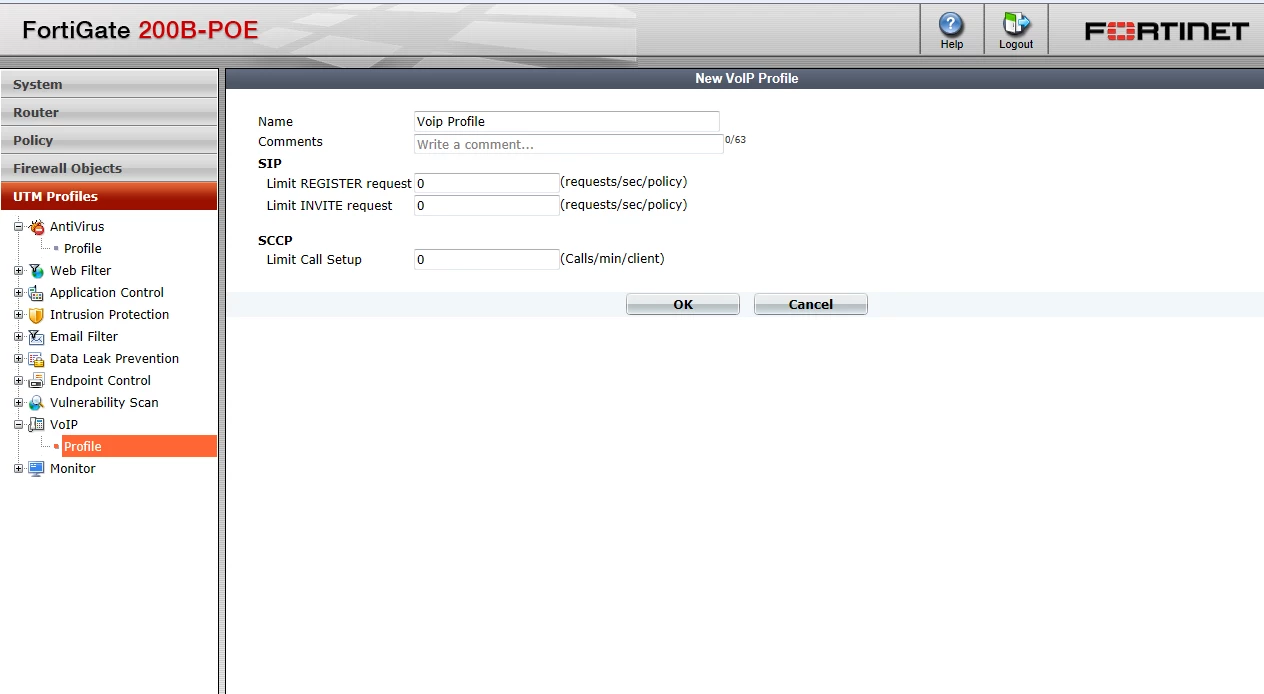
4.2 Create a new VoIP profile under "UTM Profiles". Go to: UTM Profiles > VoIP > Click Create New > VoIP_Profile
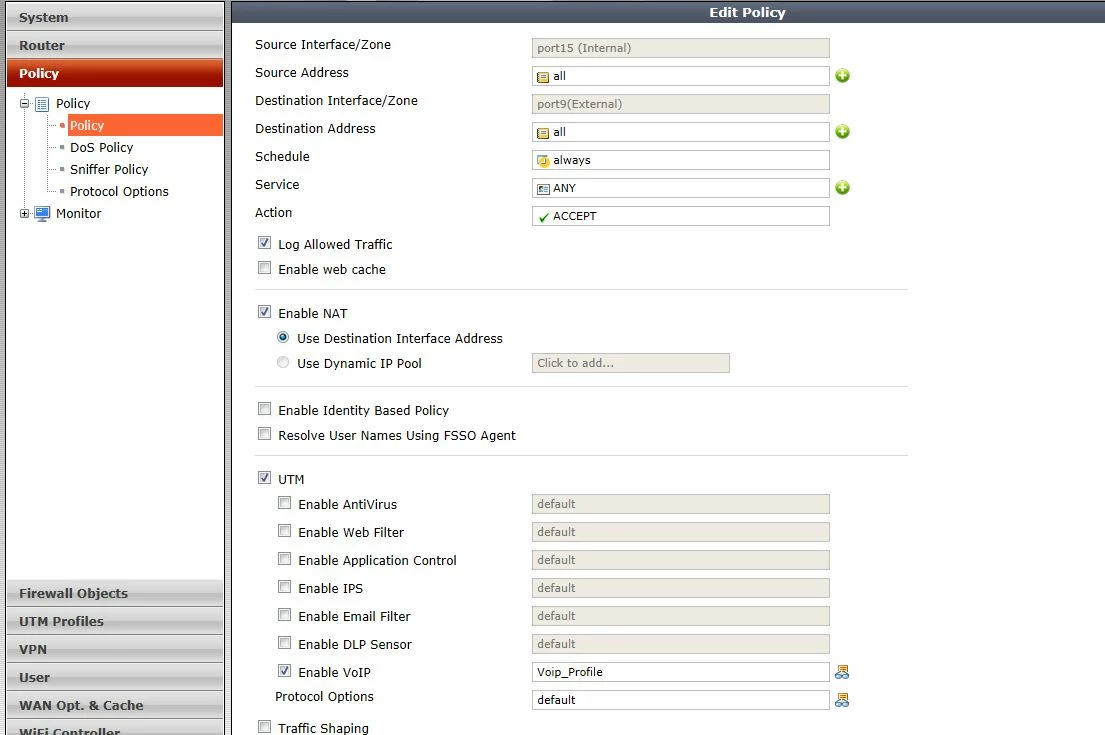
4.3 Enable the VoIP profile under the appropriate firewall policies. Go to: Policy > Enable UTM-Tick > Enable VoIP > Choose VoIP profile