


Technical Note: EAP type to enable on RADIUS server when tunnel termination is enabled on FortiGate for PEAP-MSCHAPV2 authentication
Description
Solution
This article explains which EAP type should be enabled on the RADIUS server when tunnel termination is enabled on the FortiGate for PEAP-MSCHAPV2 authentication.
Solution
The purpose of enabling tunnel termination for wpa2-enterprise profile with RADIUS authentication on the FortiGate is to have a temporary working solution for enterprise users when the RADIUS server certificate is expired or there is no certificate available on the newly installed RADIUS server.
This feature can be enabled on SSID page with wpa2-enterprise option by selecting local and mapping user group that contains RADIUS server as the member.
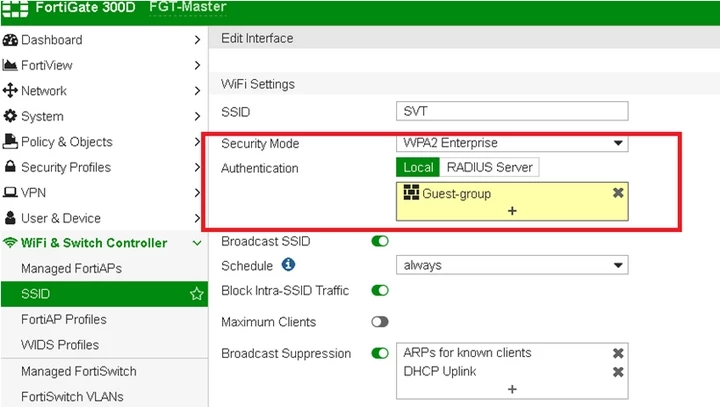
Since the outer tunnel is terminated at the FortiGate, mschapv2 should be enabled as the EAP type for the policies on the RADIUS server and not PEAP.
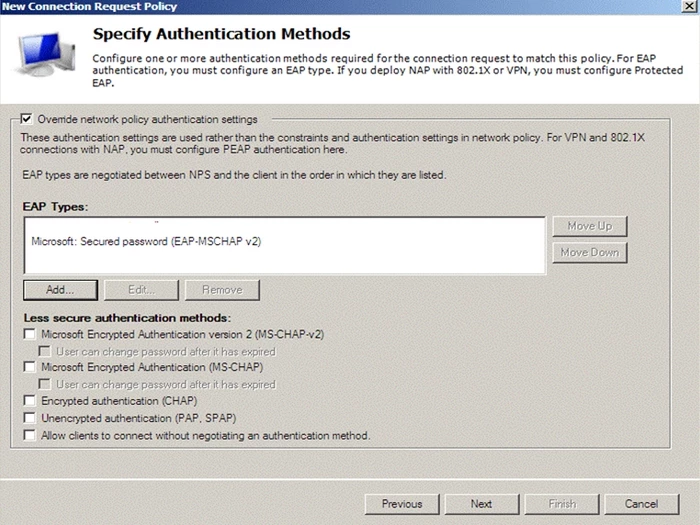
Sample NPS configuration for EAP type in Tunnel Termination
This feature can be enabled on SSID page with wpa2-enterprise option by selecting local and mapping user group that contains RADIUS server as the member.
Since the outer tunnel is terminated at the FortiGate, mschapv2 should be enabled as the EAP type for the policies on the RADIUS server and not PEAP.
Sample NPS configuration for EAP type in Tunnel Termination


