



Technical Note: DHCP IP address reservation with Dial up IPsec VPN
Description
Solution
This article addresses the need of some users to have the same IP address whenever they connect to VPN. To do this, DHCP over IPsec can be enabled and access control is possible with MAC reservation.
Solution
1) Dial up VPN can be created with the wizard.
2) Create the DHCP Server.
a) By GUI.
Go to System > Network > Interfaces > Interface created by wizard.
Assign IP address to the interface
b) By CLI.
3) Disable “Mode Config” in the VPN configuration.
a) By GUI.
a) By CLI.
4) By CLI enable DHCP over IPsec in the VPN phase 2.
5) Enable DHCP over IPsec in FortiClient.
2) Create the DHCP Server.
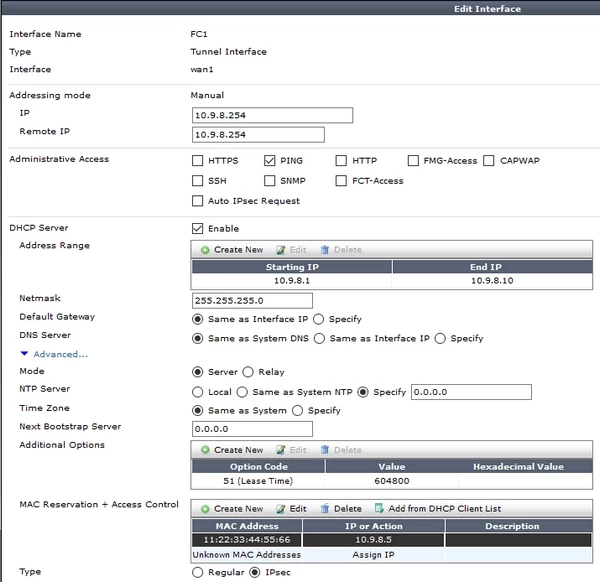
a) By GUI.
Go to System > Network > Interfaces > Interface created by wizard.
Assign IP address to the interface
IP: 10.9.8.254Enable DHCP Server
Remote IP: 10.9.8.254
Address range: 10.9.8.1 - 10.9.8.10IP address Reservation
Netmask: 255.255.255.0
Add a MAC Reservation + Access Control entry:
MAC: <network card MAC address from you are connecting to the VPN>
IP: <IP address to reserve>
Action: Reserve IP
Type: IPsec
b) By CLI.
config system dhcp server
edit 3
set dns-service default
set default-gateway 10.9.8.254
set netmask 255.255.255.0
set interface "FC1"
config ip-range
edit 1
set start-ip 10.9.8.1
set end-ip 10.9.8.10
next
end
set timezone-option default
set server-type ipsec
config reserved-address
edit 1
set ip 10.9.8.5
set mac 11:22:33:44:55:66
next
end
next
end
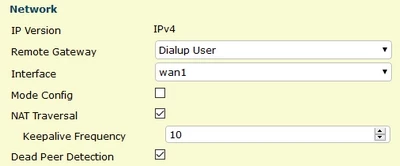
3) Disable “Mode Config” in the VPN configuration.
a) By GUI.
a) By CLI.
config vpn ipsec phase1-interface
edit "FC1"
set type dynamic
set interface "wan1"
set ip-version 4
set ike-version 1
set local-gw 0.0.0.0
set nattraversal enable
set keylife 86400
set authmethod psk
set mode aggressive
set peertype any
set mode-cfg disable HIGHLIGHT
set proposal aes128-sha256 aes256-sha256 3des-sha256 aes128-sha1 aes256-sha1 3des- sha1
set add-route enable
set localid ''
set localid-type auto
set negotiate-timeout 30
set fragmentation enable
set dpd enable
set forticlient-enforcement enable
set comments "VPN: FC1 (Created by VPN wizard)"
set npu-offload enable
set dhgrp 14 5
set wizard-type custom
set xauthtype auto
set authusrgrp "VPN"
set default-gw 0.0.0.0
set default-gw-priority 0
set psksecret ENC
set keepalive 10
set distance 15
set priority 0
set dpd-retrycount 3
set dpd-retryinterval 5
set xauthexpire on-disconnect
next
end
4) By CLI enable DHCP over IPsec in the VPN phase 2.
config vpn ipsec phase2-interface
edit "FC1"
set phase1name "FC1"
set comments "VPN: FC1 (Created by VPN wizard)"
set dhcp-ipsec enable HIGHLIGHT
next
end
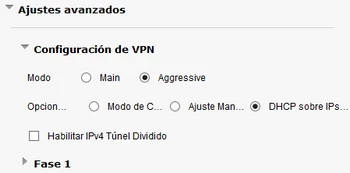
5) Enable DHCP over IPsec in FortiClient.
