| Solution | - In the FortiGate Interface CAPWAP (UDP ports 5246, 5247) captures, it can be noted that after FortiExtender and FortiGate Client and Server Hello Done message exchange, the captures show 'Description: Bad Certificate (42)' DTLS Alert - as shown below:
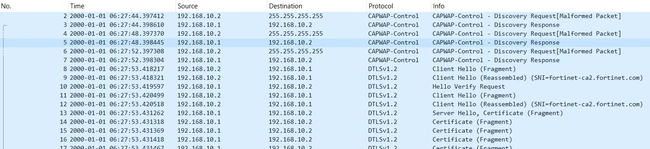 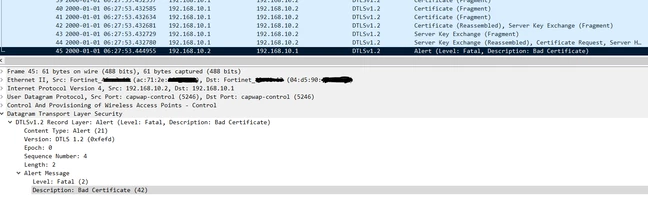
- This DTLS Alert can occur when the Date & Time on the FortiGate is not valid. In the above picture, it can be noted that the Year is 2000. Therefore, to resolve the CAPWAP connection issue between FortiGate and the FortiExtender, set the Date & Time manually (workaround) or synchronize the FortiGate Date & Time with NTP.
-
The 'get extender status' output on the FortiExtender CLI will show 'CWWS_RUN' after the CAPWAP DTLS connection is successful with the FortiGate: # get extender status
Extender Status
name : FXE11FTQ22XXXXX
mode : CAPWAP
fext-addr : 192.168.10.2
ingress-intf : port4
fext-wan-addr : 0.0.0.0
controller-addr : 192.168.10.1:5246,25246
controller-name : FGT60FTKXXXXX
uptime : 0 days, 0 hours, 0 minutes, 23 seconds
management-state : CWWS_RUN CAPWAP Control Channel state machine. |





