



Threat Coverage: How FortiEDR blocks DearCry ransomware attacks
Description
This article describes how FortiEDR natively blocks the DearCry ransomware attack.
DearCry, or DoejoCrypt, is installed in human-operated attacks using the MS.Exchange server exploits.
Here are the stages of execution observed in FortiEDR.
Pre-execution:
Once executed FortiEDR blocks:
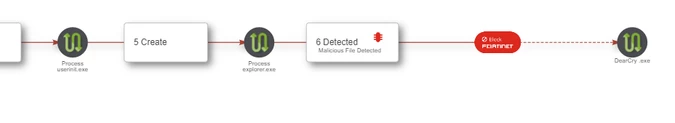
Rules Triggered:
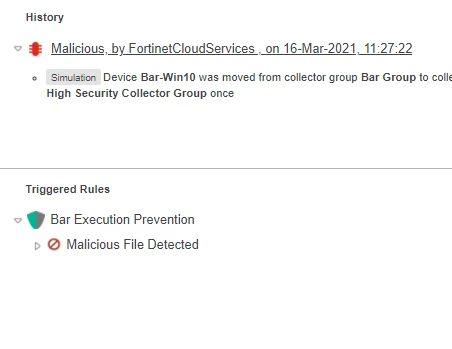
Process Termination:

Post-execution:
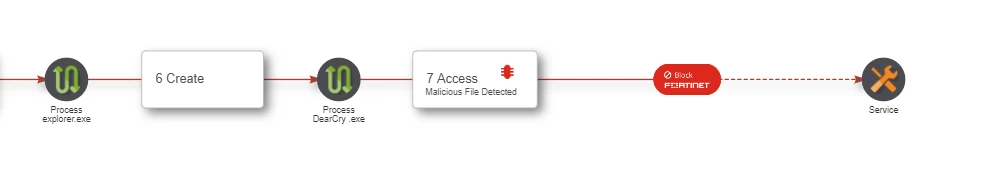
Once executed with Execution policies set to simulation, FortiEDR blocks the attempt of encrypting the files – starting with desktop.ini with the extension of .CRYPT:
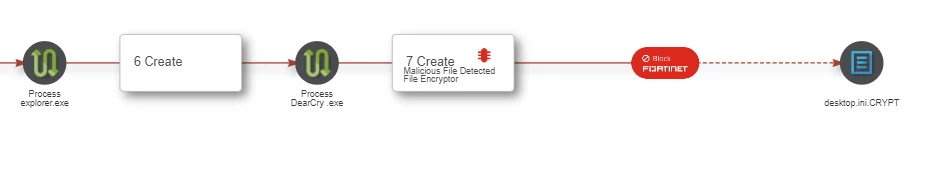
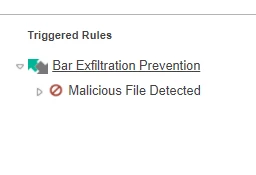
Rules Triggered:
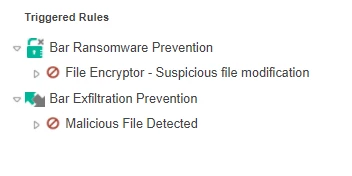
Service creation blocked:
Additional Information:
An example SHA256 hash associated with DearCry:
e044d9f2d0f1260c3f4a543a1e67f33fcac265be114a1b135fd575b860d2b8c6
For more information about this ransomware attack, see the following FortiGuard Threat Signal Report:

