Technical Tip: Pre-Execution Events and Threat Hunting Data Collection
| Description | This article discusses a common question pertaining to pre-execution security events and Threat Hunting data collection. |
| Scope | FortiEDR 5.0+ |
| Solution | FortiEDR offers several types of security policies and rules which allow or block processes and files. Separately, FortiEDR offers Threat Hunting capabilities which enrich analysts to perform deep, historic forensics investigations.
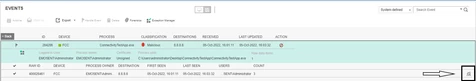
In some cases, users may view an event in the Event Viewer and select the ‘Threat Hunting’ icon:
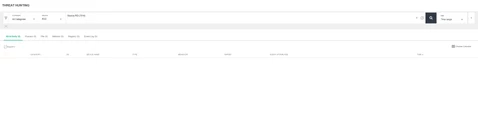
Only to find no Threat Hunting data is returned:
If the security rule, found in Event Viewer, is for ‘Malicious File Detected’, then this is considered expected behavior.
Execution Prevention (aka pre-execution prevention) relies on FortiEDR’s Next Generation Antivirus (NGAV) engine. Security events triggered here will show under the 'Malicious File Detected” security rule. In such case, the file read attempt on the endpoint is blocked prior to reaching the Collectors Threat Hunting function and thus no Threat Hunting data is collected. |