There are two methods:
Option 1: Search the Incidents page.
Use the Incidents page in combination with the Advanced Filter to search for the affected hostname. This will display all events associated with the endpoint. The event that caused the Collector to enter Isolation Mode is identified by the Isolation icon displayed next to the corresponding Event ID.
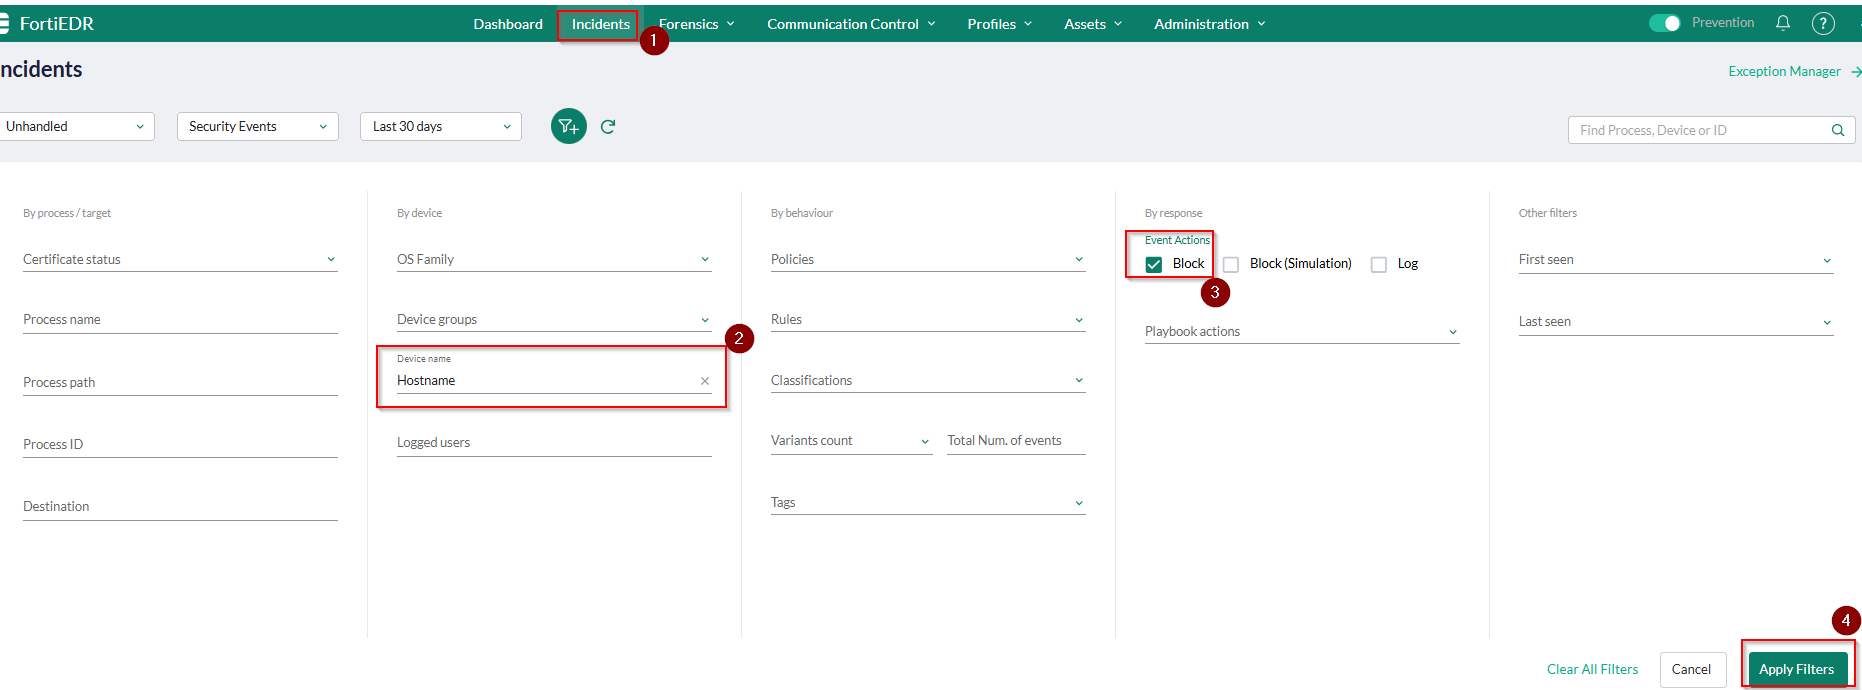
Note: This method may require more time if the affected endpoint has a large number of logged events.
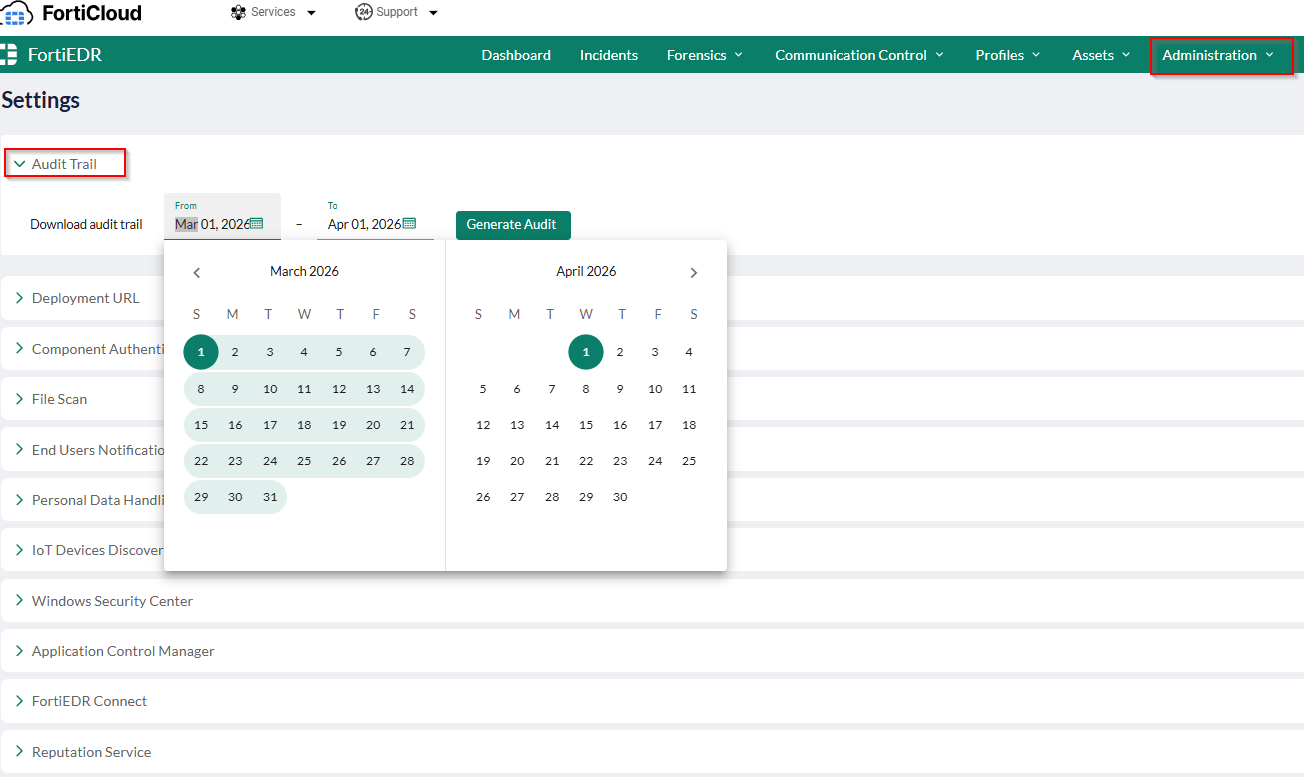
Option 2: Export the Audit Logs (Recommended).
Export the Audit Logs for the date/time when the isolation event occurred.
In the exported Excel file, use the Find All function (Ctrl + F) to search for the keyword 'isolated'. This will display all Collector isolation events recorded in the audit logs.
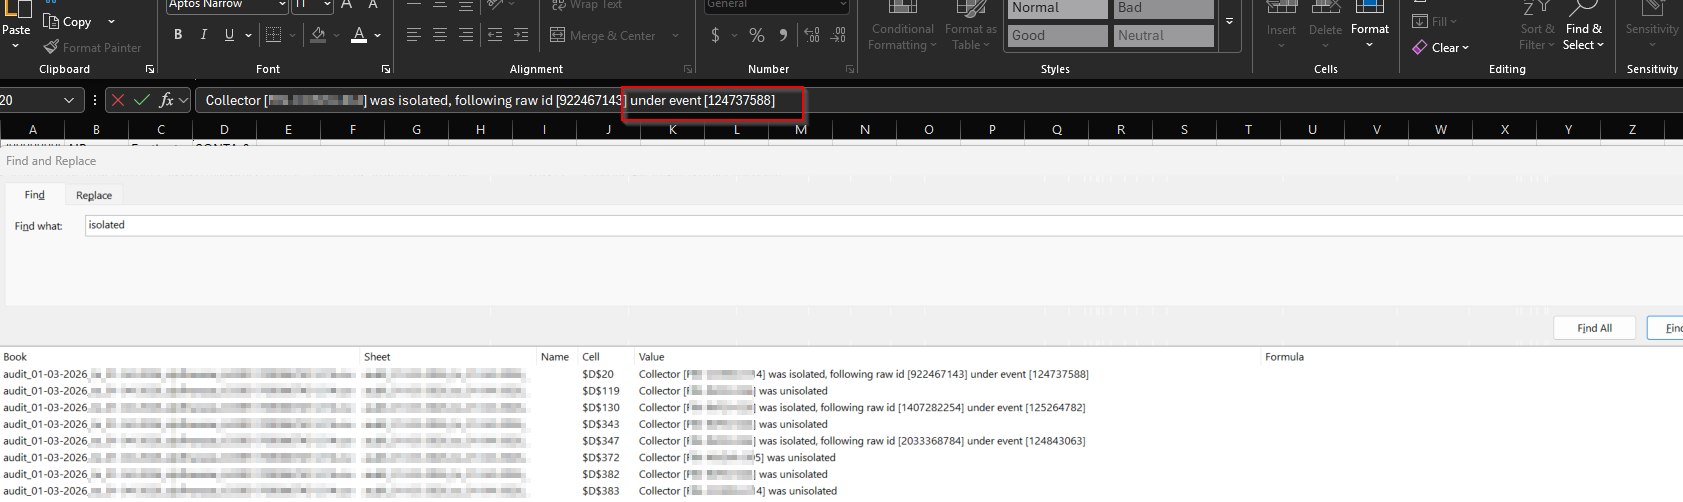
This method is typically faster because the audit logs record the Collector isolation action directly, making it easier to identify the corresponding Event ID. Once the Event ID has been identified, navigate to the Incidents page and use the Event ID as a filter to locate the associated incident.
| 



