When sending an email using the FortiDLP New Outlook add-in, FortiDLP will process the email and determine whether the email should be blocked. In some scenarios, New Outlook or OWA will prompt pop-ups for Add-ins if they take long periods of time to complete before an email can be sent. The following flowchart describes the process FortiDLP takes before sending or blocking an email and depicts at which point pop-ups can be viewed.
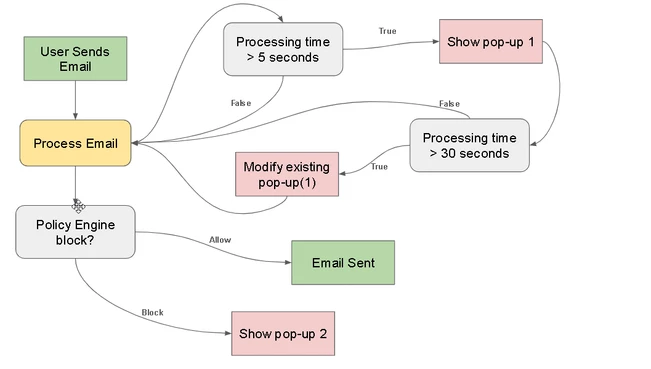
In the scenarios where pop-ups are presented due to processing time, these pop-ups are non-configurable and enforced by Microsoft (outside of the scope of the add-on itself). The following messages are expected from New Outlook/OWA when sending an email when using the FortiDLP add-in:
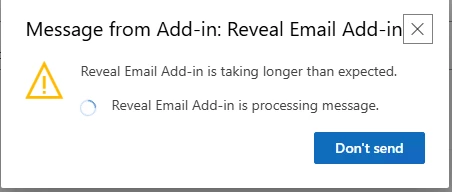
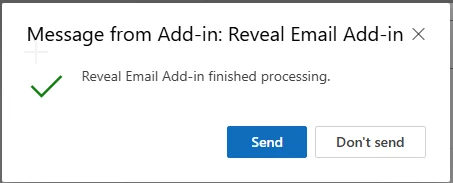
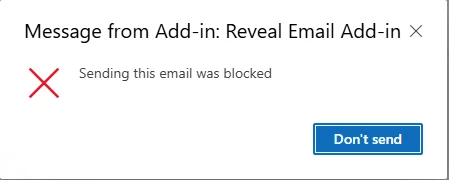
There are additional scenarios that may occur as a result of Microsoft issues. See Error shown to user (and fetch call cancelled) if onAppointmentSend event execution happens when other launch event(s) are running on an appointment. In this case, there is a scenario where an event may be cancelled when another event is called, and it creates a pop-up for the user like the following:
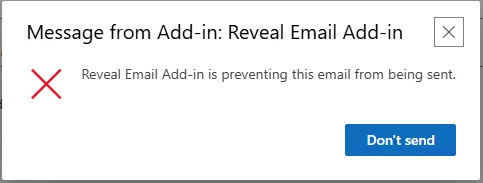
This is not directly caused by the FortiDLP Agent, but may depend on the events that have occurred and their timing. Users can proceed by selecting the 'Don't Send' option and re-attempting to send the email.
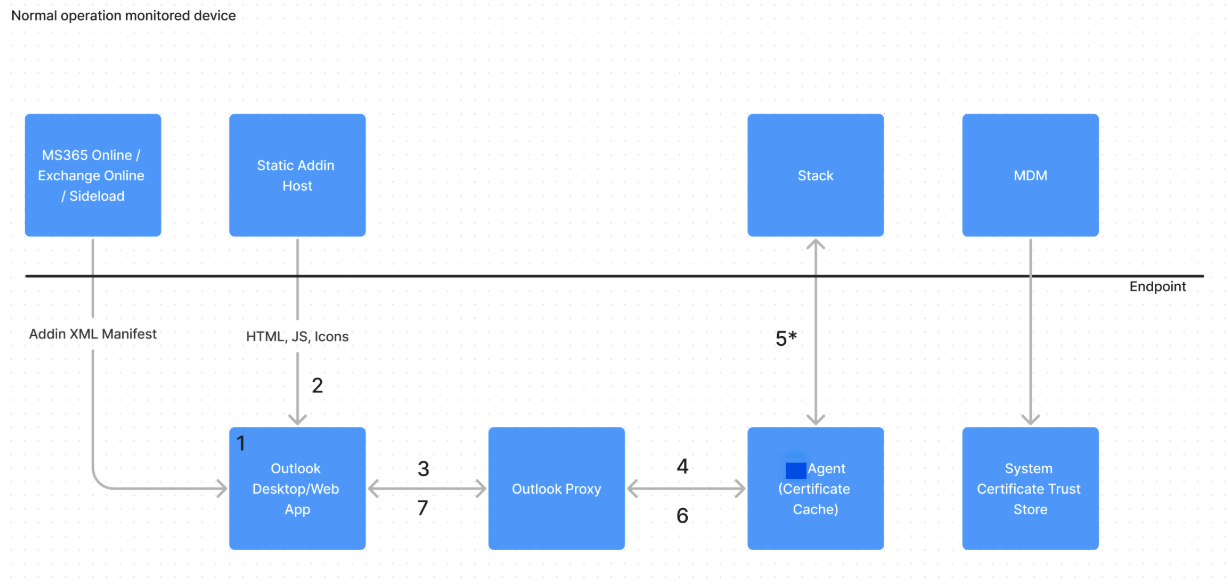 The FortiDLP/Outlook communications are detailed as follows: Microsoft 365 admin informs the Outlook service that the FortiDLP add-in is to be loaded. Outlook downloads all necessary code from FortiDLP servers to run the add-in. Outlook communicates with a locally hosted FortiDLP proxy on port 13243. The proxy communicates with local thr FortiDLP agent to generate a verdict on sending the email. The agent receives updates from the FortiDLP platform every 5 minutes about policy updates and configuration. The FortiDLP agent provides a verdict to allow email to be sent based on existing policy configuration. The proxy sends the verdict response back back to the hosted Outlook add-on.
| 




