



Technical Tip: Outlook warnings after installing the FortiDLP agent
| Description | This article discusses Outlook warnings for the FortiDLP Legacy Outlook (VSTO) plugin. |
| Scope | FortiDLP. |
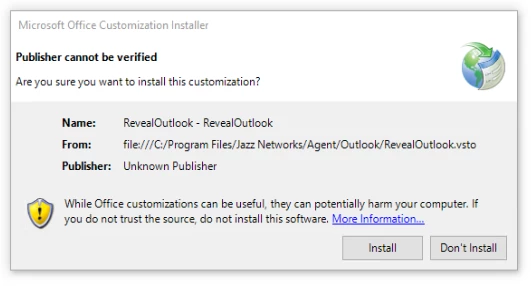
| Solution | Summary: The Windows code signing certificate for Jazz Networks Ltd. expired on the 19th of December 2021, and subsequently the Ava Security Limited certificate expired on 16th November 2024. These certificates have been used to sign all versions of the Reveal agents up to and including 12.0.0. Some warnings may now be seen in Microsoft Outlook.
Impact: Users who have previously followed the instructions to suppress the Outlook installer warning may now see unexpected pop-ups, even if they have followed the steps as described.
Other components of the Reveal Agent are unaffected.
Root Cause: The RevealOutlook plugin signature in the manifest does not contain an associated timestamp server. As such Outlook is looking at the original signing certificate only, which is now expired. Other components of the Reveal Agent are unaffected as they are correctly signed and timestamped.
Workaround: Users can manually install/approve the plugin by selecting the 'Install' option when prompted by Outlook.
Solution: Administrators should install all copies of the certificates (ava-codesign.pem, and nextdlp-codesign.pem) as a 'Trusted Publisher' via Group Policy and then upgrade to the 12.0.0 FortiDLP agent as soon as possible.
Note on the certificate(s): Ava Security / Jazz Networks are historic names of FortiDLP, so these are still our certificates. When Ava Security was acquired by Motorola Solutions in 2020, the Reveal product became a standalone business, Next DLP. Jazz Networks is an old name for Ava Security (which is why it is still referenced in places like our application path).
The codesigning certificates are provided by either DigiCert (based on a Symantec root) or SSL.com, which are both one of the four Microsoft-endorsed providers that provide an Extended Validation certificate. This is required to sign kernel modules on Windows. Extended Validation, the highest form of SSL certificate, indicates that DigiCert has conducted its extended checks.
Microsoft already trusts the certificate as demonstrated when the Agent installs the kernel drivers – Windows would prevent the kernel-signed modules from installing if this were not the case.
Outlook (and Office applications) handle this a little differently as detailed in this Microsoft support article. |
