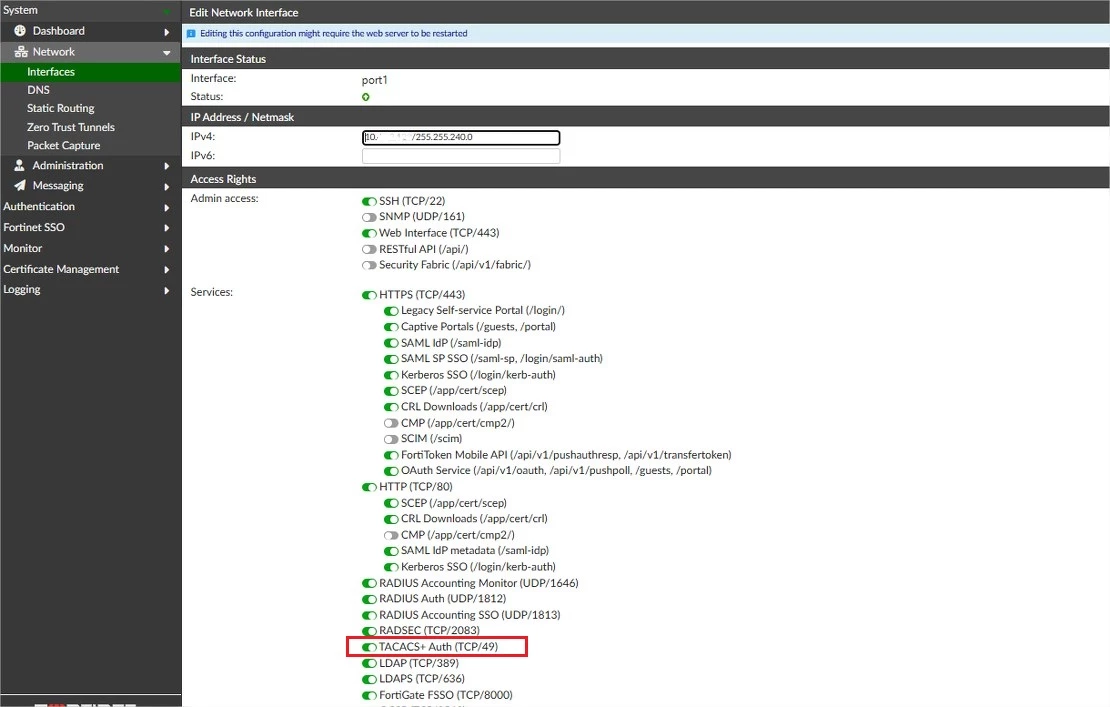
Solution | FortiDDoS-F supports three remote authentication methods for the administration account they are RADIUS, LDAP, and TACACS+. This article shows the example of creating the remote administration account in FortiAuthenticator and using the TACACS+ authentication method to authenticate the administration account login to the FortiDDoS-F device. In the FortiAuthenticator Network Interface settings, enable the TACACS+ Auth service. Save the setting, and FortiAuthenticator will reload itself.
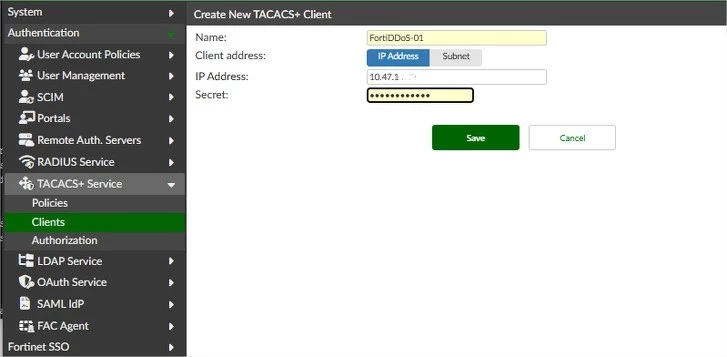
 Navigate to the TACACS+ Service -> Clients page, create a client profile for the FortiDDoS device. Insert the IP address of the FortiDDoS device that will be used to connect to the FortiAuthenticator. Create a random string for the secret key and store it in a text file for later insertion into FortiDDoS TACACS+ settings.
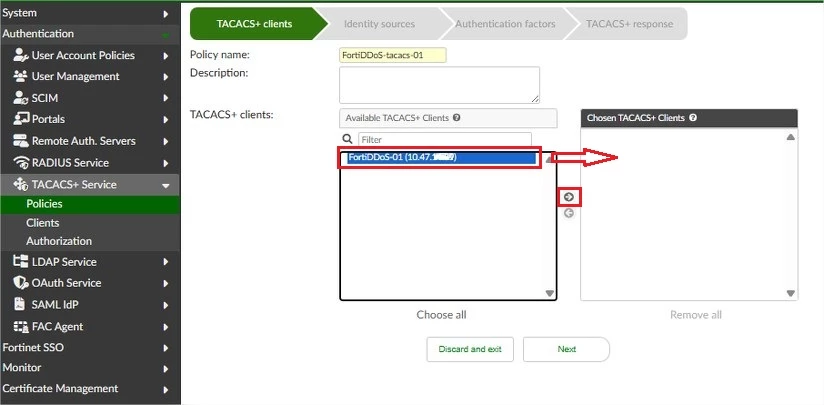
 Create a new policy in TACACS+ Service and select the FortiDDoS profile for the policy.
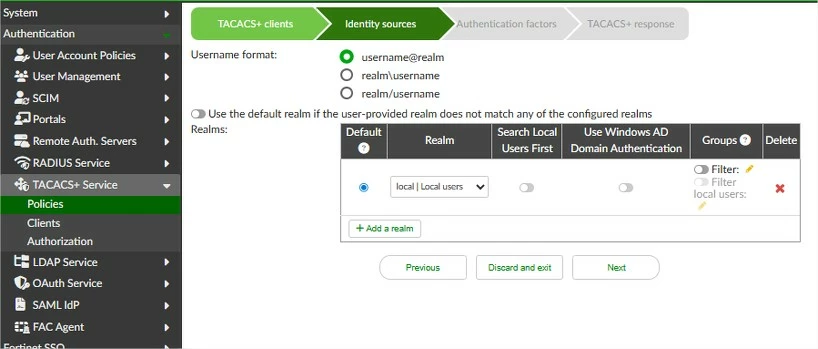
 In the same policy setting wizard, select the user group realm for the FortiDDoS authentication account group. The default local user is used in this example.
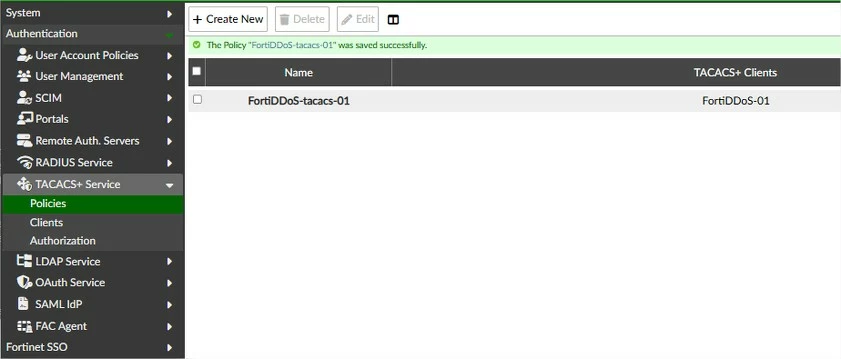
 Leave other settings as default, save, and exit the policy settings. The TACACS+ policy for FortiDDoS can be seen on the page now.
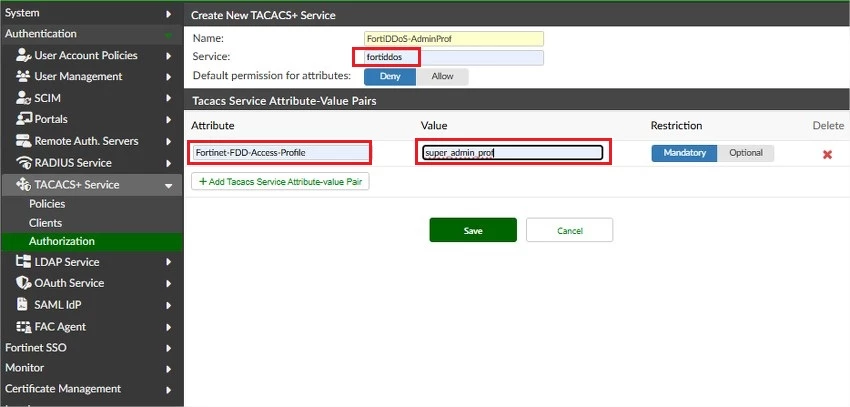
 Next, create the Authorization -> Services profile for FortiDDoS. Insert a name for the profile, and the Service text box must be 'fortiddos'; FortiDDoS would not be able to authenticate if the service name does not match. Add the TACACS+ service attribute-value pair, following the name and value below.
Attribute: Fortinet-FDD-Access-Profile. Value: super_admin_prof (can be other profile, profile name case must match the group profile created in FortiDDoS).
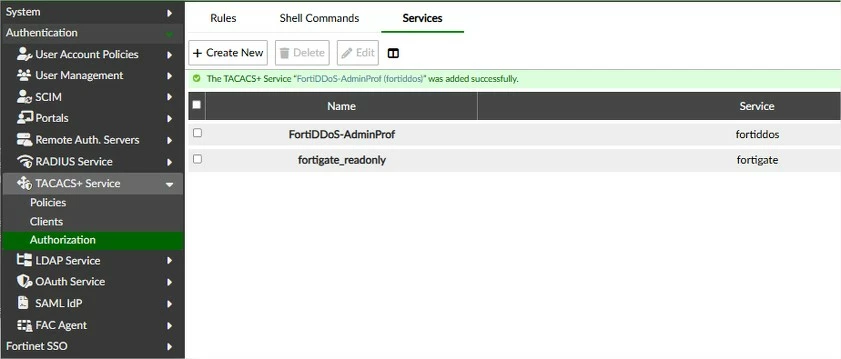
 Review the Authorization Service profile after it is created.
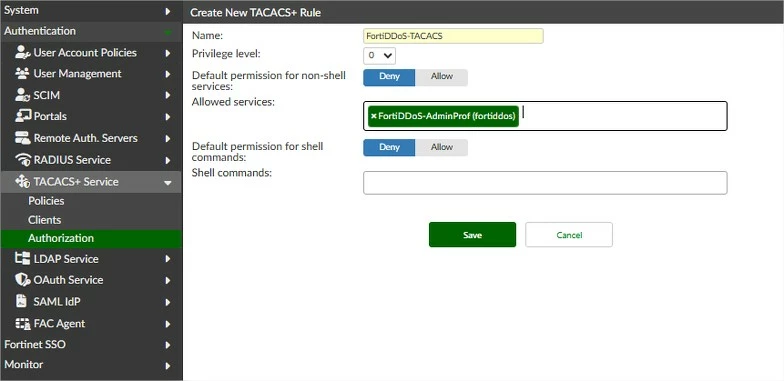
 Now navigate to the Authorization -> Rules page and create an authorization rule profile. Select the Authorization Service profile and leave other configurations as default.
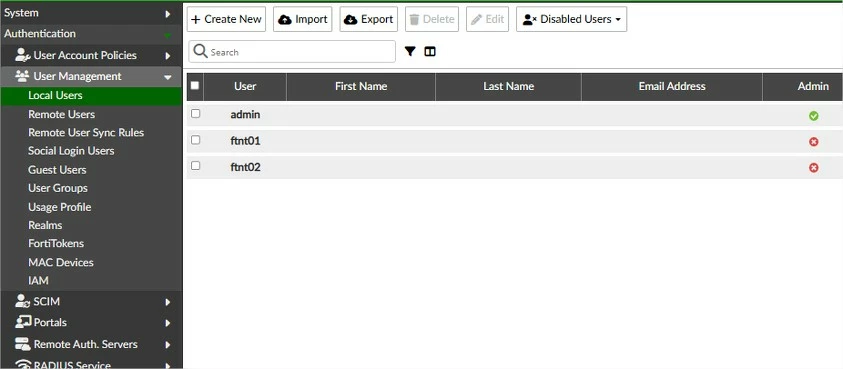
 In the local user page, create or edit the existing users to be used for the remote authentication.
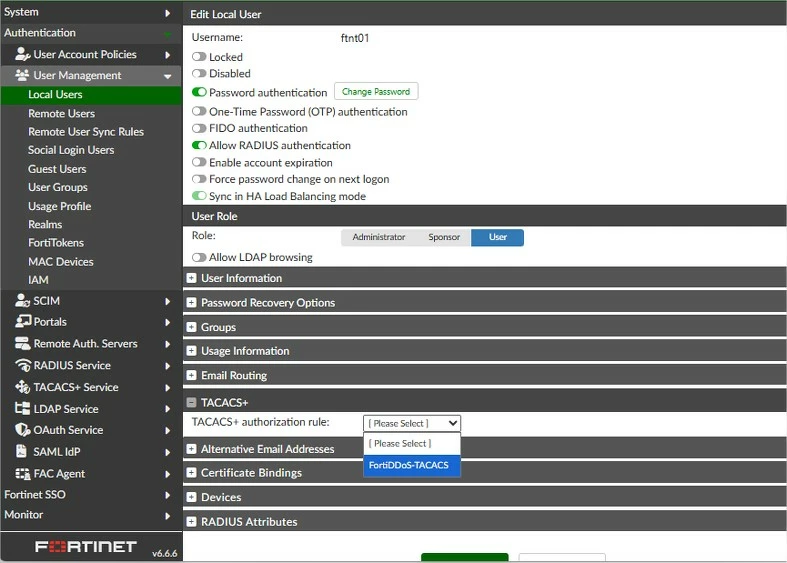
 In the user edit page, expand the TACACS+ option. Select the TACACS+ authorization rule created in step 8 from the dropdown menu. The configuration in FortiAuthenticator is now completed.
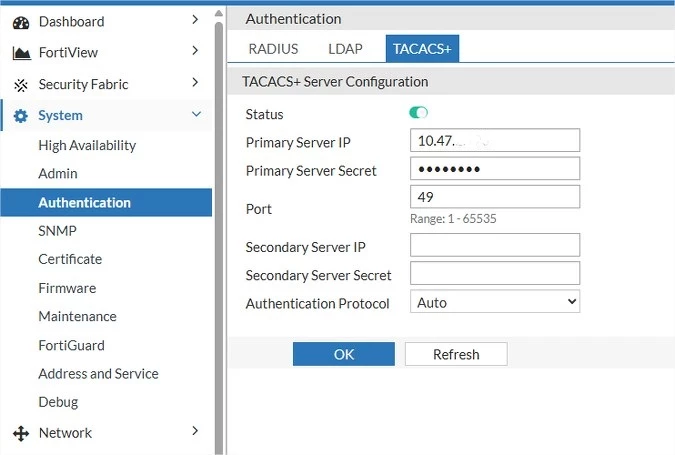
 Now log in to the FortiDDoS-F GUI using the admin account. Navigate to the System -> Authentication page and go to the TACACS+ tab. Toggle to enable the TACACS+ Server configuration. Insert the FortiAuthenticator IP and the secret key generated in step 2. Leave other settings as the default.
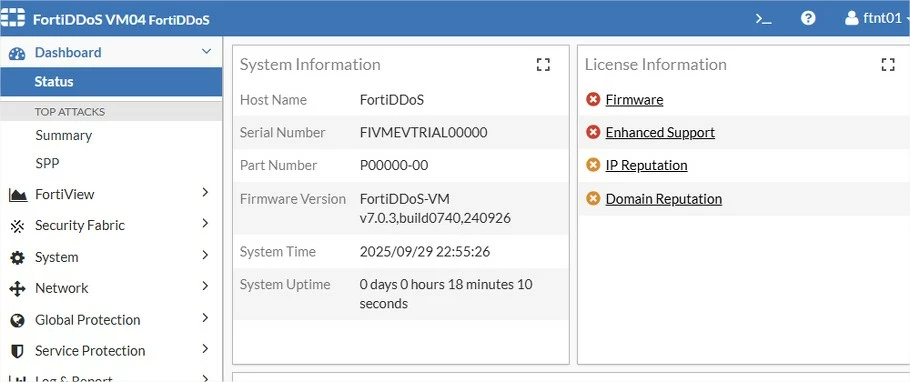
 The TACACS+ admin account login should be working now. Try to open a new browser tab in private browser or incognito mode and test the TACACS+ user login.
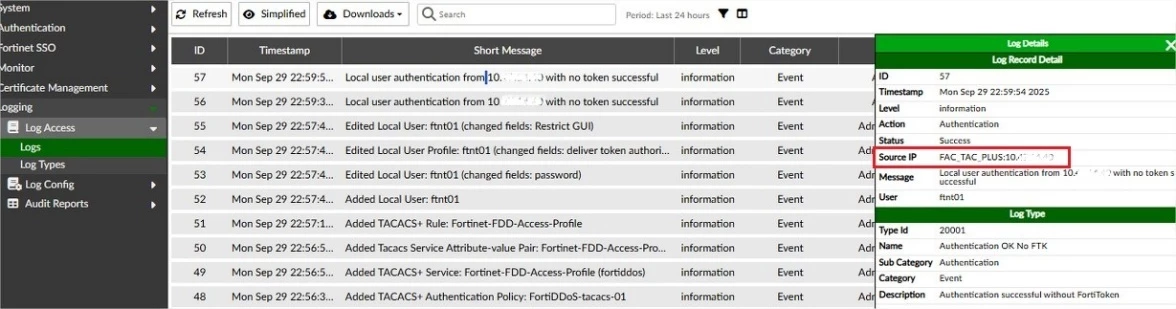
 Check the FortiAuthenticator logs to verify the user logon.
 Note: CLI access is not supported via TACACS+ authentication.
Related document:
Configuring TACACS+ authentication |





