FortiCNAPP Code Security feature supports IaC-only CI/CD integrations with Jenkins. The CI/CD IaC scan result should be uploaded from Jenkins during the pipeline build to the FortiCNAPP infra, so it will then be populated and displayed in the Code Security IaC dashboard page.
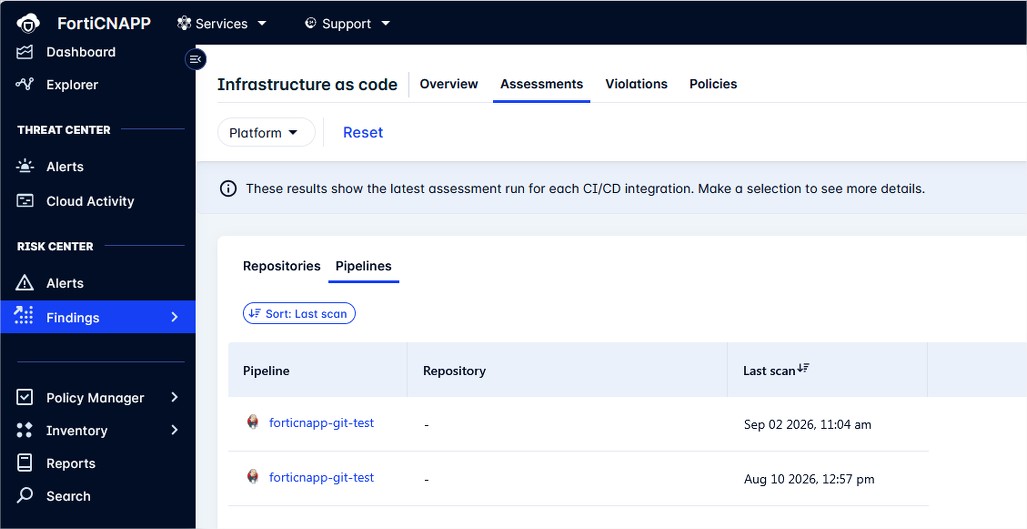
If the scan result does not appear in the dashboard, follow the steps to troubleshoot the possible reasons the IaC scan result is not populated in FortiCNAPP.
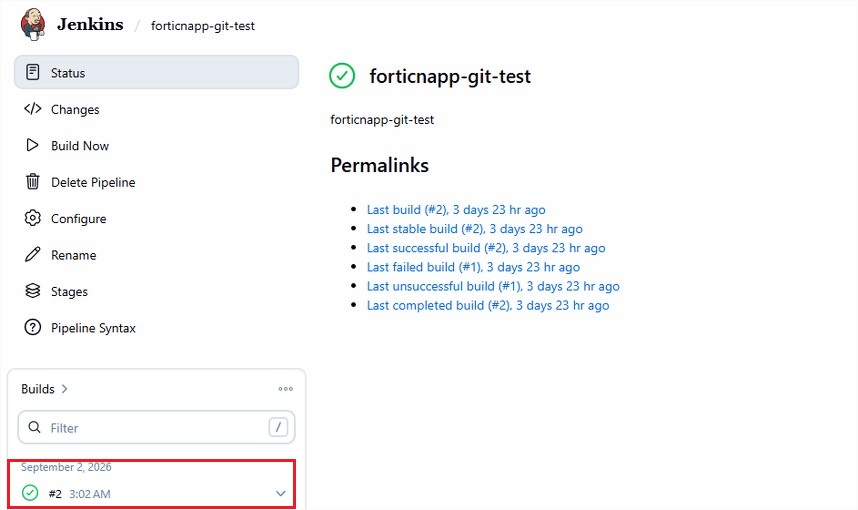
Check if the pipeline build runs successfully.
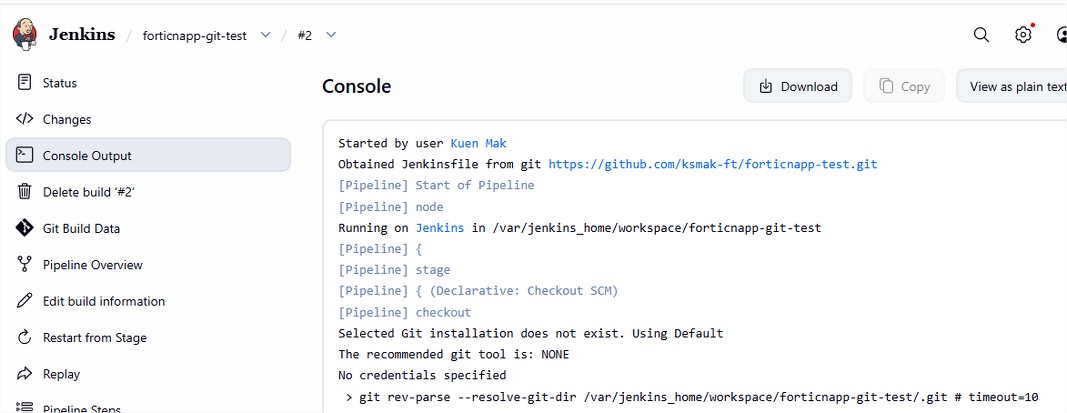
Check the pipeline console output log to check the IaC pipeline build log and the FortiCNAPP IaC scan task.
Export the log if necessary.
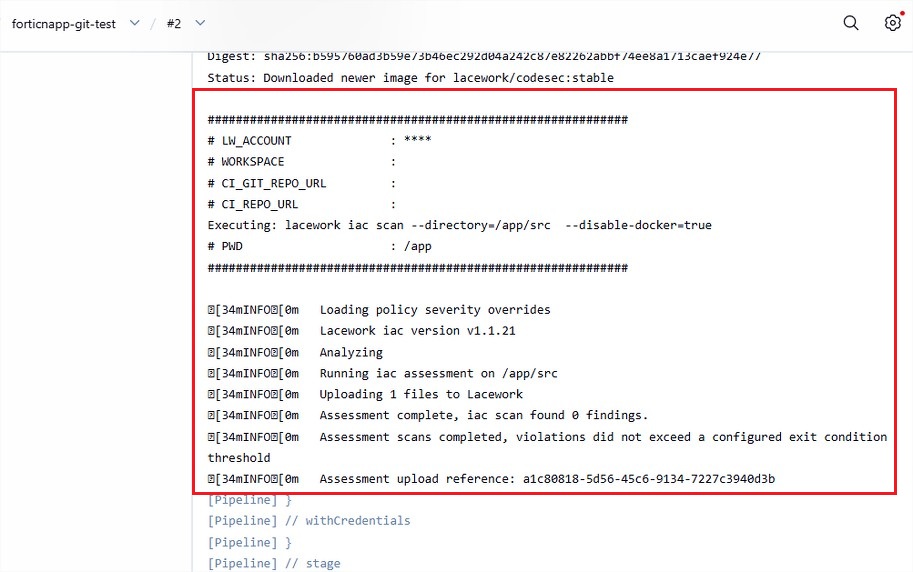
The FortiCNAPP IaC scan uses docker image lacework/codesec to scan the code.
Go through the pipeline console output log and make sure that the docker image runs successfully.
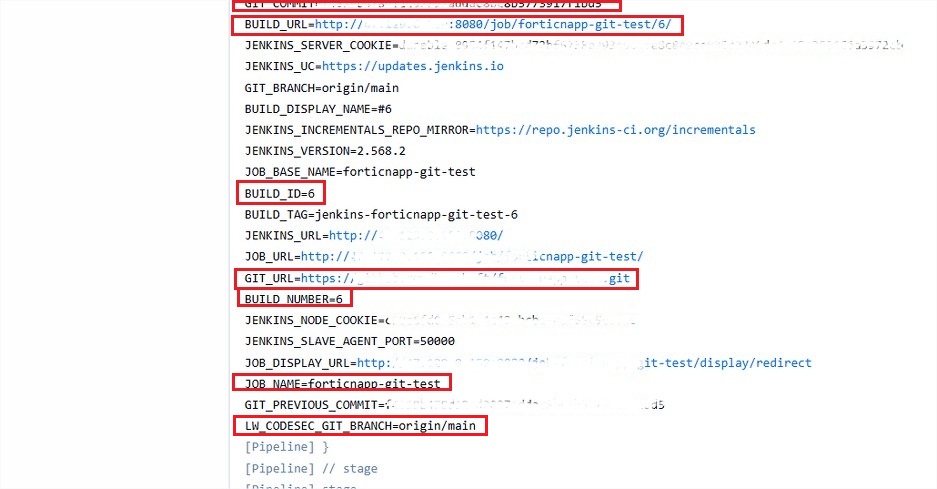
Make sure that the pipeline configuration includes all the environment variables required by FortiCNAPP to populate the uploaded IaC scan data to the dashboard.
export JENKINS_URL='${JENKINS_URL}' \
         BUILD_URL='${BUILD_URL}' \
         BUILD_ID='${BUILD_ID}' \
         BUILD_NUMBER='${BUILD_NUMBER}' \
         JOB_NAME='${JOB_NAME}' \
         GIT_URL='${GIT_URL}' \
         GIT_COMMIT='${GIT_COMMIT}' \
         LW_CODESEC_GIT_BRANCH='${GIT_BRANCH:-main}';
Related document: Jenkins | 




