Scope | FortiCNAPP, Visual Studio Code.
This article is aimed towards FortiCNAPP Code Security users who want to use the Visual Studio Code extension for Software Composition Analysis (SCA), Static Application Security Testing (SAST), and Infrastructure as Code (IaC) scanning in a local development environment. |
Solution | Running scans and results:
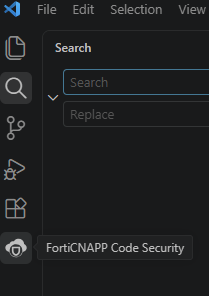
Open the project workspace in Visual Studio Code, and select FortiCNAPP extension icon.
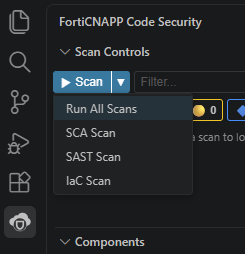
Start all scans via the Scan button, or run scan independently (IaC, SAST, or SCA or Run all scans).
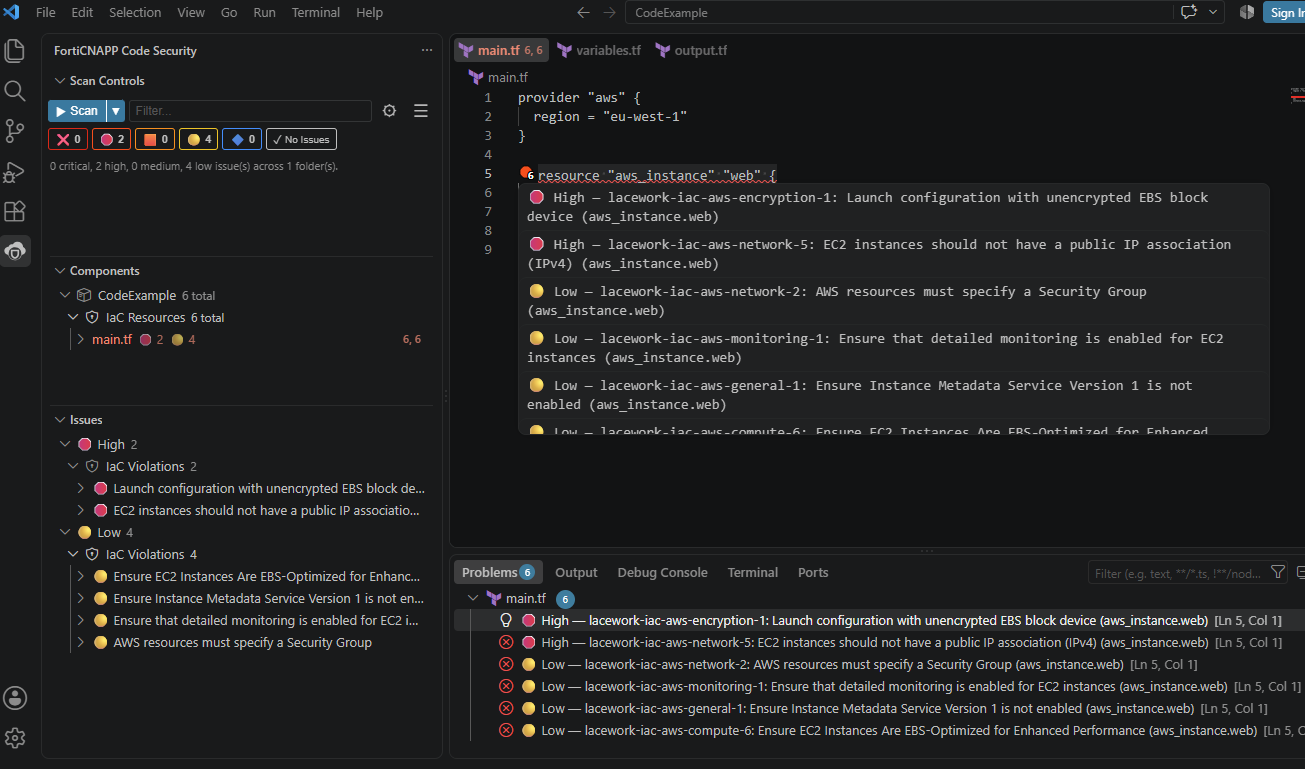
Review results in the Problem View, and navigate to files by using the Issues tree view that allows opening related files.
Troubleshooting:
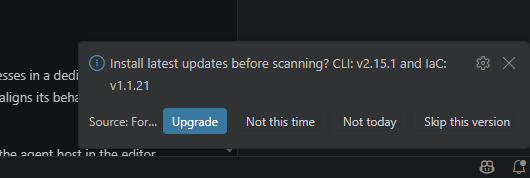
It is still possible to run the scans without upgrading to the latest updates, but scans will not benefit from the latest release features.
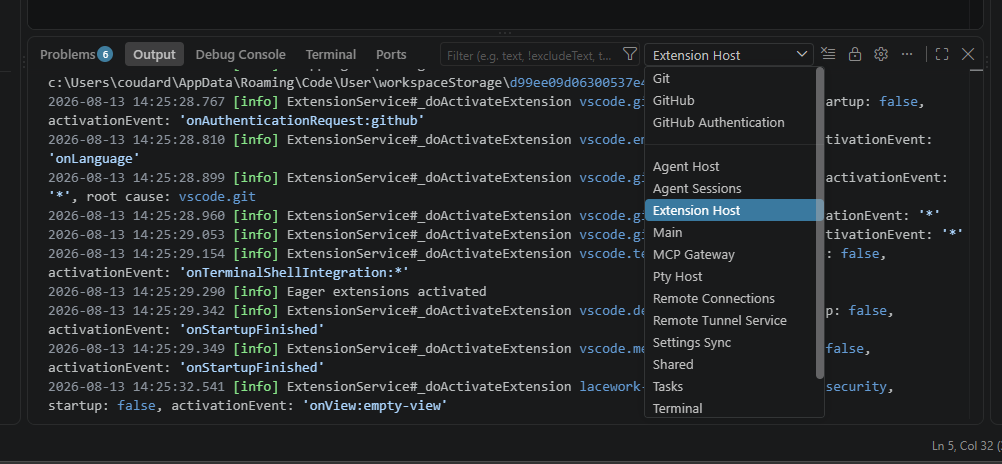
If an error occurs while running scans, extract the extension logs: go the Output panel: In Visual Studio Code, go to View -> Output -> Select 'Extension Host' from the drop-down. Then use the 'save output as' or 'export Logs' option to get full logs.
If any issue occurs while scanning, verify this independently in the FortiCNAPP CLI. The following is an example for an SCA scan that saves output in FortiCNAPP the JSON format, and saves the file for investigation.
lacework sca scan <directory> -f lw-json -o <output location and filename>
Related document:
For instructions on how to install the extension, see VS Code in the documentation.
|




