| Solution | Prerequisites: - FortiAnalyzer running version 7.6.3 or later.
- Network connectivity from FortiCNAPP to FortiAnalyzer on the FEC listening port (default: 8443).
- A trusted TLS certificate on FortiAnalyzer.
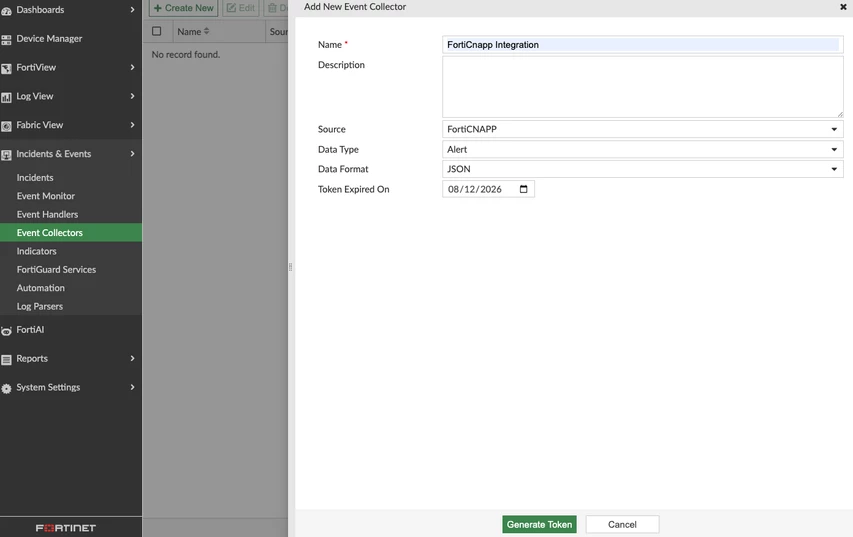
Integration steps: Step 1: On FortiAnalyzer. - Create an event collector under Incidents & Events -> Event Collectors -> Create new.
- Select source : FortiCNAPP, Data type : Alert or log, Data Format : JSON.
- Select Generate Token (by default the token expiry is set to 6 months).
- Save the Access token since it is visible only when generated.
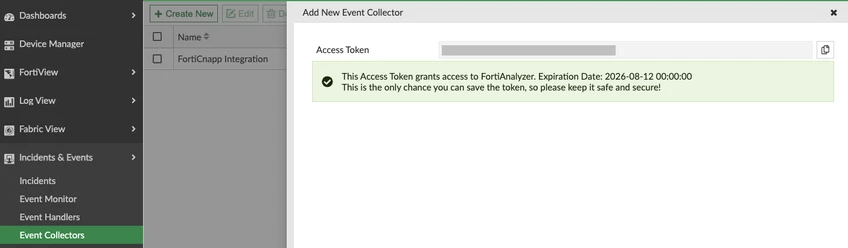
- The Regenerate Token option can be used to regenerate a token when required for the event collector. The regenerated token must also be updated in the FortiCNAPP webhook.
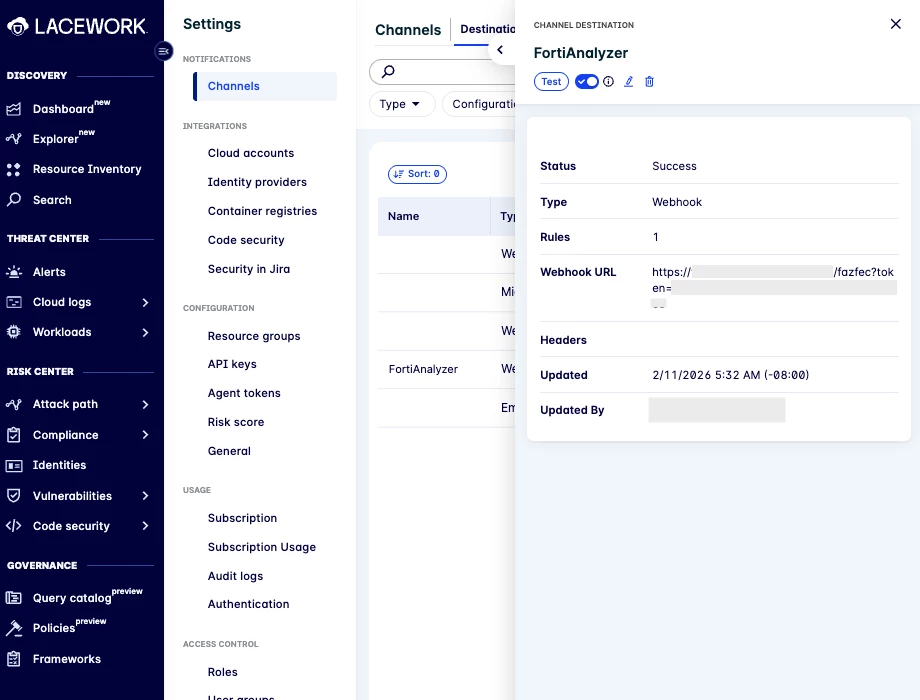
 Step 2: On FortiCNAPP. - In the UI, navigate to Settings -> Channels -> Destinations.
- Select Add to create a new destination.
- Set the Webhook URL to the following:
https://<fortianalyzer-fqdn>/fazfec?token=<token> In the above: - <fortianalyzer-fqdn> - FortiAnalyzer hostname or IP address.
- <token> - The access token generated in Step 1.
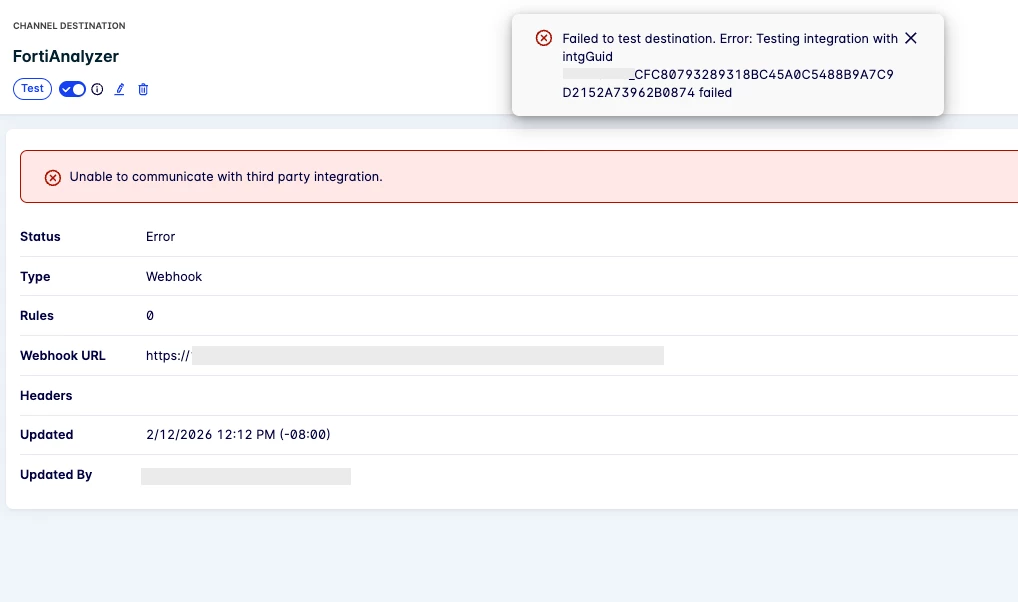
Save and test. 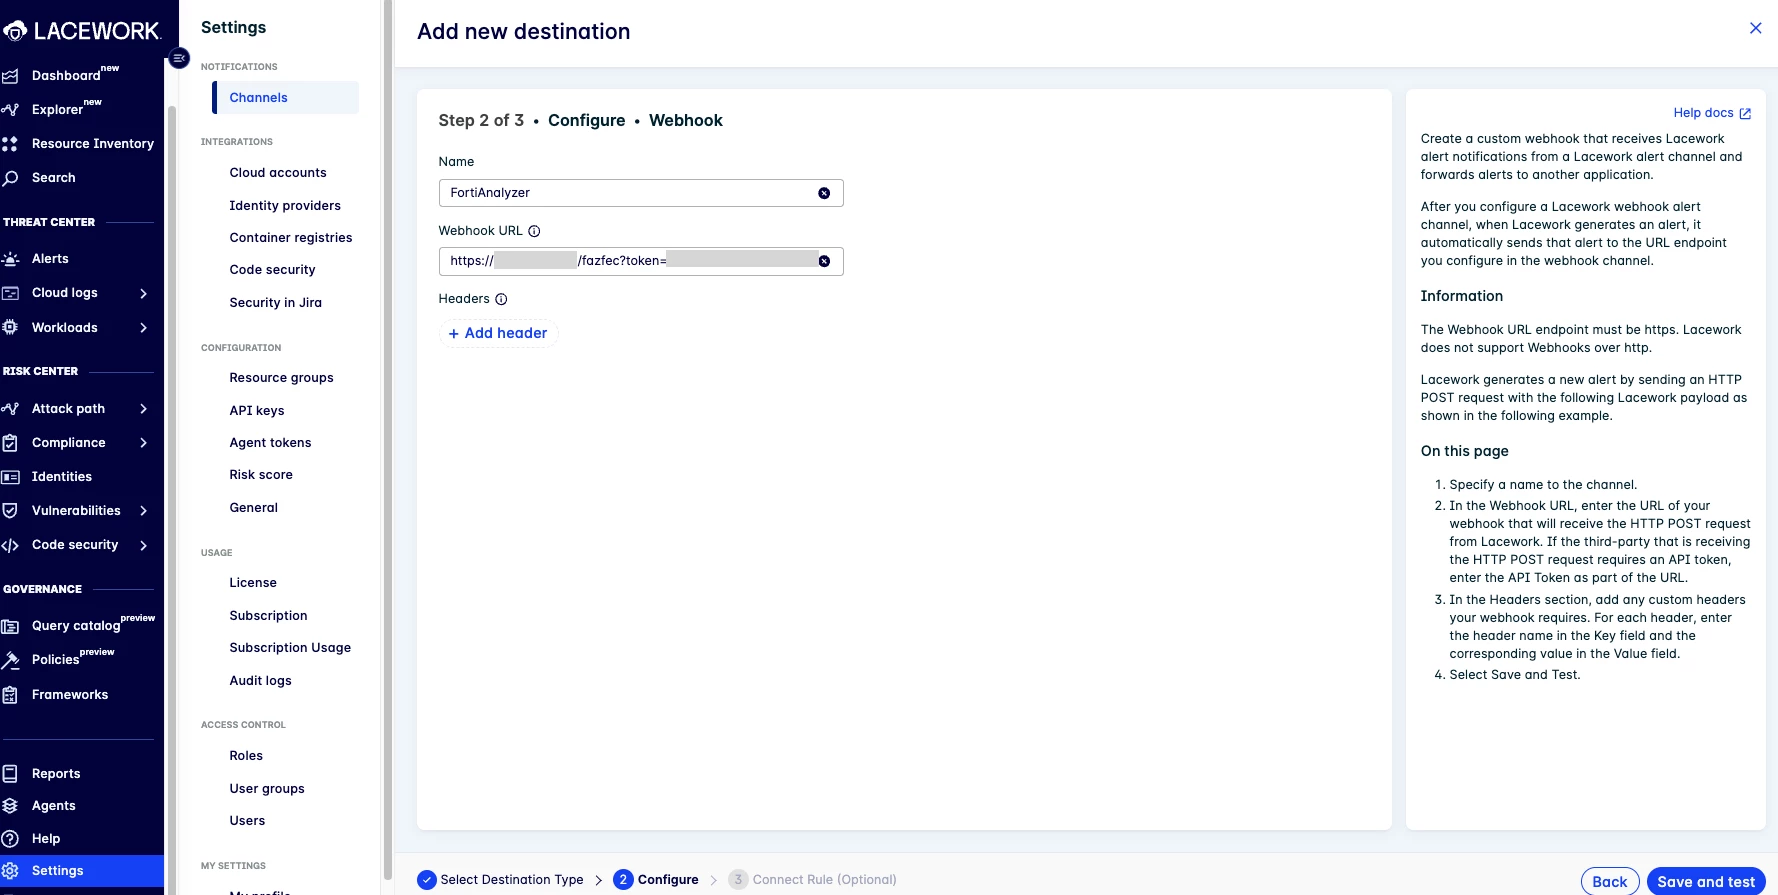 Result:The integration is successful. Troubleshooting: - Sometimes, the connection may fail with the following error in the UI:
"Unable to communicate with third party integration" Failed to test destination. Error: Testing integration with intgGuid xxxxx_xxxxxxxxxx failed
Backend log: javax.net.ssl.SSLHandshakeException: PKIX path building failed: sun.security.provider.certpath.SunCertPathBuilderException: unable to find valid certification path to requested target
- This issue is typically caused by an invalid or incomplete SSL certificate chain on the destination server.
- Make sure the certificate has a valid path. Use a certificate from a publicly trusted CA such as Let's Encrypt.
- If organizational policy requires an internal CA, ensure:FortiAnalyzer has the complete certificate chain.
- Once the certificate has a been validated, test the integration again.
|