



Troubleshooting Tip: Vulnerability scan runs daily despite the FortiClient EMS Schedule
Description | This article describes why the vulnerability scan still runs daily despite the scheduled time defined in the Endpoint profile configuration. |
Scope | FortiClient, Vulnerability Scan, FortiClient EMS. |
Solution | If a specific time is configured in the endpoint vulnerability scan profile schedule, but the scan still runs daily or outside the defined schedule, review the following settings to identify the cause.
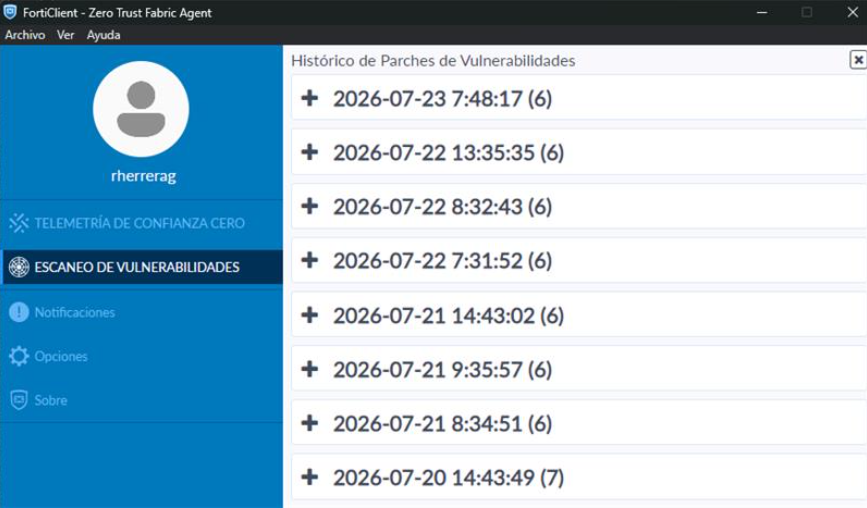
In FortiClient EMS, navigate to the following Endpoint profiles -> Vulnerability Scan, and under the scanning section, ensure the following options are disabled or unchecked:
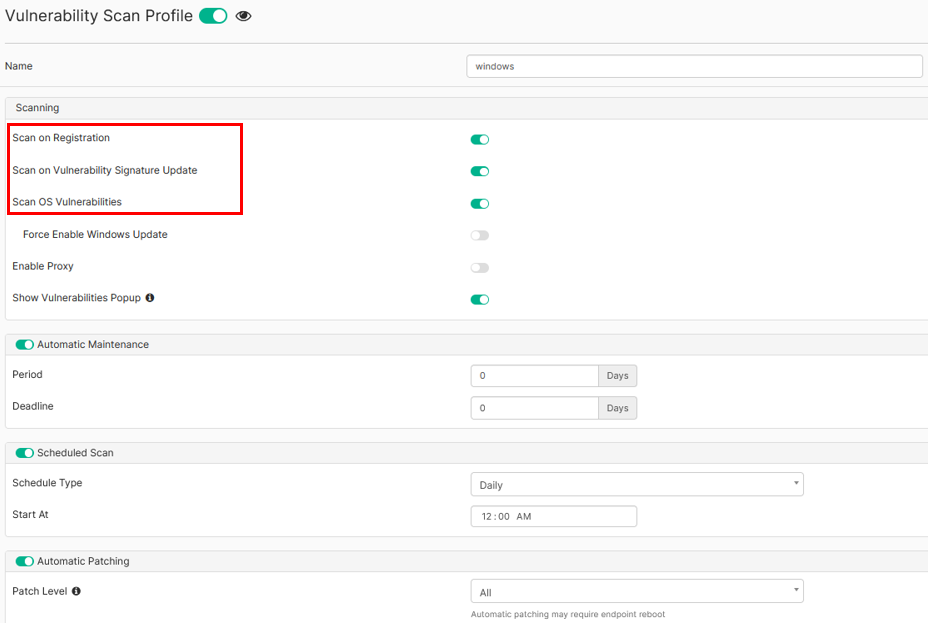
Another common cause of repeated scans is the Scan on Registration option or <scan_on_fgt_registration> as defined in the XML configuration. If enabled, FortiClient runs a Vulnerability Scan every time the endpoint registers or reconnects to a FortiGate or EMS. If the endpoint restarts, re-authenticates, or experiences network changes, this can happen multiple times daily.
The last cause of repeated scans is the Scan OS Vulnerabilities option or <windows_update> as defined in the XML configuration. With that option enabled, FortiClient actively monitors Windows Update status. When patches are installed or detected, the system may trigger additional checks to ensure OS vulnerability compliance. These are not directly controlled by the schedule and often run after Windows Update cycles.
These frequent updates ensure endpoints are checked for the latest known security issues, but they can cause scans to run much more often than the single scheduled time defined in the FortiClient EMS profile.
Related documents: |

