| In a working scenario, for both SSL VPN and IPsec VPN, after the VPN is connected, the default route metric of the VPN adapter should always be lower than the local network adapter. Issue symptoms: - After connecting to the VPN, end users will lose Internet connectivity and can only access internal resources.
- Comparing the 'route print' command result, noticed that the VPN default route metric is the same as the LAN adapter; by right, it should always be lower than the LAN adapter.
Issue example: Before connecting to VPN:
IPv4 Route Table
===========================================================================
Active Routes:
Network Destination Netmask Gateway Interface Metric
0.0.0.0 0.0.0.0 192.168.10.1 192.168.10.11 25 <--- Local LAN adapter default route metric.
127.0.0.0 255.0.0.0 On-link 127.0.0.1 331
127.0.0.1 255.255.255.255 On-link 127.0.0.1 331
127.255.255.255 255.255.255.255 On-link 127.0.0.1 331
192.168.10.0 255.255.255.0 On-link 192.168.10.11 281
192.168.10.11 255.255.255.255 On-link 192.168.10.11 281
192.168.10.255 255.255.255.255 On-link 192.168.10.11 281
224.0.0.0 240.0.0.0 On-link 127.0.0.1 331
224.0.0.0 240.0.0.0 On-link 192.168.10.11 281
After connecting to the VPN:
IPv4 Route Table
===========================================================================
Active Routes:
Network Destination Netmask Gateway Interface Metric
0.0.0.0 0.0.0.0 192.168.10.1 192.168.10.11 25 <--- Local LAN adapter default route metric.
96.45.44.64 255.255.255.255 192.168.10.1 192.168.10.11 25 <--- VPN adapter default route is the same as LAN adapter (abnormal).
127.0.0.0 255.0.0.0 On-link 127.0.0.1 331
127.0.0.1 255.255.255.255 On-link 127.0.0.1 331
127.255.255.255 255.255.255.255 On-link 127.0.0.1 331
192.168.10.0 255.255.255.0 On-link 192.168.10.11 281
192.168.10.11 255.255.255.255 On-link 192.168.10.11 281
192.168.10.255 255.255.255.255 On-link 192.168.10.11 281
224.0.0.0 240.0.0.0 On-link 127.0.0.1 331
224.0.0.0 240.0.0.0 On-link 192.168.10.11 281
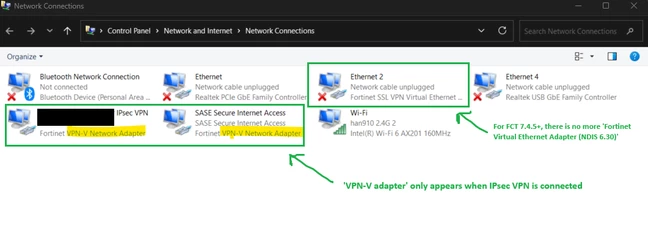
Solution: - Go to Start -> type: ncpa.cpl -> Enter.
- Check if there is more than one 'Fortinet SSL VPN Virtual Ethernet adapter' and 'Fortinet Virtual Ethernet Adapter (NDIS 6.30)'.
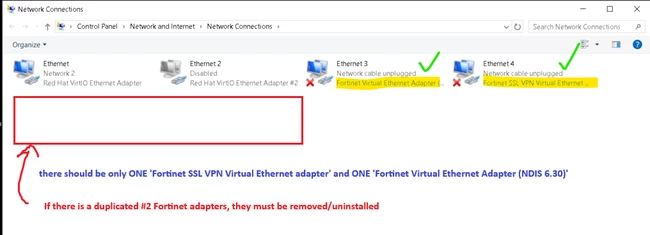 - If there is duplicated of adapters, they must be removed.
- Go to Start -> Device Manager.
- Under 'Network Adapters', locate the redundant adapters -> 'Right click' -> Uninstall Driver.
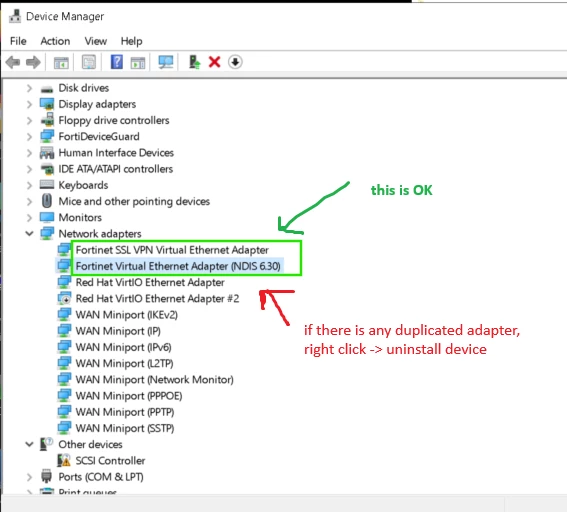
- Go back to ncpa.cpl, ensure that the redundant adapters are removed.
Note: In case the redundant adapters are unable to be removed for any reason, proceed to uninstall the existing FortiClient in Control Panel -> Reboot PC -> Fresh install FortiClient. To verify the solution: - Disconnect VPN.
- Re-connect VPN.
- Check the 'route print' command result:
IPv4 Route Table
===========================================================================
Active Routes:
Network Destination Netmask Gateway Interface Metric
0.0.0.0 0.0.0.0 10.111.36.1 10.111.36.22 25 <--- Local LAN adapter default route metric.
0.0.0.0 0.0.0.0 100.65.48.55 100.65.48.54 9 <--- VPN adapter default route now has a lower metric than LAN adapter (OK).
10.111.36.0 255.255.255.0 On-link 10.111.36.22 281
10.111.36.22 255.255.255.255 On-link 10.111.36.22 281
10.111.36.255 255.255.255.255 On-link 10.111.36.22 281
96.45.38.142 255.255.255.255 10.111.36.1 10.111.36.22 26
100.65.48.54 255.255.255.255 On-link 100.65.48.54 260
127.0.0.0 255.0.0.0 On-link 127.0.0.1 331
127.0.0.1 255.255.255.255 On-link 127.0.0.1 331
127.255.255.255 255.255.255.255 On-link 127.0.0.1 331
224.0.0.0 240.0.0.0 On-link 127.0.0.1 331
224.0.0.0 240.0.0.0 On-link 10.111.36.22 281
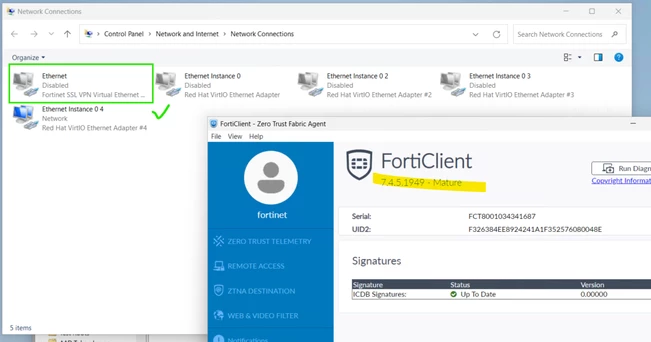
Note: For FortiClient v7.4.5 and above, there will be only one 'Fortinet SSL VPN Virtual Ethernet adapter'; 'Fortinet Virtual Ethernet Adapter (NDIS 6.30)' is no longer used from FortiClient v7.4.5 onwards.
|