| Solution | Under the FortiClient EMS endpoint pane, the EMS administrator can remotely instruct the endpoint FortiClient to perform the below scanning option: - Vulnerability Scan.
- Quick AV Scan.
- Full AV Scan.
Sometimes certain scan options are not available. If the scan option is not available, check the associated profile whether the feature module has been enabled. Example 1: The vulnerability Scan option is missing.
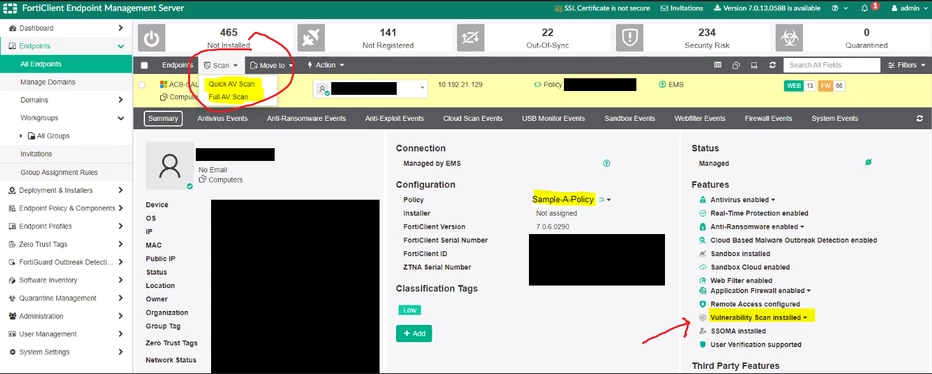
- On the right side, check if the Vulnerability Scan module is installed. As per the above screenshot, the Vulnerability Scan module is installed, but it is not enabled in the endpoint profile (grey icon = feature disabled, green icon = feature enabled).
- In this example, this endpoint is using 'Sample-A-Policy'.
- Go to EMS -> Endpoint Policy & Components -> expand the 'Sample-A-Policy', and check which Vulnerability Scan profile it is currently using.
- Go to EMS -> Endpoint Profiles -> Vulnerability Scan -> (select the profile) -> Edit -> Turn on Vulnerability Scan -> Save the profile.
- Wait for the endpoint to sync the profile. Afterwards, the Vulnerability Scan option would be available for this endpoint.
Example 2: The Antivirus scan option is missing. 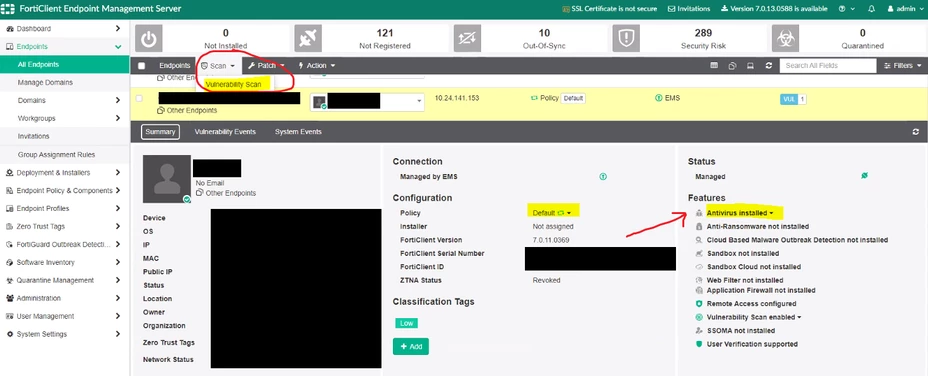
- On the right side, check if the Antivirus module is installed. As per the above screenshot, the Antivirus module is installed, but it is not enabled in the endpoint profile (grey icon = feature disabled, green icon = feature enabled)
- In this example, this endpoint is using the 'Default' policy.
- Go to EMS -> Endpoint Policy & Components -> expand the 'Default' policy, check which Malware Protection profile it is currently using.
- Go to EMS -> Endpoint Profiles -> Malware Protection -> (select Default profile) -> Edit -> Turn on Malware Protection -> Save the profile.
- Wait for the endpoint to sync the profile. Afterwards, an Antivirus scan option would be available for this endpoint.
|