Technical Tip: Importing web filter profiles from FortiGate to FortiClient EMS
| Description | This article outlines how to import the default and custom categories from FortiGate to FortiClient EMS. |
| Scope | FortiClient EMS and FortiGate. |
| Solution | FortiGate requirements:
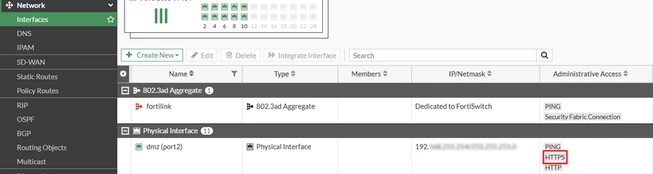
Important: HTTPS access must be permitted by FortiGate to effectively import Web Filter profiles from FortiOS to FortiClient EMS.
In FortiGate:
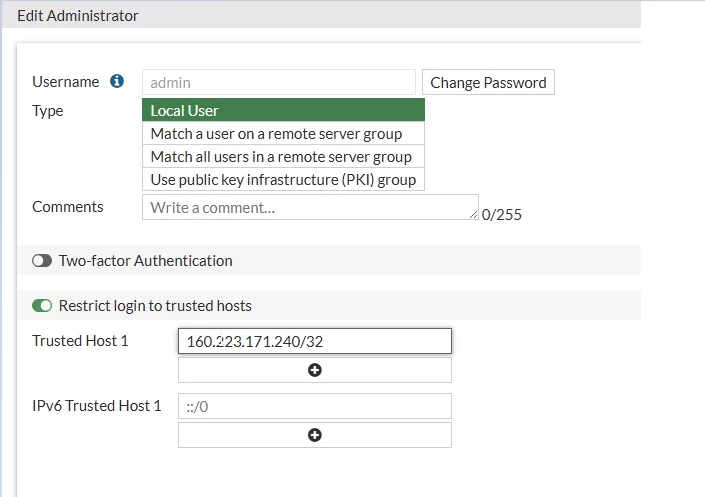
If the admin account that will be used for the import is configured with a trusted host, add the IP from where the connection attempt will originate. If using EMS Cloud, add the Cloud IP: FortiClient Cloud Portal > -About.
Related document: Allowlisting the FortiClient Cloud IP addresses
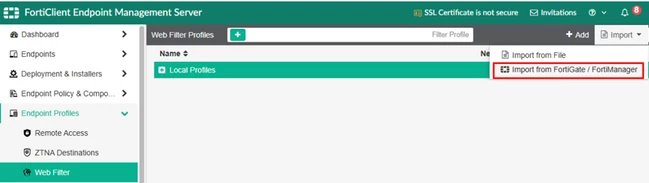
Importing Web Filter Profile: Steps to Import a Web Filter Profile from FortiGate to EMS:
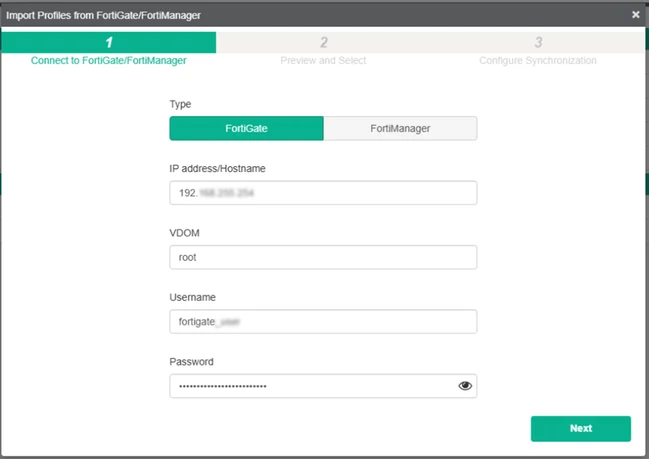
In the screen that appears, fill out the following fields:
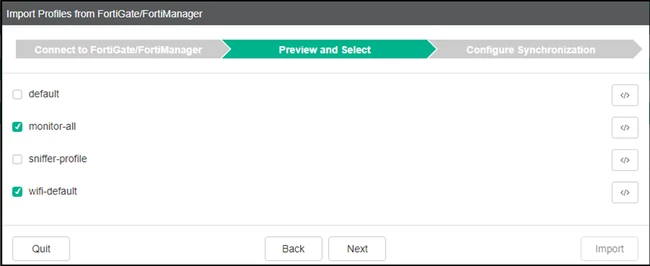
The FortiGate's configured Web Filter profiles will be listed.
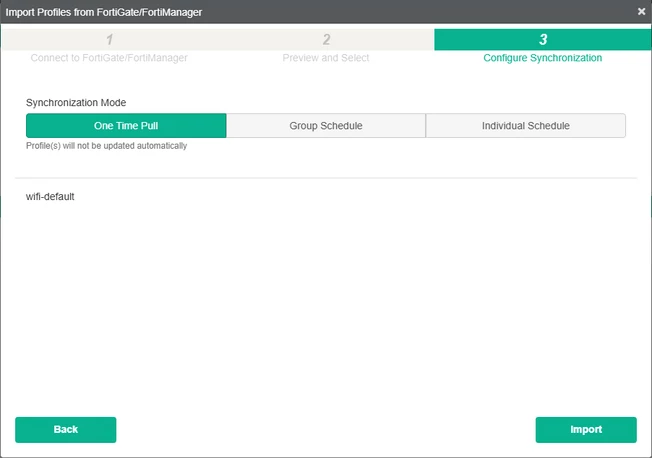
Select the Synchronization Mode and select Import:
The chosen profiles will be imported by EMS and shown in a group called FortiGate named after the source under Endpoint Profiles -> Manage Profiles.
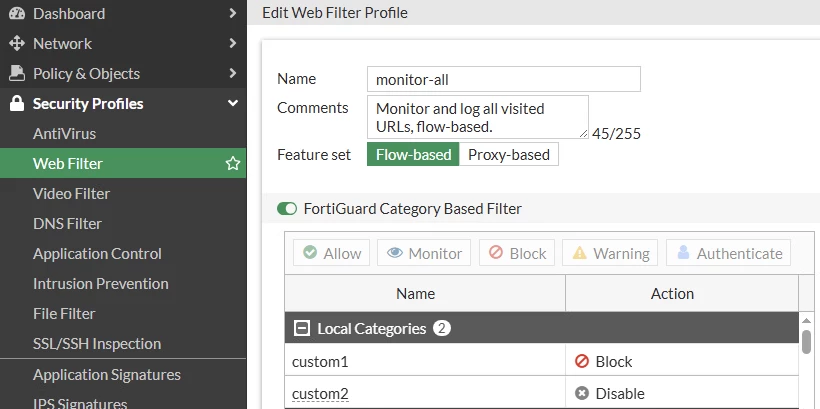
Checking custom category import.
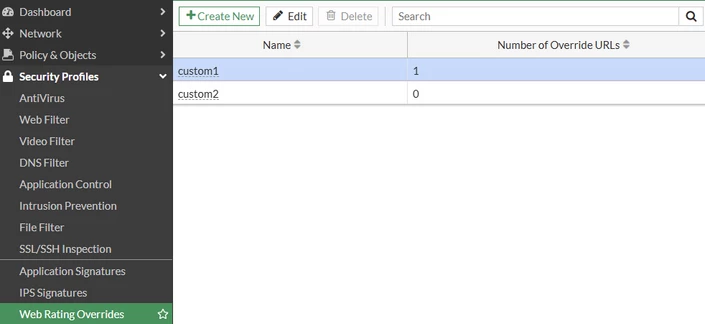
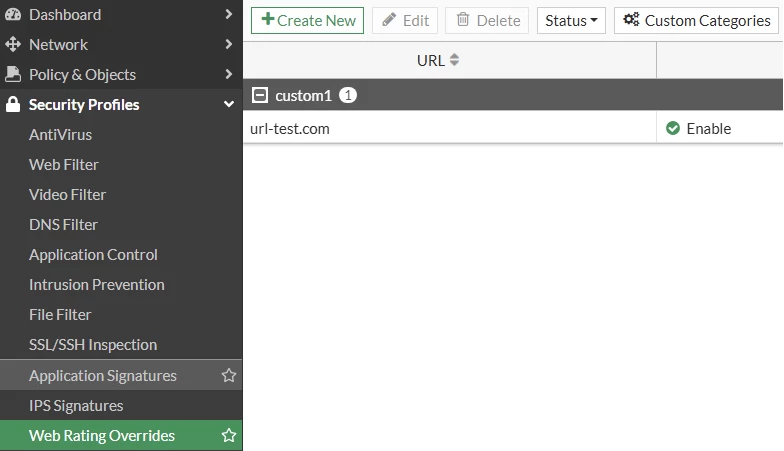
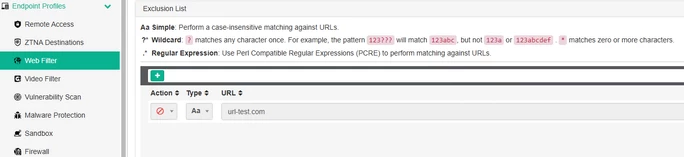
Additionally, custom categories are imported. The URLs added to each custom category, however, will be displayed in the exclusion list with the same configured action rather than in the category list. This is demonstrated in the following example:
Note that the same URL was imported with the deny action, as originally configured in the FortiGate.
Note: Starting with FortiOS 7.6.4, importing web filter profiles into FortiClient EMS using FortiGate GUI administrator credentials is no longer supported. To address this, FortiClient EMS 7.4.6 and later introduce a new method that uses a REST API key for secure integration. To successfully import web filter profiles, EMS must be running version 7.4.6 or later, and a REST API administrator account must be configured on the FortiGate.
Steps:
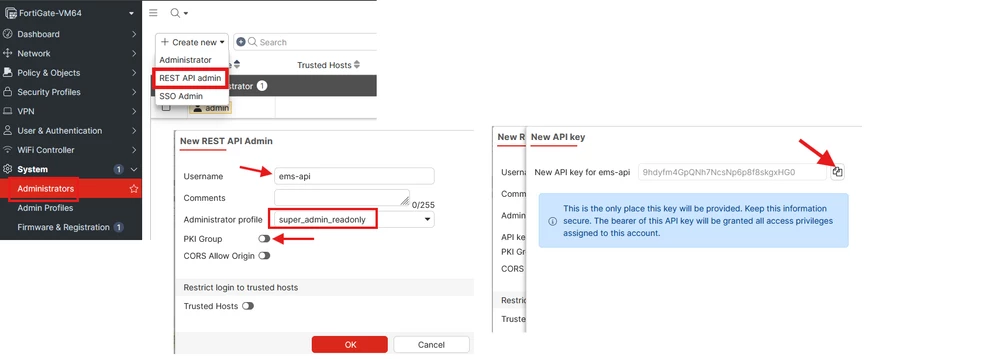
1) Navigate to System -> Administrators -> Create New -> REST API Admin -> enter the Username -> select super_admin_readonly for Administrator Profile -> unselect PKI Group -> copy the new API Key somewhere safe.
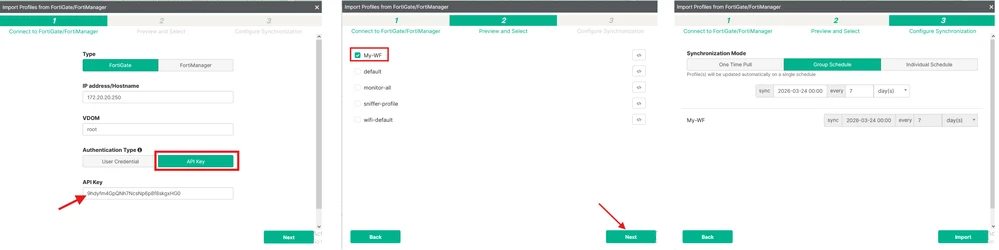
2) EMS GUI -> Endpoint Profiles -> Web filter -> Import -> import from FortiGate / FortiManager ->enter IP address of FortiGate -> select API Key for Authentication Type ->paste the API Key copied from the previous step.
Related articles: Technical Tip: How to create a REST API Admin user and assign it to an admin profile FortiClient 7.4.5 EMS Release Notes
|