



Technical Tip: How to configure IPsec dialup VPN with certificate based authentication
Description
This article explains how to configure the IPsec dial-up VPN with certificate-based authentication.
Scope
FortiClient.
Solution
Requirements:
- CA certificate.
- Server certificate.
- Client certificate.
- Generate CA Certificate ca.crt:
openssl genrsa -des3 -out ca.key 4096
openssl req -new -x509 -days 365 -key ca.key -out ca.crt
openssl req -new -x509 -days 365 -key ca.key -out ca.crt
- Generate Server Certificate server.crt:
openssl genrsa -des3 -out server.key 4096
openssl req -new -key server.key -out server.csr
openssl x509 -req -days 365 -in server.csr -CA ca.crt -CAkey ca.key -set_serial 01 -out server.crt
openssl req -new -key server.key -out server.csr
openssl x509 -req -days 365 -in server.csr -CA ca.crt -CAkey ca.key -set_serial 01 -out server.crt
- Generate Client Certificate client.crt and convert to .p12 format for exporting with private keys:
openssl genrsa -des3 -out client.key 4096
openssl req -new -key client.key -out client.csr
openssl x509 -req -days 365 -in client.csr -CA ca.crt -CAkey ca.key -set_serial 01 -out client.crt
openssl pkcs12 -export -in client.crt -inkey client.key -certfile ca.crt -name "test" -out client.p12
openssl req -new -key client.key -out client.csr
openssl x509 -req -days 365 -in client.csr -CA ca.crt -CAkey ca.key -set_serial 01 -out client.crt
openssl pkcs12 -export -in client.crt -inkey client.key -certfile ca.crt -name "test" -out client.p12
- FortiGate and FortiClient Configuration:
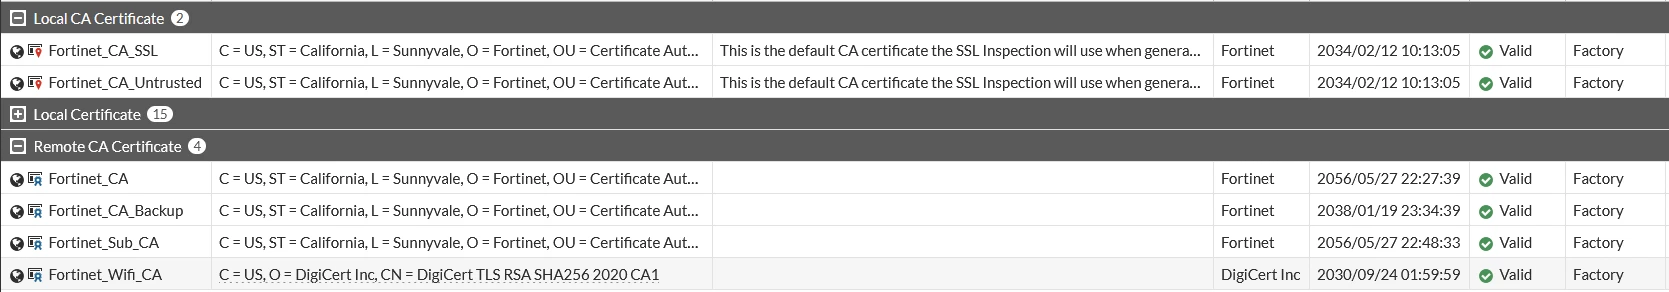
- Import CA and Server certificates on FortiGate.
- Configure the user peer and the peer user group.
config user peer
edit user1
set ca CA_Cert_2
end
config user peergrp
edit user_group1
set member user1
end
edit user1
set ca CA_Cert_2
end
config user peergrp
edit user_group1
set member user1
end
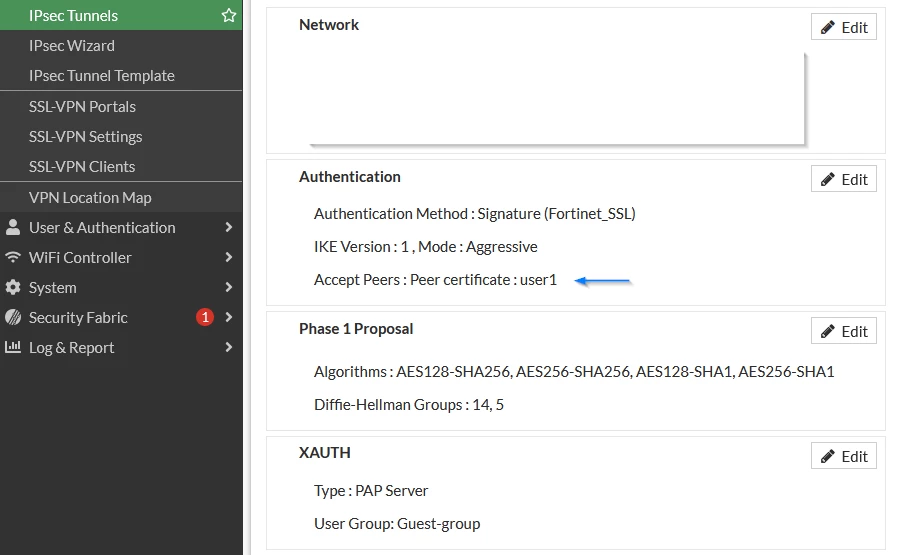
- FortiGate IPsec config.
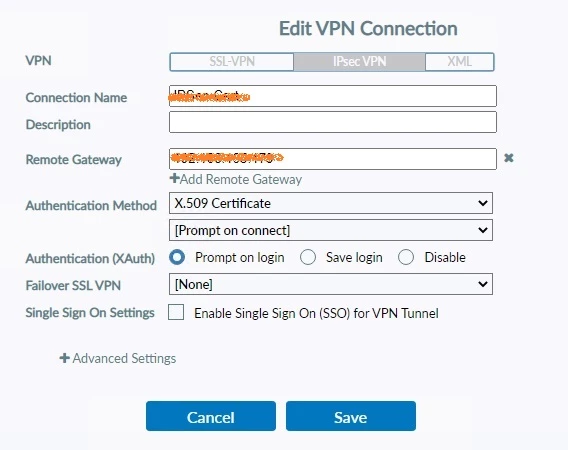
- FortiClient config: The CA certificate must be imported and placed in the Trusted Root Certification Authorities. Select Authentication Method in the IPsec VPN connection settings.
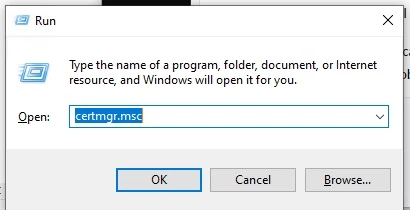
To upload a user certificate on a Windows end-device, open Run window, type certmgr.msc and press enter:
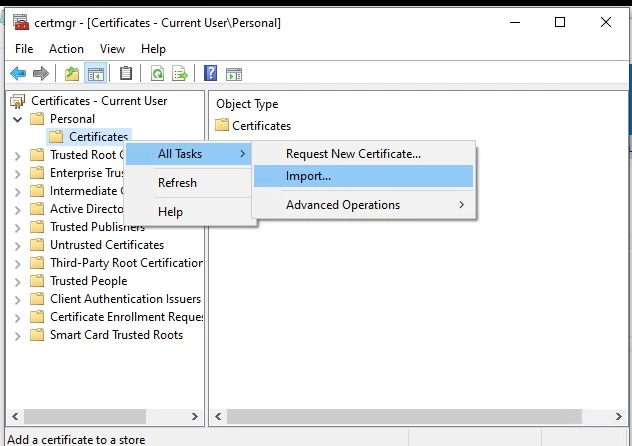
On the left pane, expand Personal -> Certificates - Right click over Certificates -> All Tasks -> Import.
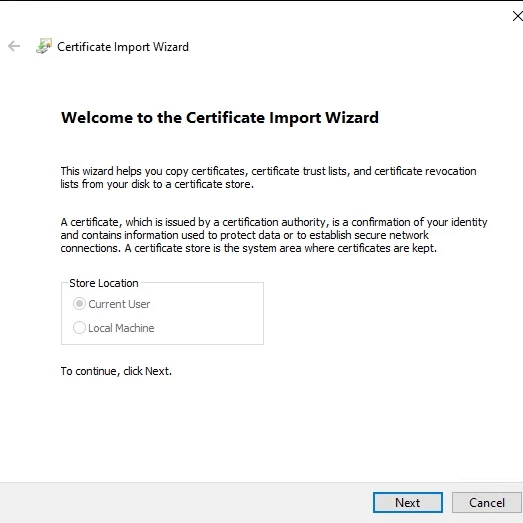
Select the Next button:
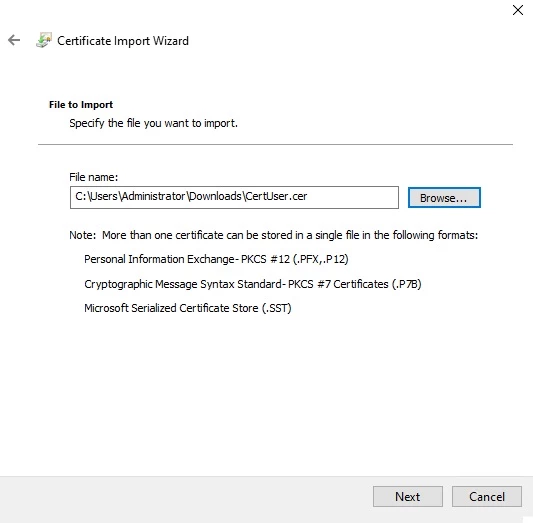
Select the Browse button and navigate to the folder that contains the user certificate file, select the Open button, and select the Next button.
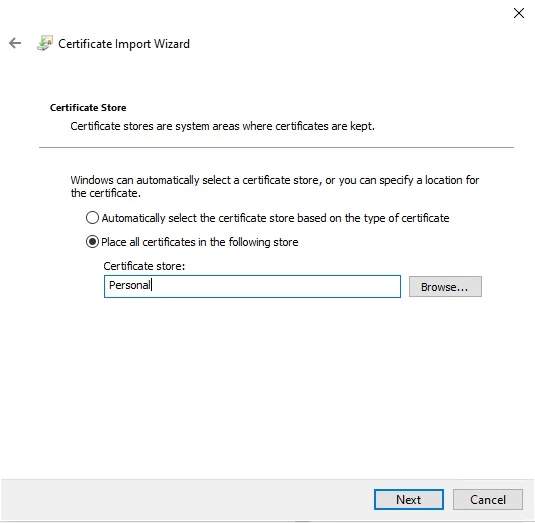
Place this user certificate in the user certificate store:
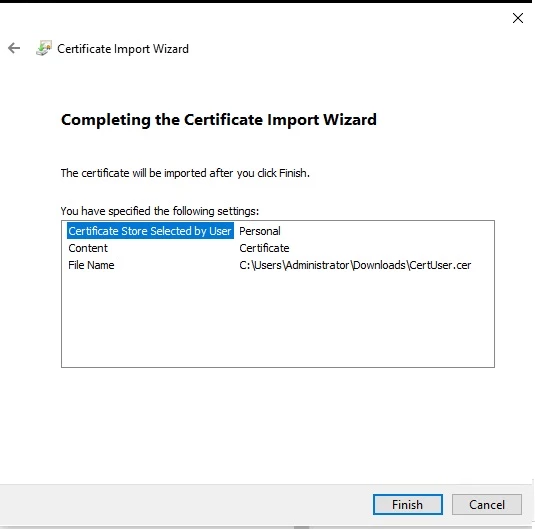
Select the Finish button:
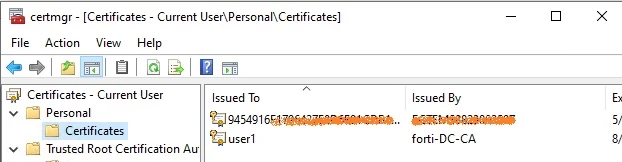
The user certificate must appear in the Certificates folder:
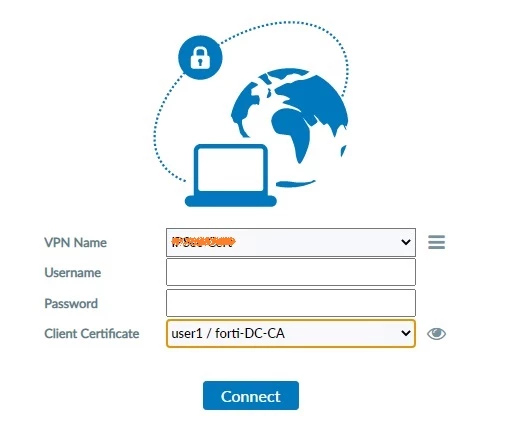
This certificate can be selected on FortiClient to negotiate VPN:
Related article:
Technical Tip: PKI peer user/usergroup creation for certificate authentication


