Technical Tip: Filter client certificates in FortiClient
| Description | This article describes how to configure the certificate filter to show only the matched subject and issuer. |
| Scope | FortiClient v7.0. |
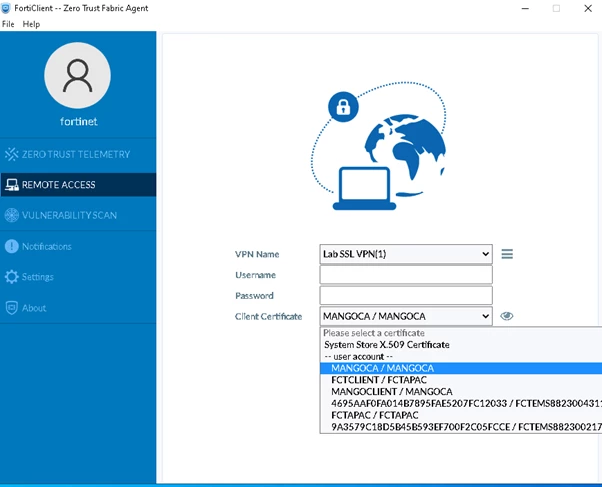
| Solution | Sometimes, in the endpoint, there might be many client certificates available in the personal certificate store, and it could be tedious for the end user to know which client certificate to select to establish a VPN tunnel.
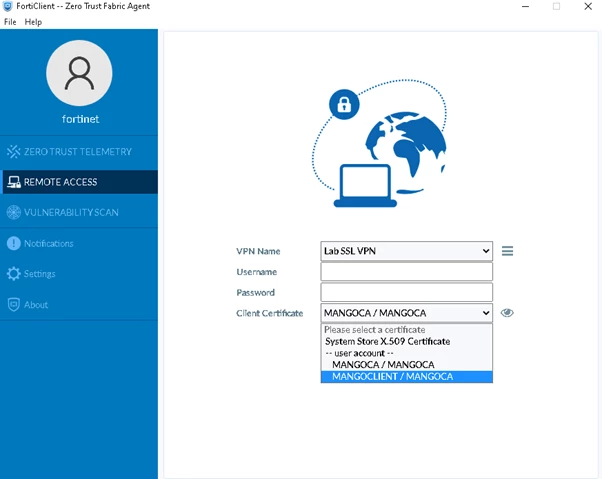
It is possible to use an XML certificate tag to filter based on the common name and issuer. For instance, if it is desired to filter to only show certificates issued by MANGOCA, include the following XML tags:
To filter only client certificates issued by MANGOCA, include the following XML code:
SSL VPN:
<sslvpn> <connections> <connection> <name>Lab SSL VPN</name> <certificate> </connection> </connections> </sslvpn>
IPsec VPN:
<ike_settings> <auth_data> <certificate> </auth_data> </ike_settings>
Results:
|