



Technical Tip: Enable Communication to FortiClient EMS from the FortiGate through an IPsec VPN tunnel
Description
This article describes how to connect to a FortiClient EMS over an IPsec VPN tunnel.
Scope
FortiClient EMS.
Solution
Assume that the site-to-site IPsec VPN tunnel is up, and the traffic can pass through as expected.
Adding the FortiClient EMS.
- Go to Security Fabric -> Fabric Connectors and select 'Create New'.
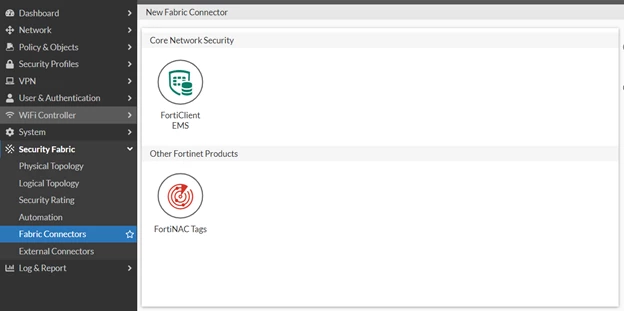
- Select FortiClient EMS.
- Fill out the Name and IP/Domain name and the HTTPS port and select 'OK'. 3. Even though the server is added, it is not reflected as connected in the status.
- Open the CLI and modify the 'source-ip' configuration for FortiClient EMS, by executing the following commands:
config endpoint-control fctems
edit NAME of your EMS
set source-ip X.X.X.X
end
Note: 'X.X.X.X' must be a FortiGate interface IP address, whose subnet is added in IPsec tunnel phase-2 local subnet settings in both locations.
While configuring the source IP setting for the EMS connector in the VDOM mode, we need to configure it in the global mode:
config global
config endpoint-control fctems
edit xxxx <----- EMS ID in order (1 - 7) EMS ID is basically the EMS connector 1,2.....
set source-ip X.X.X.X
end
end
- Fabric Connector for the FortiClient EMS should now be green and up.
- If the connector is not coming up, perform the troubleshooting procedure described in Troubleshooting Tip: Troubleshooting FortiGate with EMS.


