js2
Staff
Staff
January 19, 2026

Troubleshooting Tip: Token prompt not received for IPsec dial up VPN and EAP password failure error received

  • January 19, 2026
  • 0 replies
  • 2802 views
Description This article describes a use case where, after enabling IKEv2, the user authentication fails with the error 'EAP password failure'.
Scope FortiGate, FortiAuthenticator.
Solution

In this use case, the setup works as expected with PAP using IKEv1. However, in IKEv2, MS-CHAPv2 will be used.


Debugs to be checked:

FortiClient debug: Log Level -> Debug.


IPsec debug from FortiGate:


diagnose debug console timestamp enable

diagnose vpn ike log filter rem-addr4 <remote_side_publicIP>
diagnose debug application ike -1
diagnose debug application fnbamd -1
diagnose debug application eap_proxy -1
diagnose debug enable


To disable the debug after testing:


diagnose debug disable
diagnose vpn ike log filter clear
diagnose debug reset


FortiAuthenticator debug:


https://<FAC IP>/debug/radius/ 


For detailed debug logs, it is better to use https://<FAC IP>/debug/. Navigate to Log Category -> RADIUS to see Authentication, Accounting, Accounting monitors logs.

Note: RADIUS debug is disabled by default starting firmware version 6.5. It must be enabled by selecting 'Enter debug mode'. Detailed debug can then be enabled by selecting 'Enter detail debug mode'. Debug mode is disabled after manually disabling it or rebooting FortiAuthenticator.


From FortiAuthenticator debug, it can be observed that a challenge message is sent, but no response is received. In the user PC, an EAP password error is received.


2026-01-02T03:47:22.824653-08:00 FortiAuthenticator radiusd[30624]: (4) eap: EAP session adding &reply:State = 0x22a6ecd322a7eaff
2026-01-02T03:47:22.824656-08:00 FortiAuthenticator radiusd[30624]: (4)     [eap] = handled
2026-01-02T03:47:22.824659-08:00 FortiAuthenticator radiusd[30624]: (4)   } # authenticate = handled
2026-01-02T03:47:22.824666-08:00 FortiAuthenticator radiusd[30624]: (4) Using Post-Auth-Type Challenge
2026-01-02T03:47:22.824674-08:00 FortiAuthenticator radiusd[30624]: (4) # Executing group from file /usr/etc/raddb/sites-enabled/default
2026-01-02T03:47:22.824677-08:00 FortiAuthenticator radiusd[30624]: (4)   Challenge { ... } # empty sub-section is ignored
2026-01-02T03:47:22.824691-08:00 FortiAuthenticator radiusd[30624]: (4) Sent Access-Challenge Id 55 from 0.0.0.0:2083 to 10.103.195.177:32982 length 73
2026-01-02T03:47:22.824694-08:00 FortiAuthenticator radiusd[30624]: (4)   EAP-Message = 0x0101000f0650617373776f72643a20
2026-01-02T03:47:22.824697-08:00 FortiAuthenticator radiusd[30624]: (4)   Message-Authenticator = 0x00000000000000000000000000000000
2026-01-02T03:47:22.824700-08:00 FortiAuthenticator radiusd[30624]: (4)   State = 0x22a6ecd322a7eaff47a4e2b3faa55d19
2026-01-02T03:47:22.824720-08:00 FortiAuthenticator radiusd[30624]: (0) (TLS) send TLS 1.3 Handshake, Finished
2026-01-02T03:47:22.824755-08:00 FortiAuthenticator radiusd[30624]: (4) Finished request


Solution:

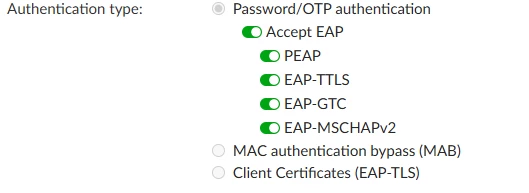
Step 1: Ensure EAP is enabled in the RADIUS policy: 


Screenshot 2026-01-19 155939.png


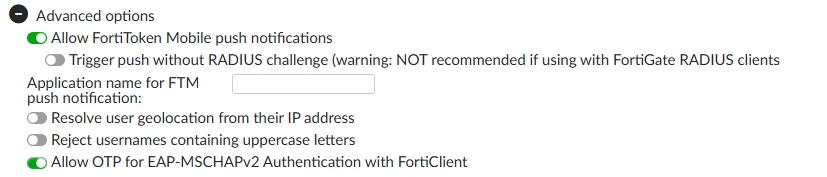
In the RADIUS policy, under Advanced Options, enable 'Allow OTP for EAP-MSCHAPv2 Authentication with FortiClient'.


Screenshot 2026-01-19 160055.png


Step 2: 

Configure it using the <eap_method> option in the FortiClient's XML configuration:

In <ike_settings>, add the following line:


 <ike_settings>
<authentication_method>Preshared Key</authentication_method>
<eap_method>1</eap_method>
</ike_settings>
</connection>
</connections>
</ipsecvpn>
</vpn>
</forticlient_configuration>


Using 1, authentication is performed using EAP-MSCHAPv2.


Note:

Verify that the FortiAuthenticator domain join is successful. If successful, the connection should show as 'joined domain, connected' under Monitor -> Authentication -> Windows AD.

Additionally, in the RADIUS Policy under Authentication -> RADIUS Service -> Policies -> Identity Sources, verify that the option 'Use Windows AD Domain Authentication' is enabled. 


Related documents:

Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!