Solution | Logging into the PC displays the message: Offline Tokens: None available.
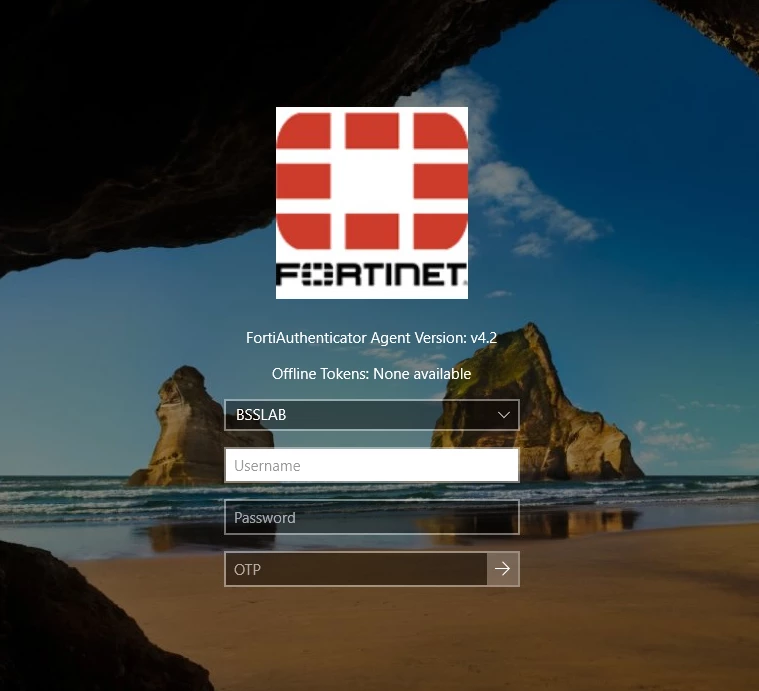 The following error entries are observed in the FortiAuthenticator agent logs:
2026-02-16 12:06:36,153 [15612|14|DEBUG] : [Credential.cpp:2496] Credential::FetchOfflineTokens: Sending FetchOfflineOTPRequest to service
2026-02-16 12:06:36,187 [15612|15|DEBUG] FAC_Agent.Service.Impl: Processing FetchOfflineOTPRequest for BSSLAB\Likith
2026-02-16 12:06:36,215 [15612|15|DEBUG] TwoFactorAuthPlugin: FetchTokens: Received Domain: BSSLAB, username: likith
2026-02-16 12:06:36,279 [15612|15|DEBUG] TwoFactorAuthPlugin: Fetching tokens, next update time was 02/16/2026 06:36:35 UTC
2026-02-16 12:06:36,295 [15612|15|INFO ] TwoFactorAuthenticator: Requesting tokens for user (likith) realm (BSSLAB) starting at: UTC 16-02-2026 06:36:36
2026-02-16 12:06:36,329 [15612|15|DEBUG] TwoFactorAuthenticator: Authenticate input pars: subj name: FAC-VM0A12001111, host: 10.18.4.22, nretries: 3, timeout: 5, allow_on_fail: Block, verifycert: False, certfile: C:\Program Files\Fortinet\fortinet_ca.crt, admin name: ldapadmin, offline tokens: enabled, Preferred Server
2026-02-16 12:06:36,357 [15612|15|DEBUG] RestAPI: Initializing RestApi hostname: FAC-VM0A12001111, host: 10.18.4.22, verifyCert: False, admin: rdpadmin
2026-02-16 12:06:36,387 [15612|15|INFO ] RestAPI: GetOfflineTokens queued asynchronously
2026-02-16 12:06:36,451 [15612|16|DEBUG] : [Credential.cpp:2425] Credential::FetchEmergencyToken: Sending EmergencyTokenRequest to service
2026-02-16 12:06:36,467 [15612| 4|ERROR] RestAPI: An unexpected exception occurred while opening an SSL stream: Authentication failed because the remote party has closed the transport stream.
2026-02-16 12:06:36,499 [15612| 4|ERROR] RestAPI: Cannot create SSL stream
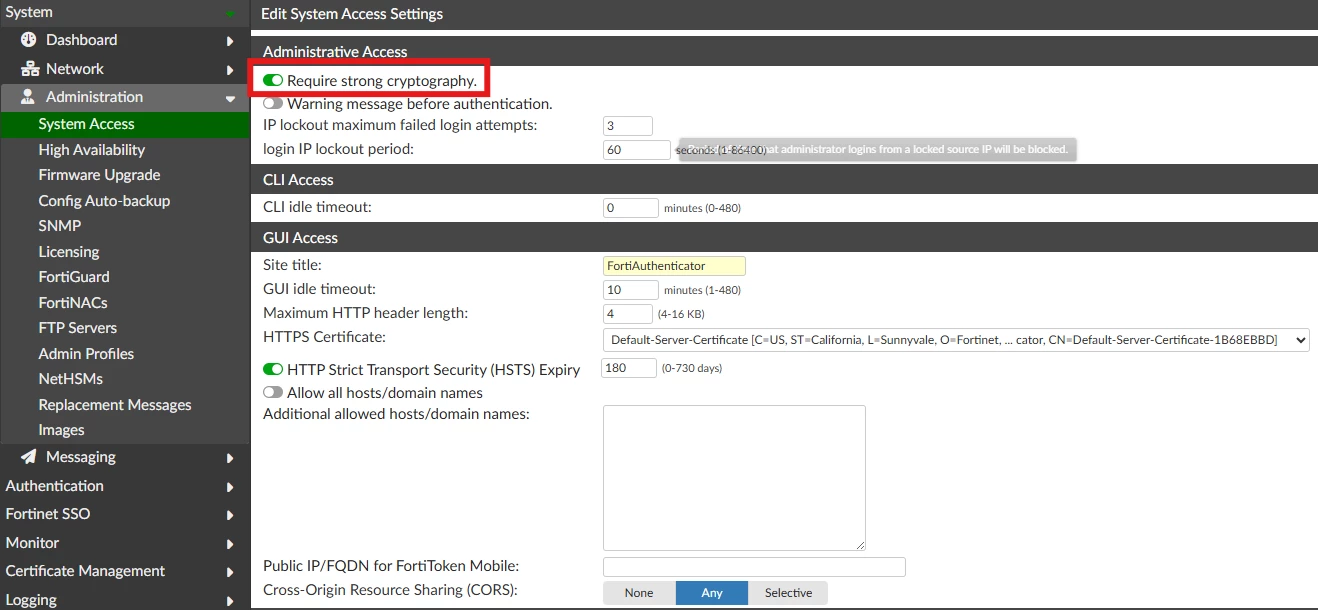
To resolve this issue, enable the Require strong cryptography option in FortiAuthenticator by following the steps below:
Log in to FortiAuthenticator, navigate to System -> Administration -> System Access, and enable the Require strong cryptography option.
After applying the changes, log in twice on the agent using the appropriate credentials and the regular FortiToken while the device is connected to the network, as the FortiAuthenticator Agent needs to retrieve the offline tokens when the FortiAuthenticator is reachable.
Disconnect the PC from the network and sign out. Upon signing in again, the offline FortiToken should be available to login.
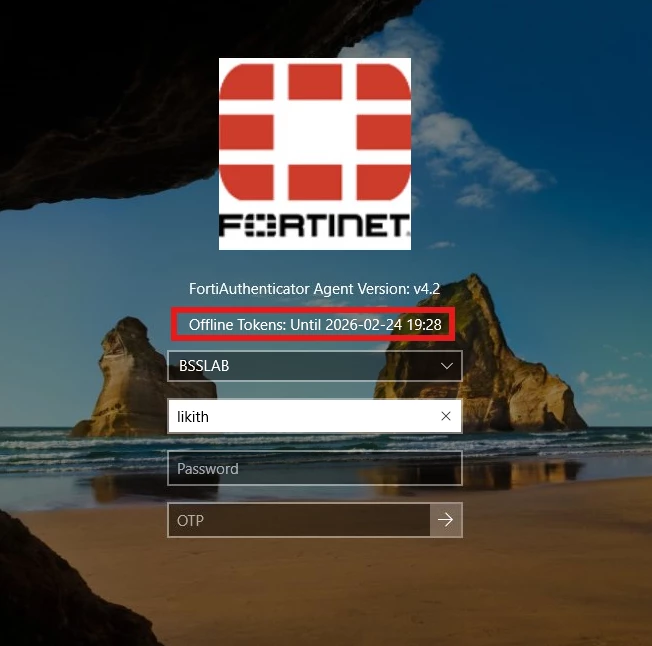
Note: To verify if offline tokens were synced, go to C:\Program Files\Fortinet\FortiAuthenticator Agent\Offline, then there should be a folder with the name of the realm, and into it a folder with the name of the user that contains offline tokens.
Related article:
Technical Tip: FortiAuthenticator, offline tokens not working on Windows agent |