Troubleshooting tip: RADIUS Authentication Failure on FortiAuthenticator When NTLM v1 is Disabled on LDAP Server
| Description | This article describes a solution to resolve the issue of RADIUS authentication failure, when NTLM v1 is disabled on a Windows Server (LDAP server), RADIUS authentication may fail between FortiGate and FortiAuthenticator and LDAP server. |
| Scope | FortiGate, FortiAuthenticator. |
| Solution | When NTLM v1 is disabled, and the RADIUS protocol on FortiGate radius settings is set as MSCHAPv2, the authentication will fail because MSCHAPV2 uses NTLM v1.
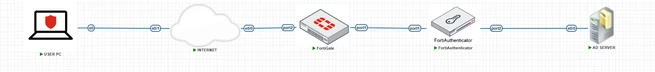
In the topology below, a FortiClient user connecting to FortiGate and FortiGate is using FortiAuthenticator as a RADIUS server for user authentication and FortiAuthenticator is authenticating the users stored on the LDAP server.
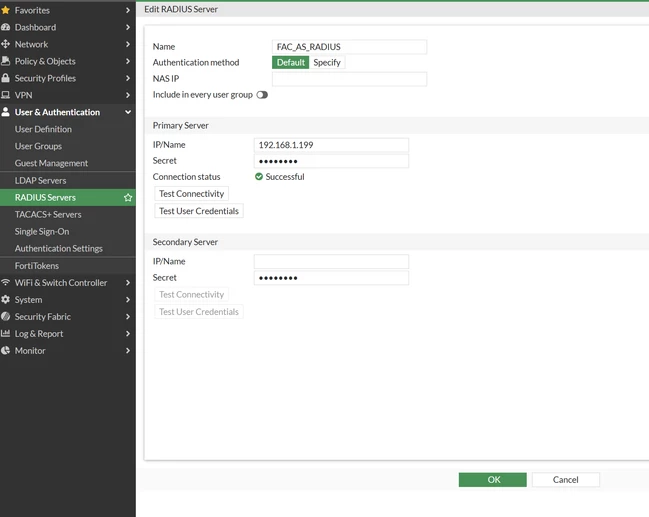
Following config changes are required on FortiGate:
Related document: |