When configuring a remote LDAP server in FortiAuthenticator, the LDAP query elements determine which LDAP objects are treated as users and which attribute is used as the username.
Consider an LDAP group using the groupOfUniqueNames object class with multiple values in the uniqueMember attribute:
dn: cn=LDAP-Test-Group,ou=groups,dc=example,dc=com
objectClass: groupOfUniqueNames
cn: LDAP-Test-Group
uniqueMember: uid=user1,ou=people,dc=example,dc=com
uniqueMember: uid=user2,ou=people,dc=example,dc=com
uniqueMember: uid=user3,ou=people,dc=example,dc=com
If the FortiAuthenticator LDAP query elements are configured as follows:
User object class: groupOfUniqueNames
Username attribute: uniqueMember
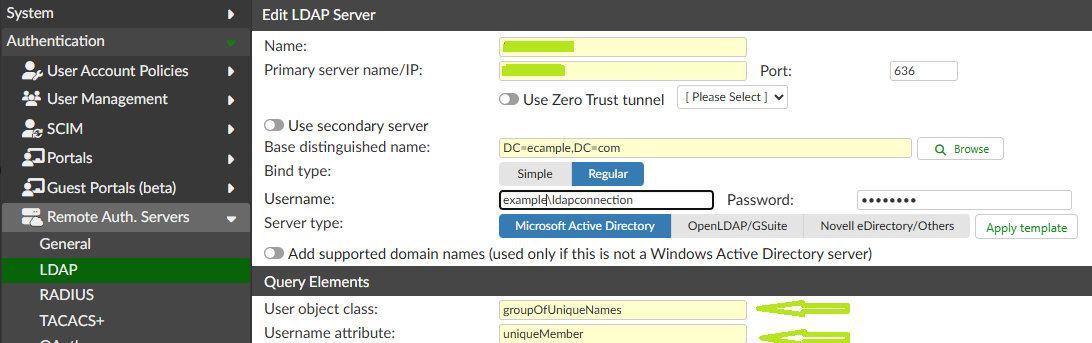
FortiAuthenticator searches for groupOfUniqueNames objects as user objects.
The uniqueMember attribute is a multi-valued group membership attribute. A single LDAP group can therefore contain multiple uniqueMember values.
With this configuration, the LDAP group is identified as a single user object, while all values of the uniqueMember attribute are used for the username. As a result, multiple member DNs may appear together as a single remote LDAP user in FortiAuthenticator.
For example:
uid=user1,ou=people,dc=example,dc=com,
uid=user2,ou=people,dc=example,dc=com,
uid=user3,ou=people,dc=example,dc=com
This does not indicate that the LDAP server is returning the individual users as a single LDAP entry. The LDAP server returns one group entry containing multiple values for the uniqueMember attribute.
To import the users individually, verify the LDAP schema of an individual user entry.
For example:
dn: uid=user1,ou=people,dc=example,dc=com
objectClass: person
uid: user1
cn: User One
sn: One
In this example, configure the LDAP query elements to use the individual user object class and username attribute:
User object class: person
Username attribute: uid
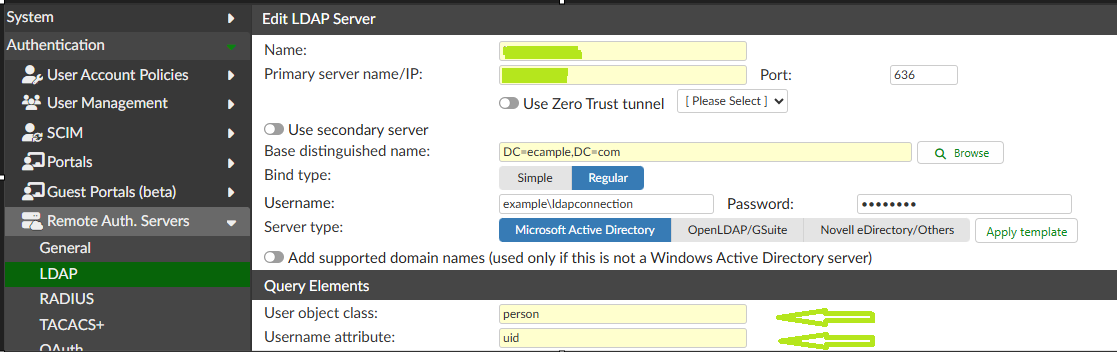
If group membership information is available through an attribute on the user object, configure the applicable user group membership attribute according to the LDAP schema.
For example, if the LDAP user entry contains:
isMemberOf: cn=LDAP-Test-Group,ou=groups,dc=example,dc=com
The corresponding configuration can use:
Obtain group memberships from: User attribute
Group membership attribute: isMemberOf
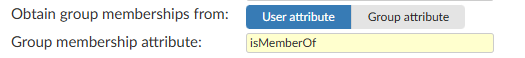
After correcting the user object class and username attribute, FortiAuthenticator identifies the individual LDAP entries separately during remote user import.
For example:
user1
user2
user3
Important: The applicable user object class, username attribute, group object class, and group membership attributes depend on the LDAP directory schema. Verify the objectClass and username attributes of an individual LDAP user before configuring the LDAP query elements in FortiAuthenticator.
A group object class such as groupOfUniqueNames and a multi-valued membership attribute such as uniqueMember should not be configured as the user object class and username attribute when individual LDAP users need to be imported.
Related articles: | 




