| When both local and remote groups are configured, the local authentication does not work. From the FortiAuthenticator debug logs, it is possible to see that user information is being verified against the LDAP server instead of the local database. https://<FAC IP>/debug/radius/ 2025-01-04T06:14:58.585485-08:00 FortiAuthenticator radiusd[19006]: (43) User-Name = "user1"
2025-01-04T06:14:58.586524-08:00 FortiAuthenticator radiusd[19006]: User-Name = "user1"
2025-01-04T06:14:58.586853-08:00 FortiAuthenticator radiusd[19006]: (43) facauth: ===>Username:user1
2025-01-04T06:14:58.592837-08:00 FortiAuthenticator radiusd[19006]: (43) facauth: Input raw_username: (null) Realm: (null) username: user1
2025-01-04T06:14:58.595087-08:00 FortiAuthenticator radiusd[19006]: (43) facauth: Adding remote attribute to query for user user1: samAccountName
2025-01-04T06:14:58.595108-08:00 FortiAuthenticator radiusd[19006]: (43) facauth: Adding remote attribute to query for user user1: userPrincipalName
2025-01-04T06:14:58.595121-08:00 FortiAuthenticator radiusd[19006]: (43) facauth: Adding remote attribute to query for user user1: mail
2025-01-04T06:14:58.595133-08:00 FortiAuthenticator radiusd[19006]: (43) facauth: Adding remote attribute to query for user user1: displayName
2025-01-04T06:14:58.595144-08:00 FortiAuthenticator radiusd[19006]: (43) facauth: Adding remote attribute to query for user user1: objectGUID
2025-01-04T06:14:58.595157-08:00 FortiAuthenticator radiusd[19006]: (43) facauth: Adding remote attribute to query for user user1: mS-DS-ConsistencyGuid
2025-01-04T06:14:58.602575-08:00 FortiAuthenticator radiusd[19006]: (43) facauth: Try to search user by: (&(objectClass=person)(sAMAccountName=user1))
2025-01-04T06:14:58.604219-08:00 FortiAuthenticator radiusd[19006]: Warning: failed to search remote LDAP server for remote user 'user1', error: invalid user
2025-01-04T06:14:58.604236-08:00 FortiAuthenticator radiusd[19006]: (43) facauth: user: user1 not found, update user and ip lockout with ip: 10.107.3.131
2025-01-04T06:14:58.610652-08:00 FortiAuthenticator radiusd[19006]: (43) facauth: Updated auth log 'user1': Remote LDAP user authentication with no token failed: invalid user In the RADIUS policy where remote groups are configured, it is necessary to enable the 'Allow local users to override remote users' option and select the local user group. This configuration allows both local and remote users to connect to the VPN. 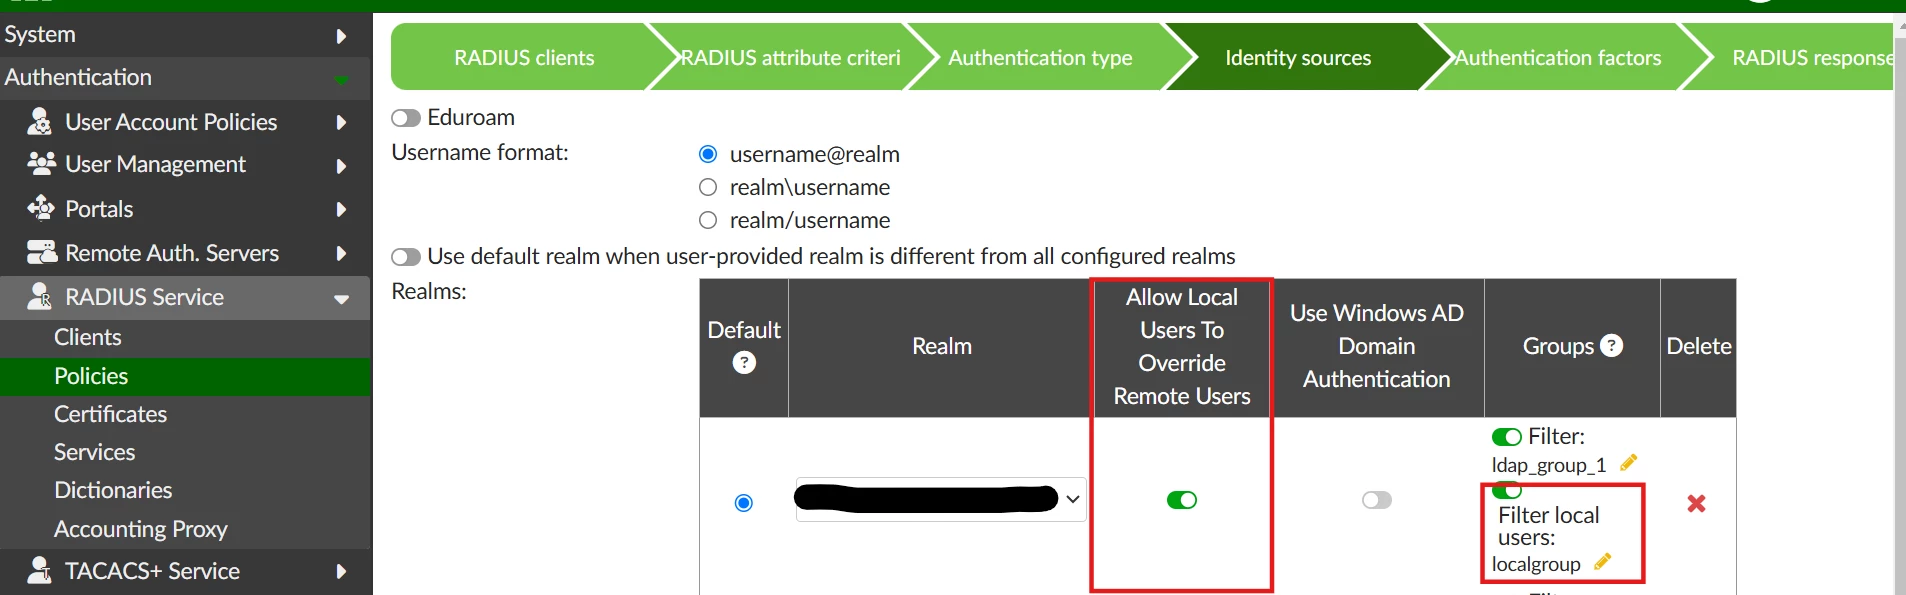
2025-01-04T06:13:39.041612-08:00 FortiAuthenticator radiusd[19006]: (42) User-Name = "user1"
2025-01-04T06:13:39.043817-08:00 FortiAuthenticator radiusd[19006]: User-Name = "user1"
2025-01-04T06:13:39.044368-08:00 FortiAuthenticator radiusd[19006]: (42) facauth: ===>Username:user1
2025-01-04T06:13:39.055651-08:00 FortiAuthenticator radiusd[19006]: (42) facauth: Input raw_username: (null) Realm: (null) username: user1
2025-01-04T06:13:39.060083-08:00 FortiAuthenticator radiusd[19006]: (42) facauth: Local user found: user1
2025-01-04T06:13:39.072761-08:00 FortiAuthenticator radiusd[19006]: (42) facauth: Updated auth log 'user1': Local user authentication with no token successful
2025-01-04T06:13:39.073045-08:00 FortiAuthenticator radiusd[19006]: (42) facauth: User-Name: user1 (from request) |